
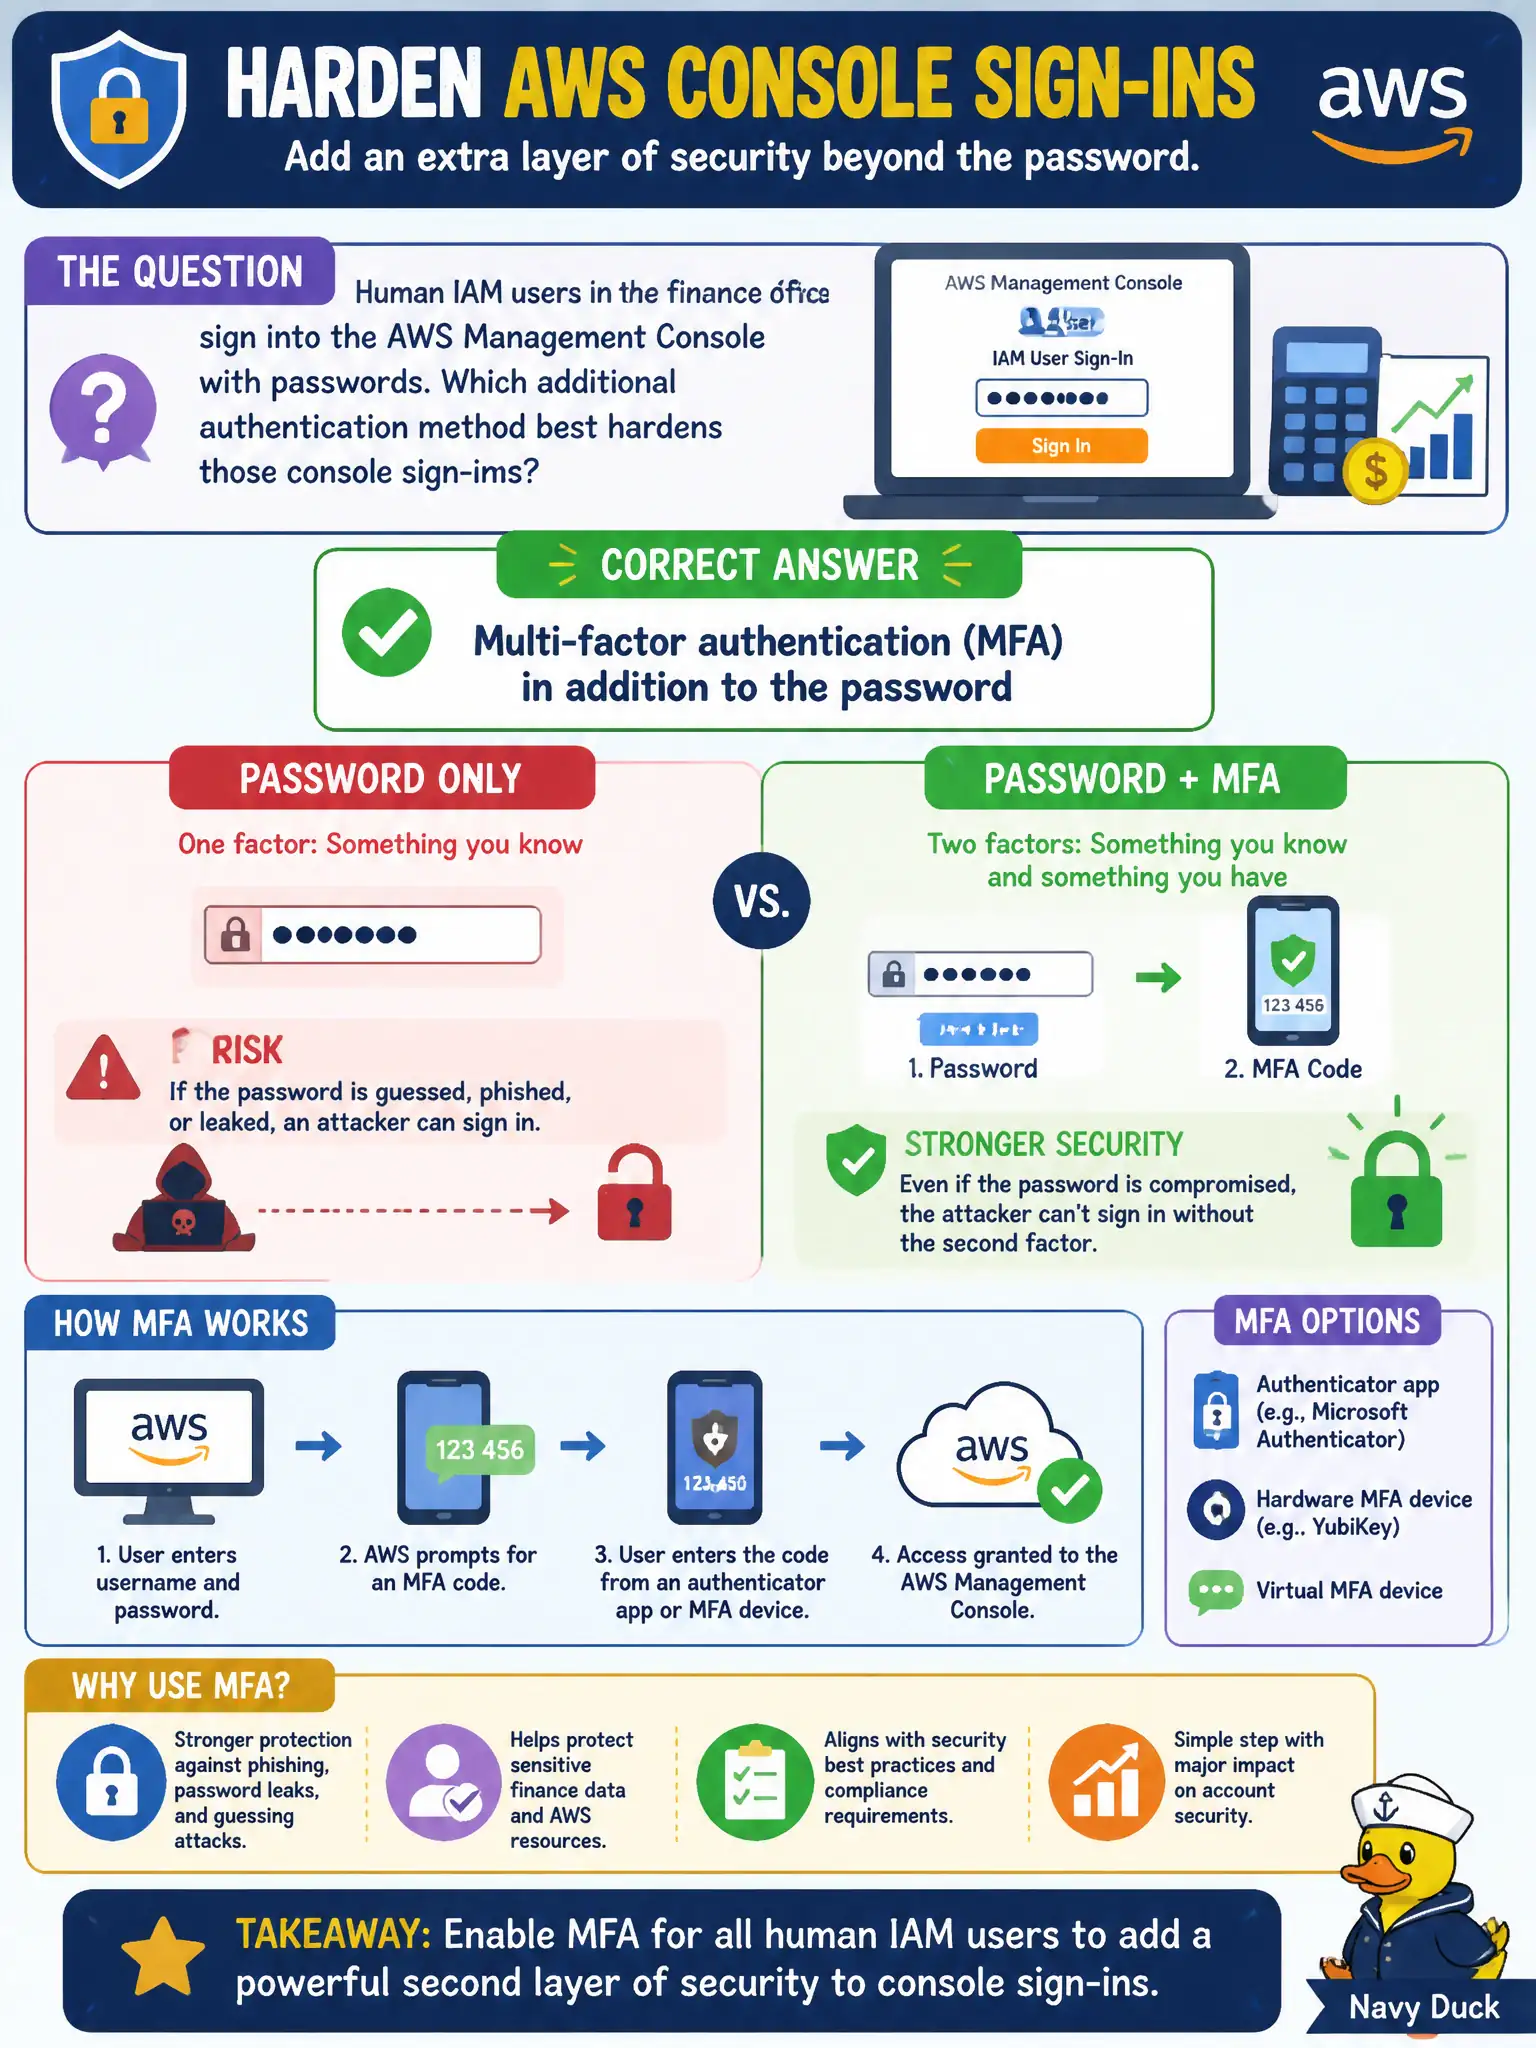
Human IAM users in the finance office sign into the AWS Management Console with passwords. Which additional authentication method best hardens those console sign-ins?
Select an answer to reveal the explanation.
Short Explanation
A password alone is one lock on the door; MFA adds a second factor — something you have, like a token or authenticator app. Even if the password leaks, the thief still needs that second factor to walk into the console.
Full Explanation
Multi-factor authentication (MFA) in addition to the password best hardens console sign-ins for human IAM users in the finance office. A password alone is one lock; MFA adds a second factor such as a token or authenticator app so a leaked password is not enough to walk into the console. Disabling CloudTrail so login events are not logged removes detection. Publishing the password policy to an anonymous S3 website does not harden authentication and may leak policy details unnecessarily. Granting AdministratorAccess to every finance user by default increases blast radius instead of hardening sign-in. Distractors fail by weakening logging, by confusing documentation with authentication strength, or by over-privileging users. Exam caveat: MFA is the classic first hardening step for password-based console access and is especially important for privileged finance and admin personas. Operational check: require MFA for all human console users, prioritize finance and IAM admins, monitor for console logins without MFA where detectable, keep CloudTrail enabled, and avoid trading MFA away for convenience during budget season. In practice, make MFA mandatory for finance console users before month-end close, track enrollment completion, and keep CloudTrail enabled to evidence hardened sign-ins.