
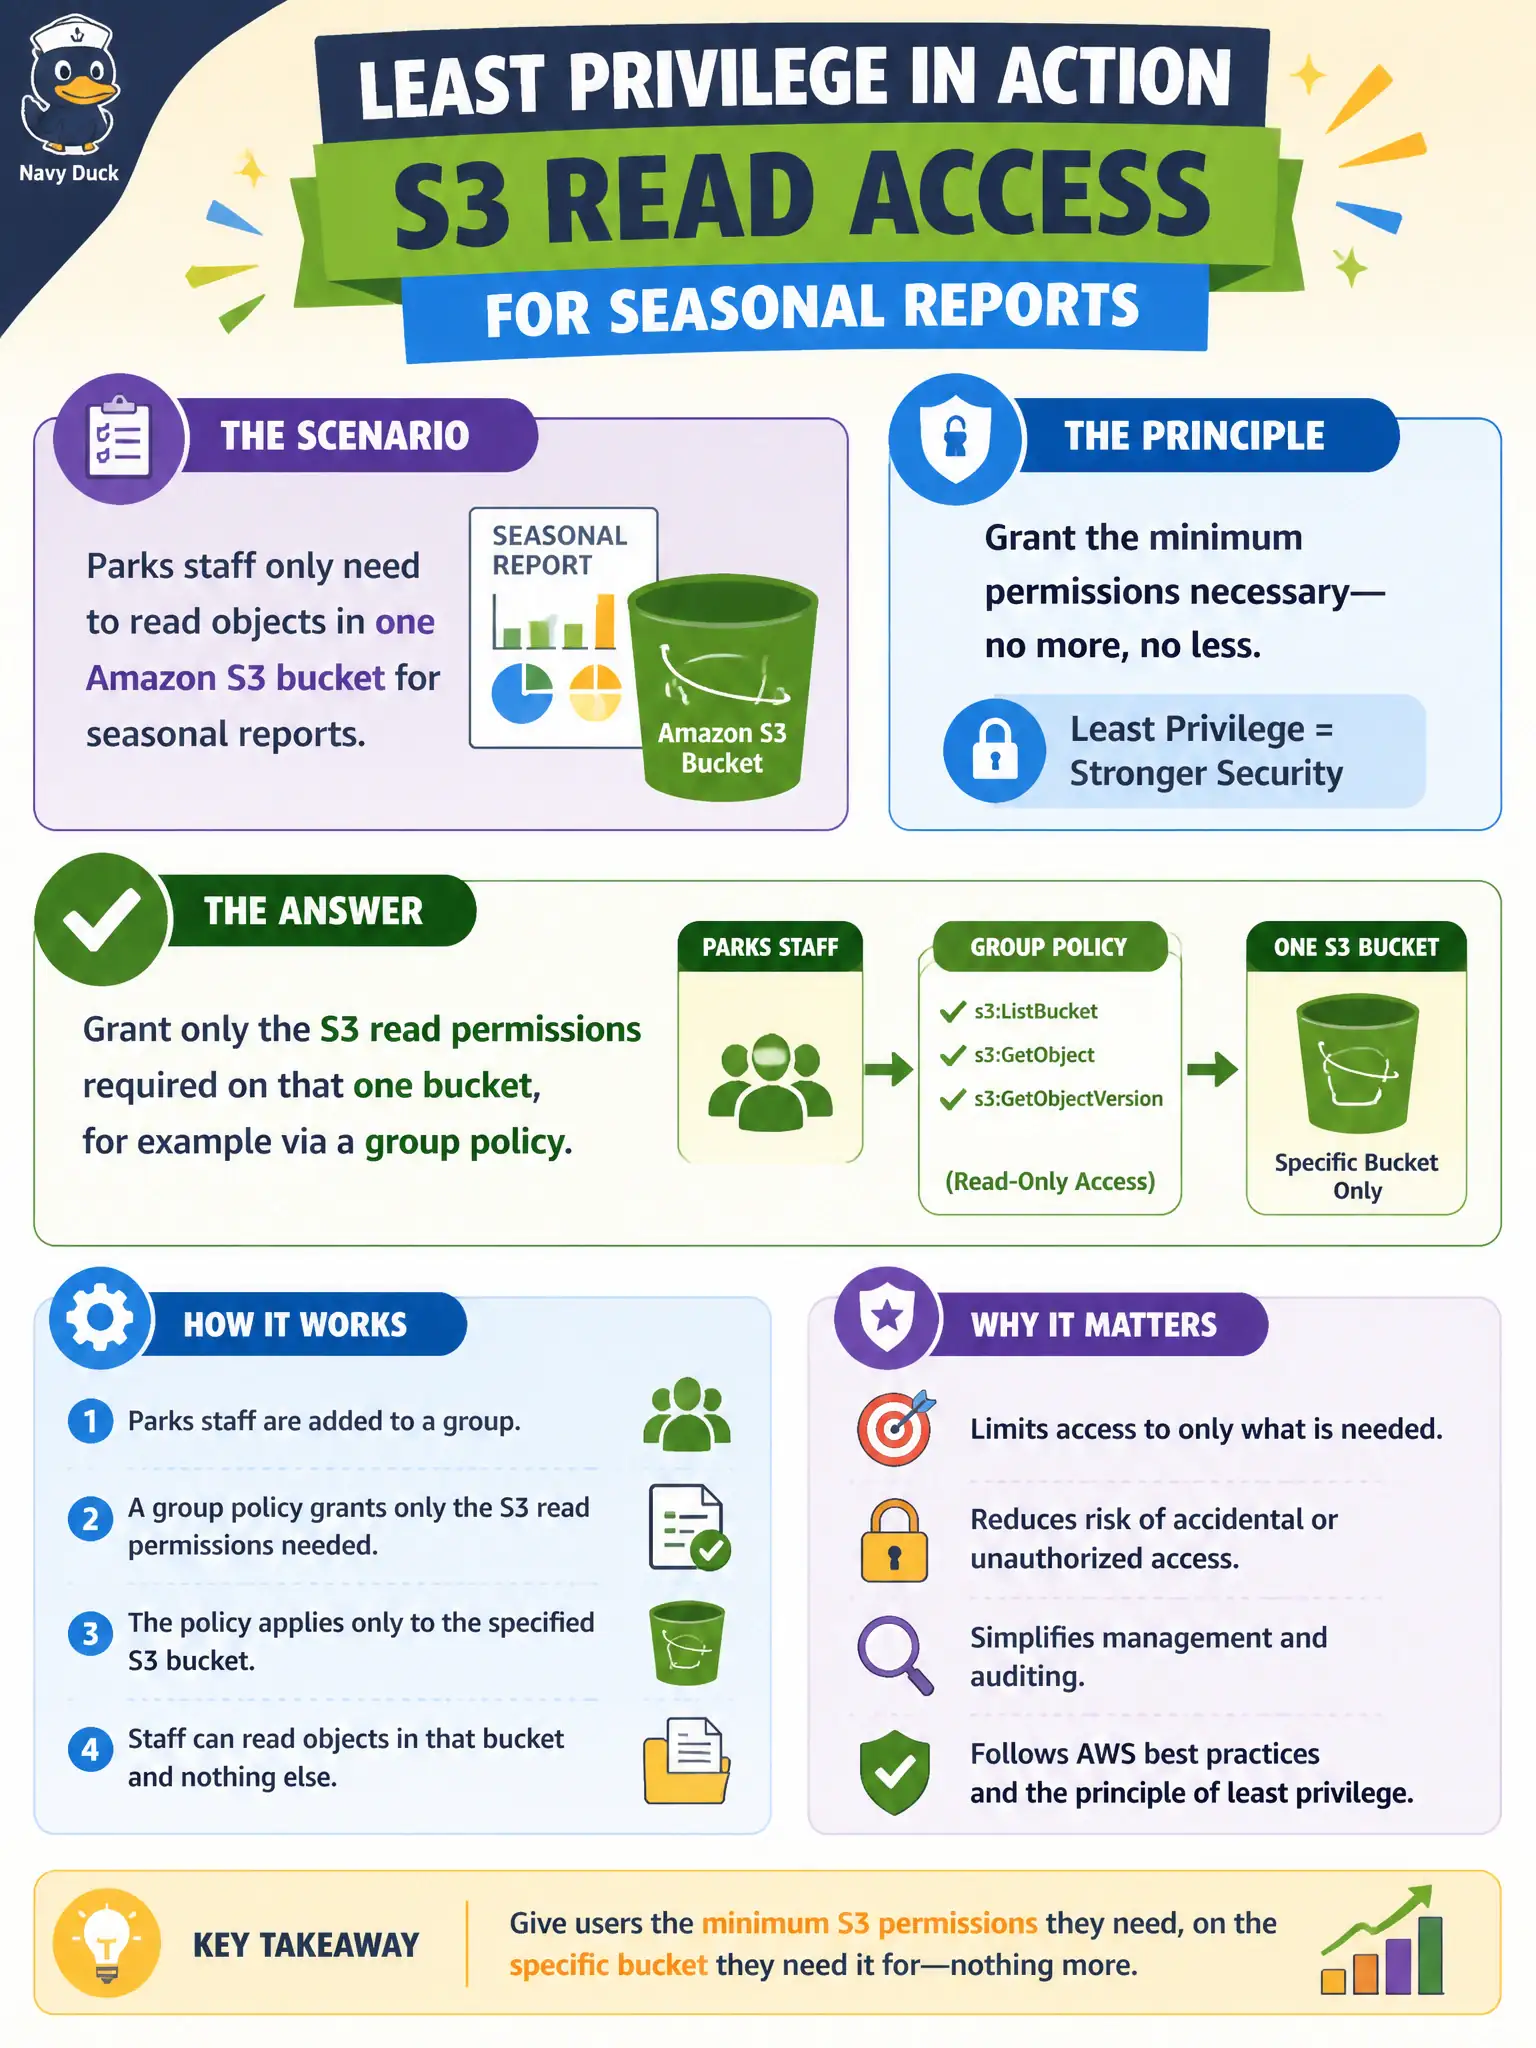
Parks staff only need to read objects in one Amazon S3 bucket for seasonal reports. How should permissions be granted under the principle of least privilege?
Select an answer to reveal the explanation.
Short Explanation
Least privilege means handing someone the key to one filing cabinet drawer — not the entire city hall master ring. Parks readers get S3 read on that bucket, not admin on everything. Broad AdministratorAccess or root sharing is the opposite pattern.
Full Explanation
Under least privilege, parks staff who only need to read objects in one Amazon S3 bucket should receive only the S3 read permissions required on that bucket — for example via a group policy — not AdministratorAccess on everything. Least privilege means handing someone the key to one filing cabinet drawer, not the entire city hall master ring. Attaching AdministratorAccess to every parks IAM user for simplicity is the opposite pattern. Sharing the account root user with seasonal crew is dangerous and unnecessary. Granting s3:* on all buckets in all accounts to avoid ticket delays vastly over-scopes access. Distractors fail by maximizing privileges for convenience rather than matching the read-only reporting job. Exam caveat: broad managed policies can be starting points, but exam answers that grant admin or root for a narrow read need are almost always wrong. Operational check: place parks readers in an IAM group, attach a policy allowing s3:GetObject (and list if required) on the specific bucket ARN, deny or omit write/delete, review membership each season, and verify CloudTrail shows only expected GetObject calls from that group. In practice, write the parks policy with explicit bucket ARNs, attach it through a group, and dry-run Access Denied for write calls to prove least privilege before season start.