
Compared with designing a bespoke on-premises HSM project from scratch, what Cloud Practitioner-level benefit of AWS cloud security is most accurate regarding encryption?
Select an answer to reveal the explanation.
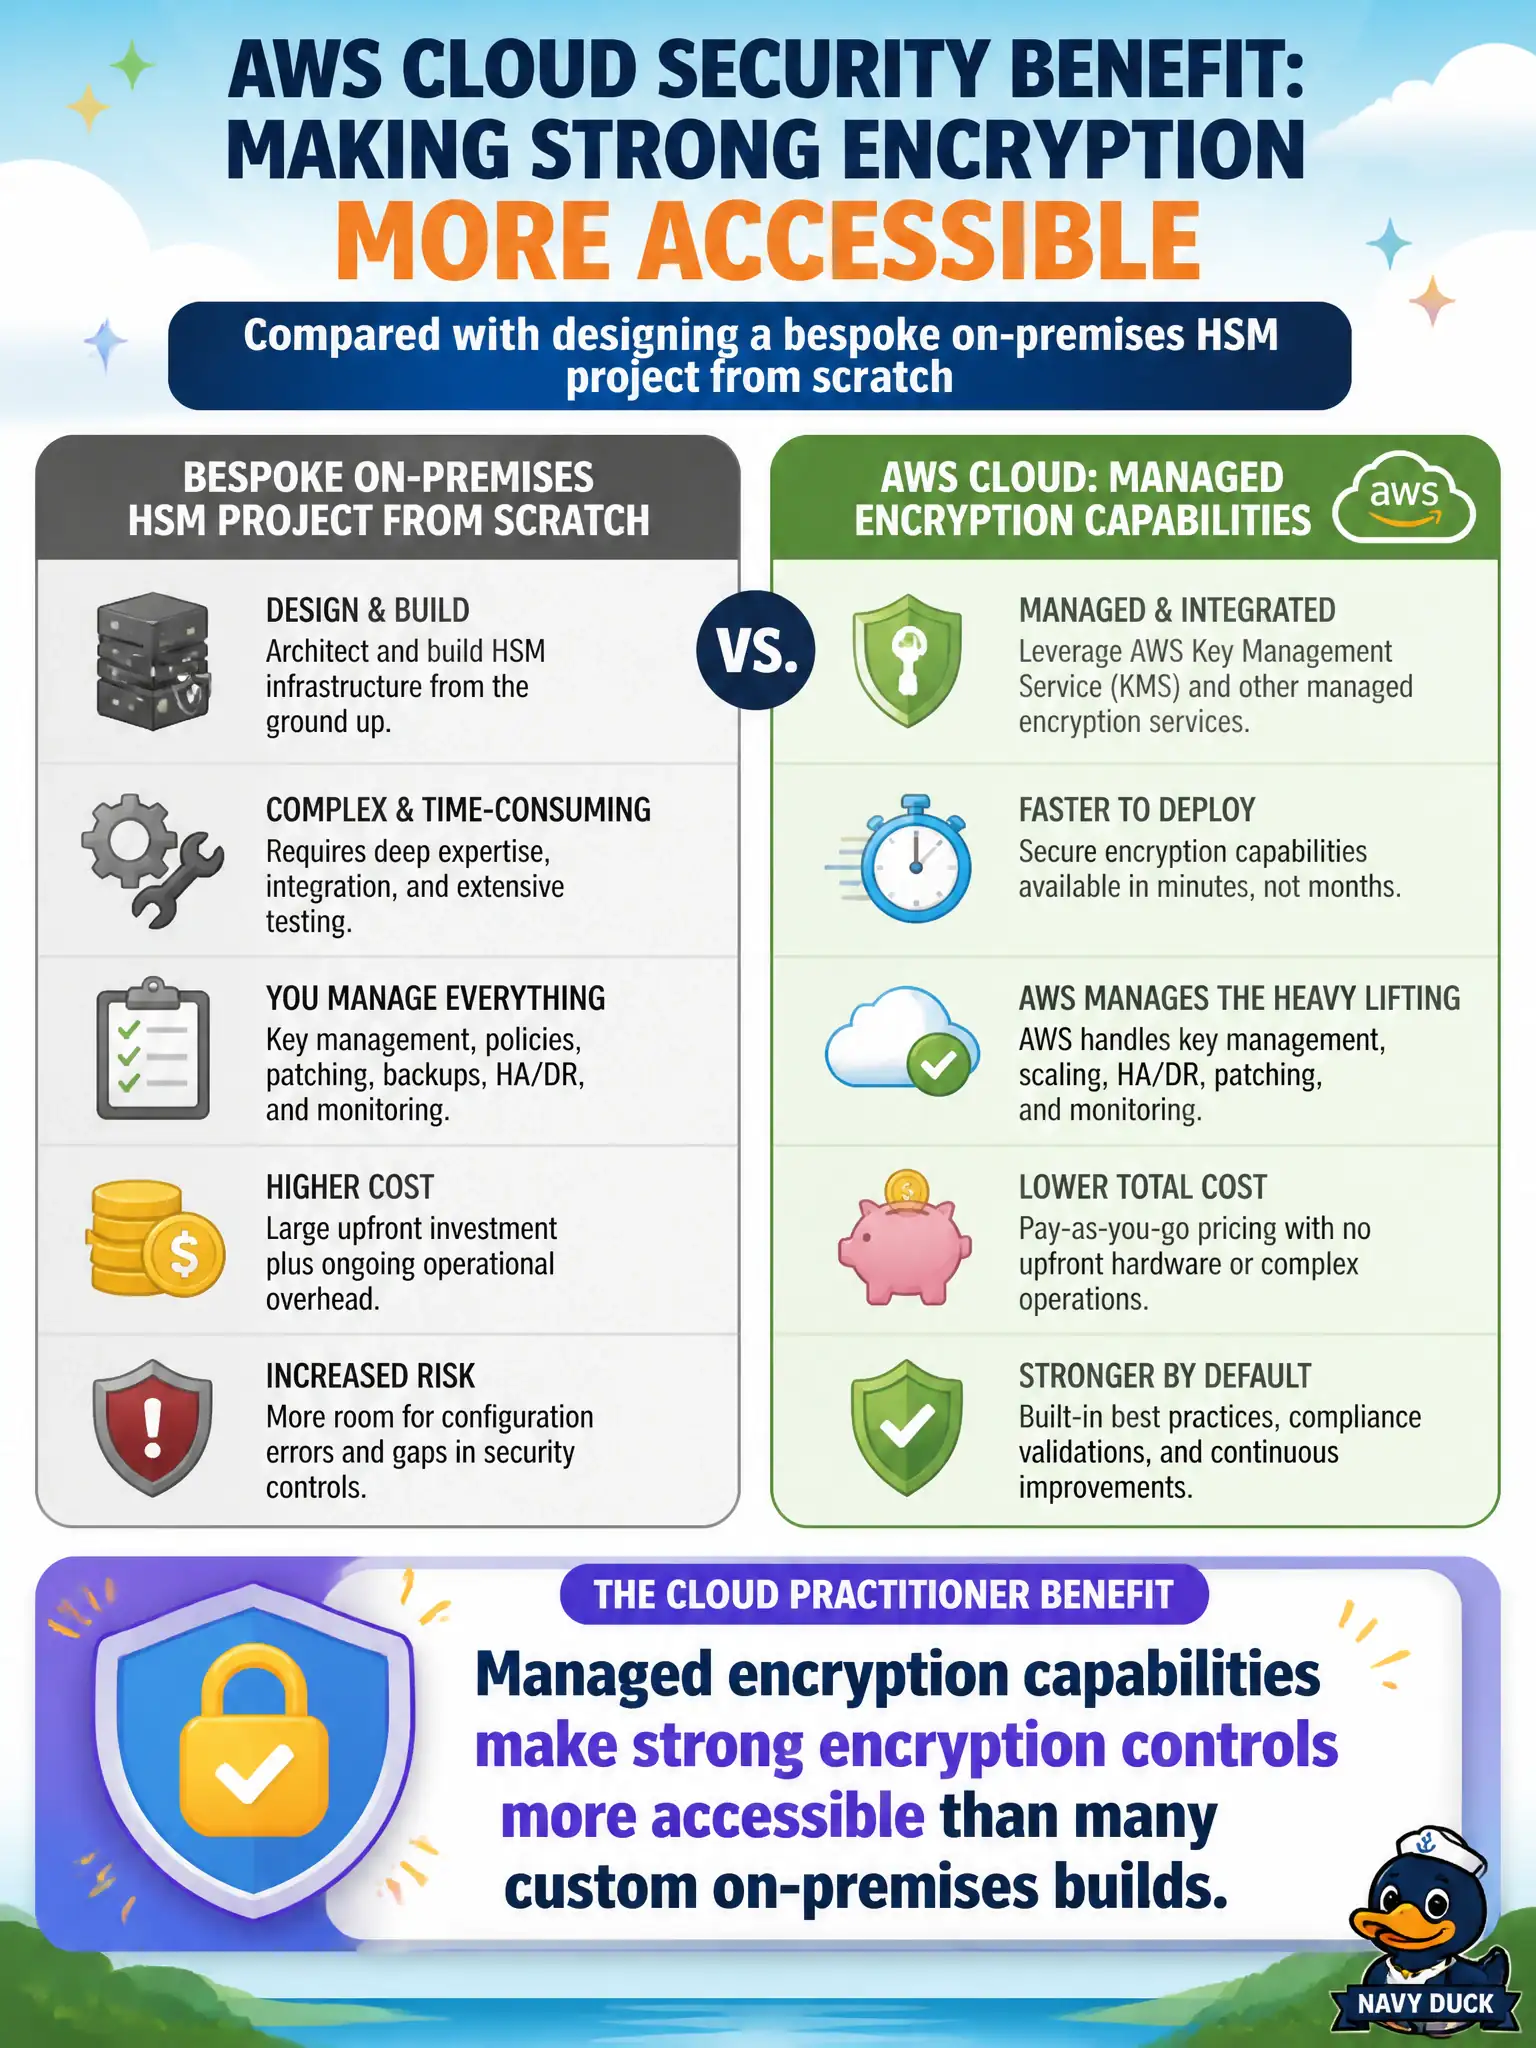
Short Explanation
On-prem HSM projects can feel like building a bank vault with hand tools; AWS managed encryption services put strong locks within reach of a city IT team without inventing crypto from scratch. That accessibility is the benefit — not a myth that responsibility or physics disappear.
Full Explanation
Compared with designing a bespoke on-premises HSM project from scratch, a Cloud Practitioner-accurate benefit is that managed encryption capabilities on AWS make strong encryption controls more accessible than many custom builds. On-prem HSM projects can feel like building a bank vault with hand tools; AWS managed encryption services put strong locks within reach of a city IT team without inventing cryptography from scratch. That accessibility is the benefit — not a myth that AWS removes all customer responsibility for protecting data, that encryption is unnecessary because Regions are physically impossible to breach, or that customers must invent their own TLS protocol before any AWS API call succeeds. Distractors fail by erasing shared responsibility, by denying the need for encryption, or by inventing a DIY TLS prerequisite. Exam caveat: using KMS, SSL/TLS terminations, and service encryption features still leaves key policy, enablement, and data-classification decisions with the customer. Operational check: standardize on managed encryption services for municipal data stores, require encryption at rest and in transit in architecture standards, review key policies quarterly, and avoid one-off custom crypto projects unless a clear gap remains.