
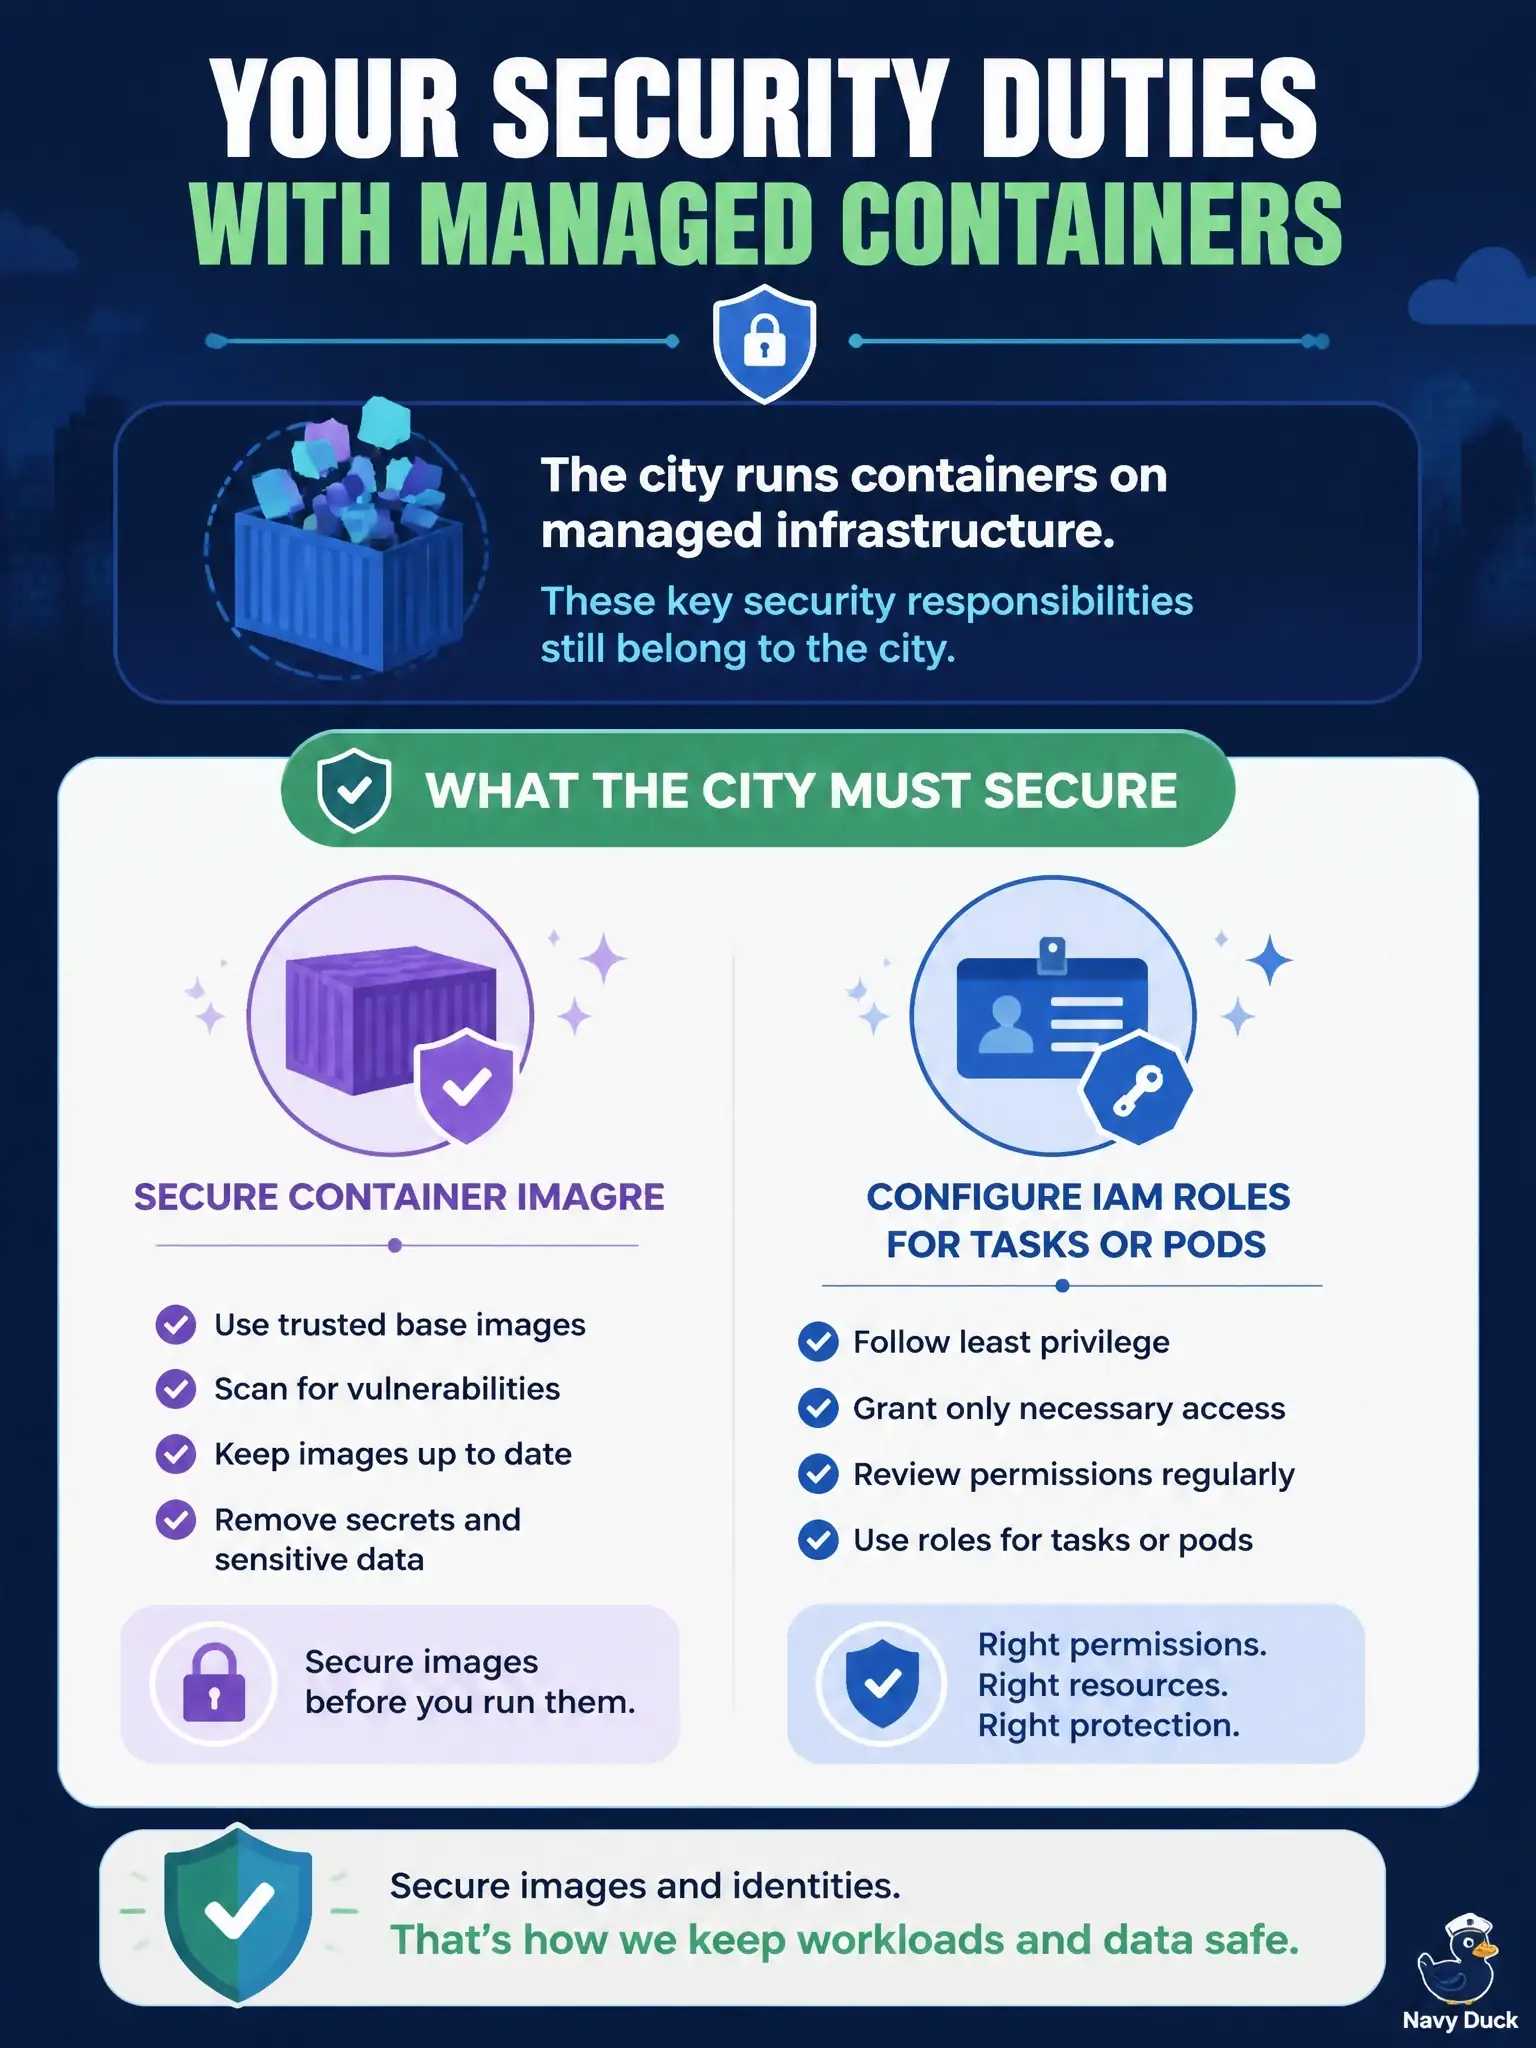
The city runs containers on managed Amazon ECS or Amazon EKS. Which customer security duties still apply?
Select an answer to reveal the explanation.
Short Explanation
A managed container platform isn't a free pass to ship mystery images with admin keys baked in. You still harden images and set task or pod IAM roles carefully. "Managed" shifts cluster chores; it doesn't erase image and identity hygiene.
Full Explanation
Even on managed container platforms, the city must still secure container images and configure IAM roles used by tasks or pods. Managed services can shift cluster control-plane or node choreography toward AWS, but they do not grant a free pass to ship unvetted images or over-privileged task roles that can read all municipal buckets. The claim that managed containers remove all customer image and IAM responsibilities is false. The claim that only AWS is responsible for securing container images and task or pod IAM roles is false. The claim that Physical Region guards scan and sign every city container image before deploy is false. Distractors fail by inventing facility-guard image signing, by declaring total removal of customer duties, or by assigning image and role hygiene solely to AWS. Exam caveat: "managed Kubernetes or containers" on an exam still usually leaves image provenance, task or pod IAM roles, and application secrets on the customer side of shared responsibility. Operational check: scan images in CI before promote-to-prod, use least-privilege task or pod roles, avoid baking long-lived keys into image layers, rotate any required secrets via managed secret stores, and periodically review running task roles for civic microservices against the data they actually need.