
The city wants staff to sign in to AWS with existing municipal SSO. Who is responsible for configuring identity federation into AWS?
Select an answer to reveal the explanation.
Short Explanation
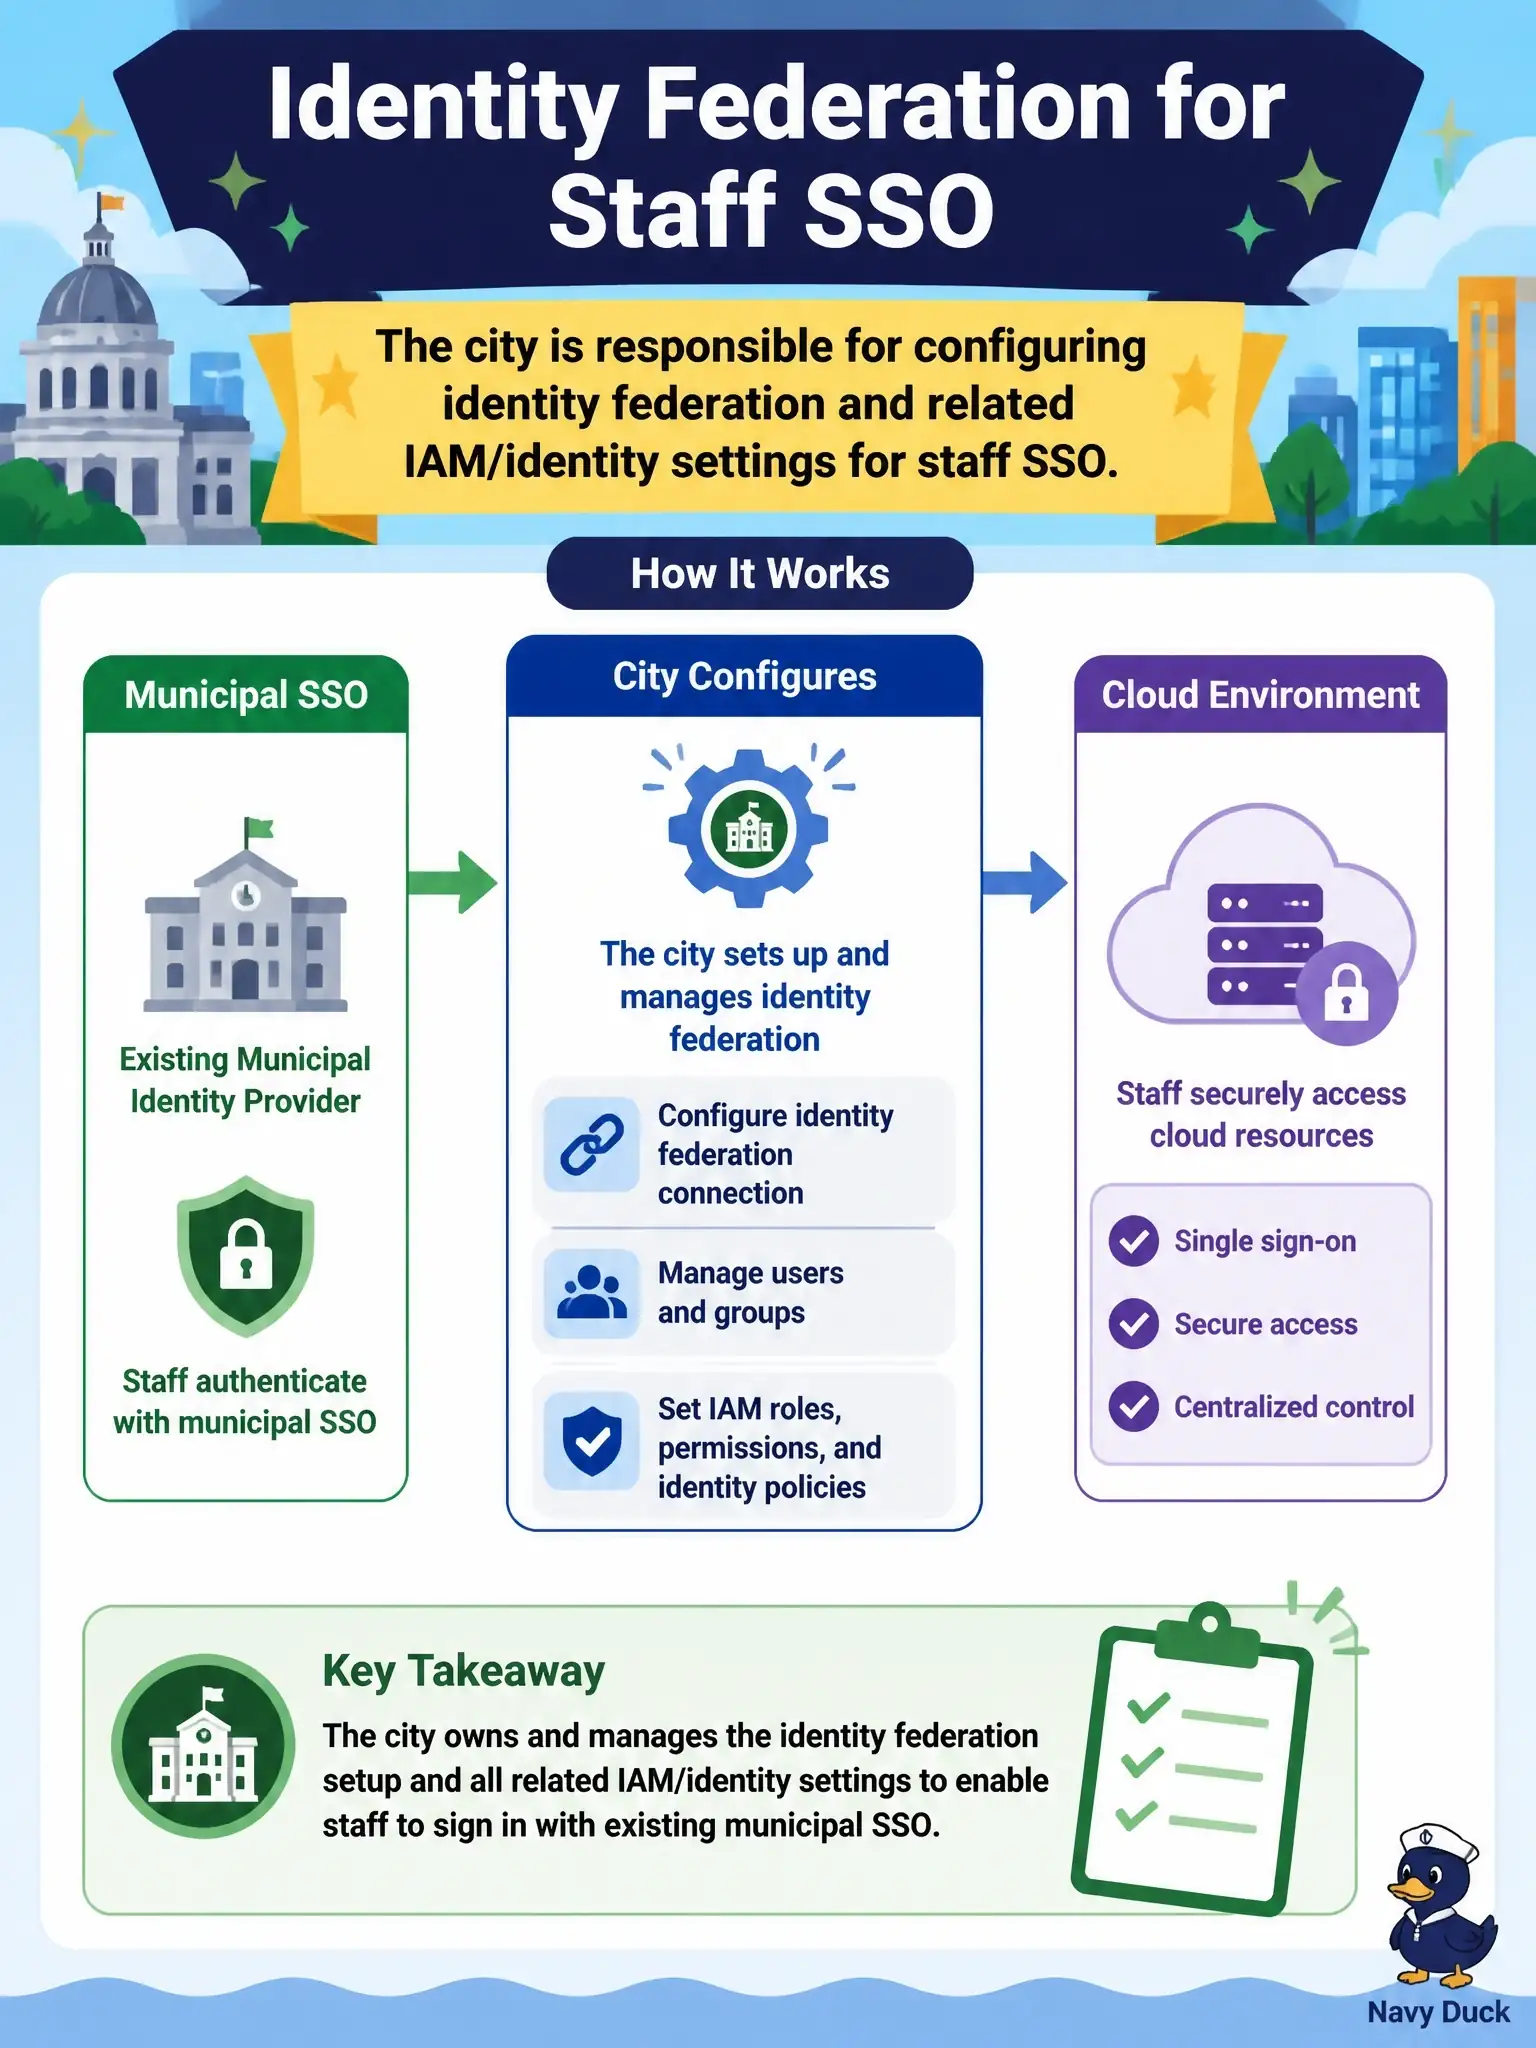
You're responsible for wiring the city's identity provider to AWS and setting up IAM or Identity Center access. AWS won't automatically federate your on-prem directory, and threat detection or facility guards don't handle SSO.
Full Explanation
The city is responsible for configuring identity federation and related IAM or IAM Identity Center settings so staff can use single sign-on into AWS. AWS does not automatically federate every customer's on-premises directory without setup on day one. Physical datacenter guards do not approve each federated login at the Region door — facility security and identity federation are different control planes. Amazon GuardDuty focuses on threat detection; it does not configure SSO federation as part of finding malicious activity. Correct reasoning: connecting Active Directory or another identity provider, defining permission sets or role mappings, and maintaining those integrations are customer duties that keep workforce access aligned to HR status. The automatic-federation claim fails because it assumes zero-setup onboarding of an on-premises directory. The guard-approval claim fails by inventing guard-based login approval at the Region door. The GuardDuty claim fails by assigning SSO configuration to a threat-detection service. Exam caveat: managed identity services still require customer design of who trusts whom and which roles federated users may assume. Operational check: document the IdP connection, test joiner-mover-leaver flows for city employees, enforce MFA where appropriate, review federated role mappings against least privilege, and confirm break-glass paths do not depend on unmanaged shared passwords.