
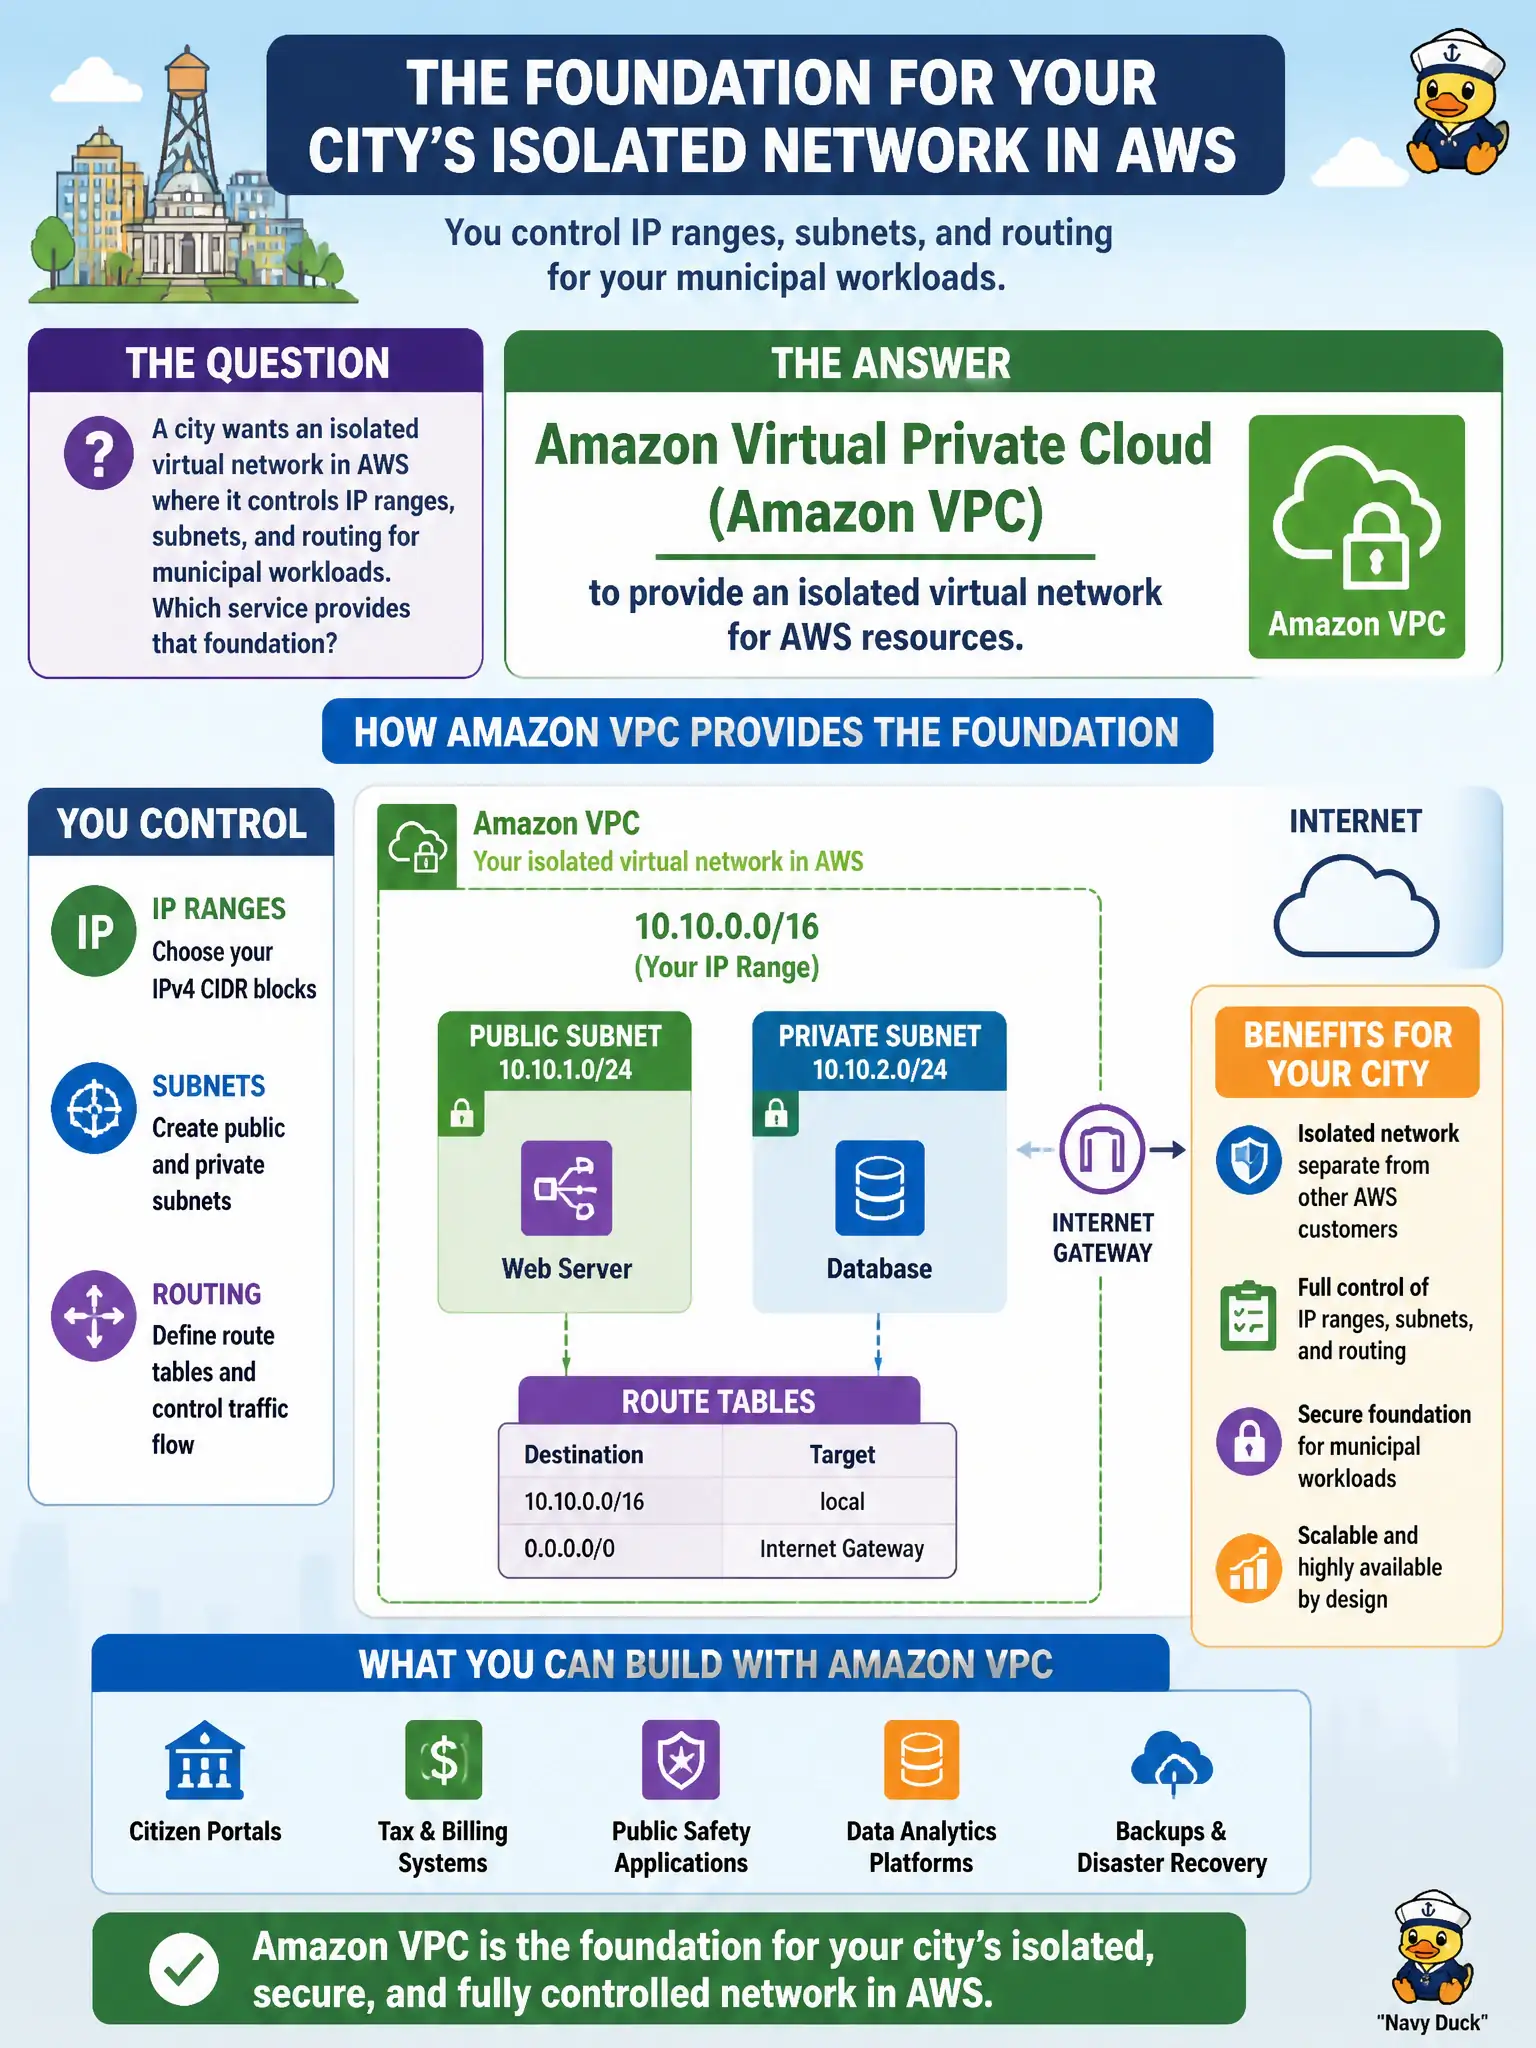
A city wants an isolated virtual network in AWS where it controls IP ranges, subnets, and routing for municipal workloads. Which service provides that foundation?
Select an answer to reveal the explanation.
Short Explanation
A VPC is your own fenced neighborhood in the AWS cloud—you pick the streets (IP ranges), blocks (subnets), and how traffic flows. CloudFront is edge delivery, SNS is messaging, and Organizations manages multi-account structure—not the virtual network itself.
Full Explanation
A city that wants an isolated virtual network in AWS where it controls IP ranges, subnets, and routing for municipal workloads should use Amazon Virtual Private Cloud (Amazon VPC). VPC is the foundational networking construct that provides an isolated virtual network for AWS resources, with customer-defined CIDR blocks, subnets, route tables, gateways, and security controls. Nearly every Regional compute and data pattern for city workloads sits inside a VPC design.
Amazon CloudFront is a CDN, not the primary isolated virtual network fabric for placing EC2 and RDS. Amazon SNS is pub/sub messaging, not a private IP networking boundary. AWS Organizations governs multi-account structure and policies; it is not a subnet routing service inside one account.
Exam caveat: Isolated virtual network with IP/subnet/routing control → VPC. Do not confuse Organizations (accounts) or CloudFront (content delivery) with VPC networking fundamentals.
Operational check: create production and non-production VPCs with non-overlapping CIDRs planned against on-premises ranges, allocate public and private subnets across AZs, tag resources for the responsible department, and peer or use Transit Gateway only through the network architecture review board.