
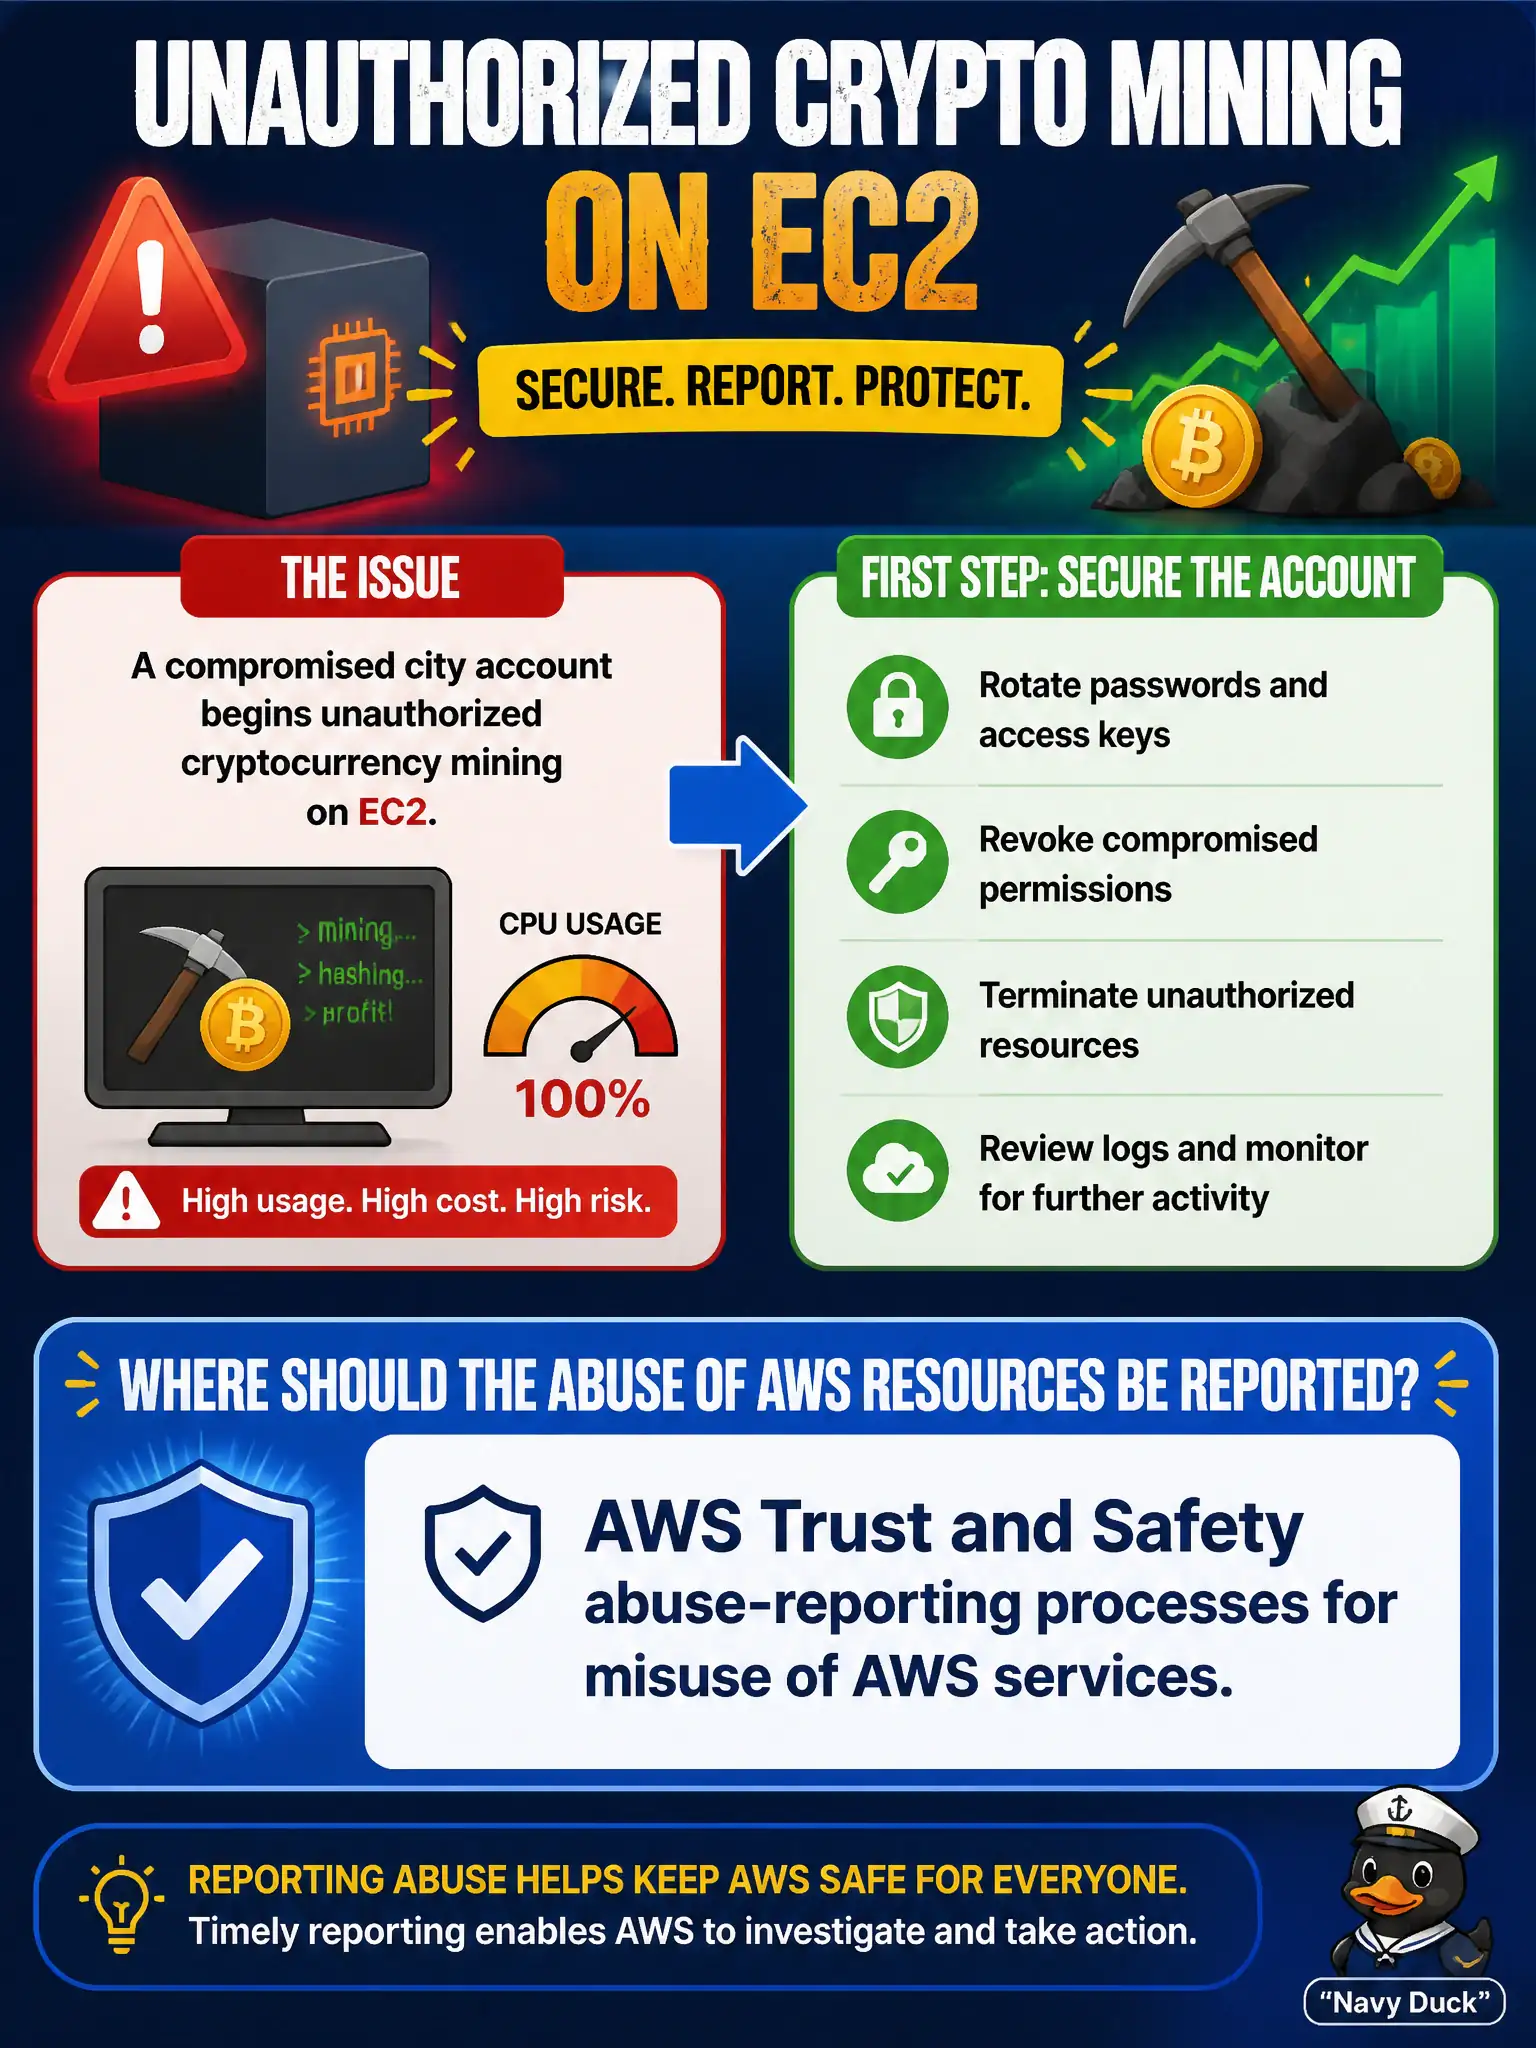
A compromised city account begins unauthorized cryptocurrency mining on EC2. Besides securing the account, where should the abuse of AWS resources be reported?
Select an answer to reveal the explanation.
Short Explanation
If someone is abusing AWS from a hijacked account—like crypto mining—report it through AWS Trust and Safety. Lock the account down at the same time.
Full Explanation
If a compromised city account begins unauthorized cryptocurrency mining on EC2, the city must secure the account and report the abuse of AWS resources through AWS Trust and Safety abuse-reporting processes. Trust and Safety handles misuse reports such as abusive mining, malware hosting, or other violations—complementing the customer's own incident response to rotate keys, isolate instances, and close security gaps.
Amazon Personalize builds recommendation models rather than handling abuse reports. AWS Artifact distributes compliance reports, not abuse intake. Amazon Forecast predicts time series and does not receive abuse reports. ML personalization, artifact portals, and forecasting services are unrelated to abuse reporting.
Exam caveat: Compromise response = contain + eradicate + recover + report abuse via Trust and Safety when AWS resources are misused. Support cases help with account recovery guidance; Artifact is not the abuse desk.
Operational check for incident response: immediately restrict IAM and root access, stop or isolate mining instances, rotate compromised keys, enable MFA everywhere, review CloudTrail for persistence, submit an abuse report through AWS Trust and Safety channels, preserve evidence for forensics, and run a post-incident review to harden CI/CD and secret storage against repeat civic account takeovers.