
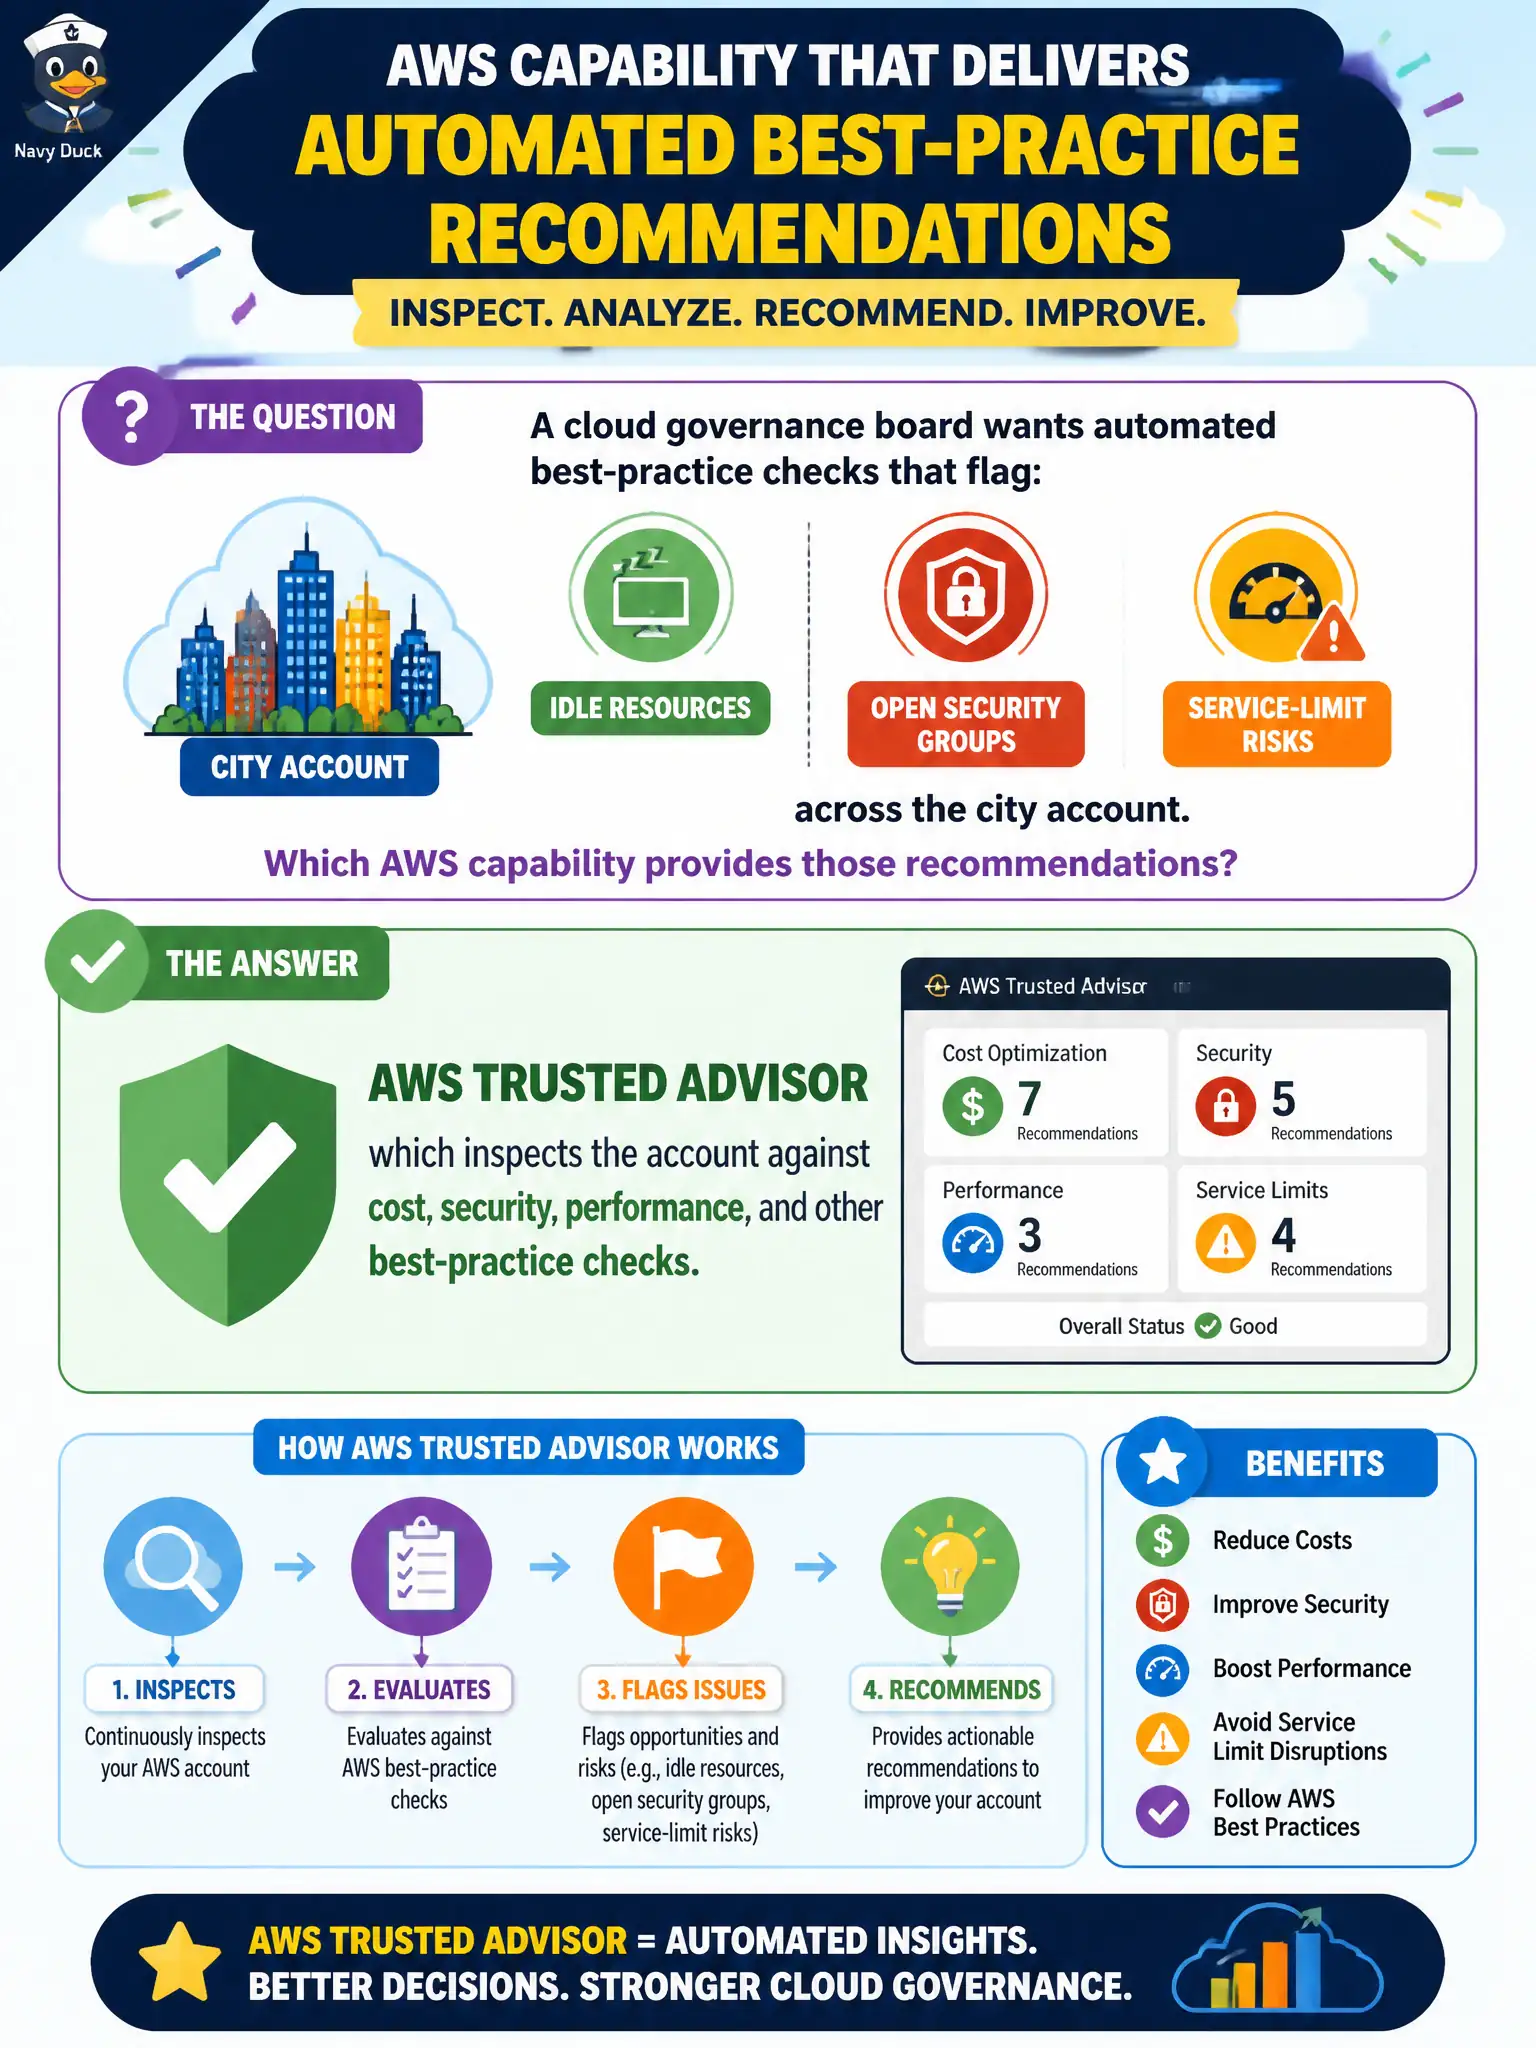
A cloud governance board wants automated best-practice checks that flag idle resources, open security groups, and service-limit risks across the city account. Which AWS capability provides those recommendations?
Select an answer to reveal the explanation.
Short Explanation
Want a checkup that catches wasteful resources and shaky security settings? That is Trusted Advisor. Think of it as a cloud wellness scan for the account.
Full Explanation
A cloud governance board that wants automated best-practice checks flagging idle resources, open security groups, and service-limit risks across the city account should use AWS Trusted Advisor. Trusted Advisor inspects the account against cost, security, performance, fault tolerance, and service-limit categories (with check availability depending on Support level) and recommends remediations—functioning as a cloud wellness scan for municipal accounts.
Amazon Kinesis Data Firehose delivers streaming data rather than account best-practice reviews. AWS Snowcone is an edge storage and compute device, not a recommendation engine. Amazon Pinpoint runs customer engagement campaigns rather than Trusted Advisor checks. Streaming, edge appliances, and campaigns do not replace Trusted Advisor.
Exam caveat: Trusted Advisor = best-practice recommendations; Security Hub = centralized security findings; GuardDuty = threat detection; Config = configuration compliance. Idle resources and open SG checks are classic Trusted Advisor examples on CLF.
Operational check for governance: review Trusted Advisor weekly in the management account and critical members, assign owners for high-risk security findings, track service-limit increases before tax season, refresh cost recommendations before budget hearings, and remember some checks require Business/Enterprise-level Support to fully unlock.