
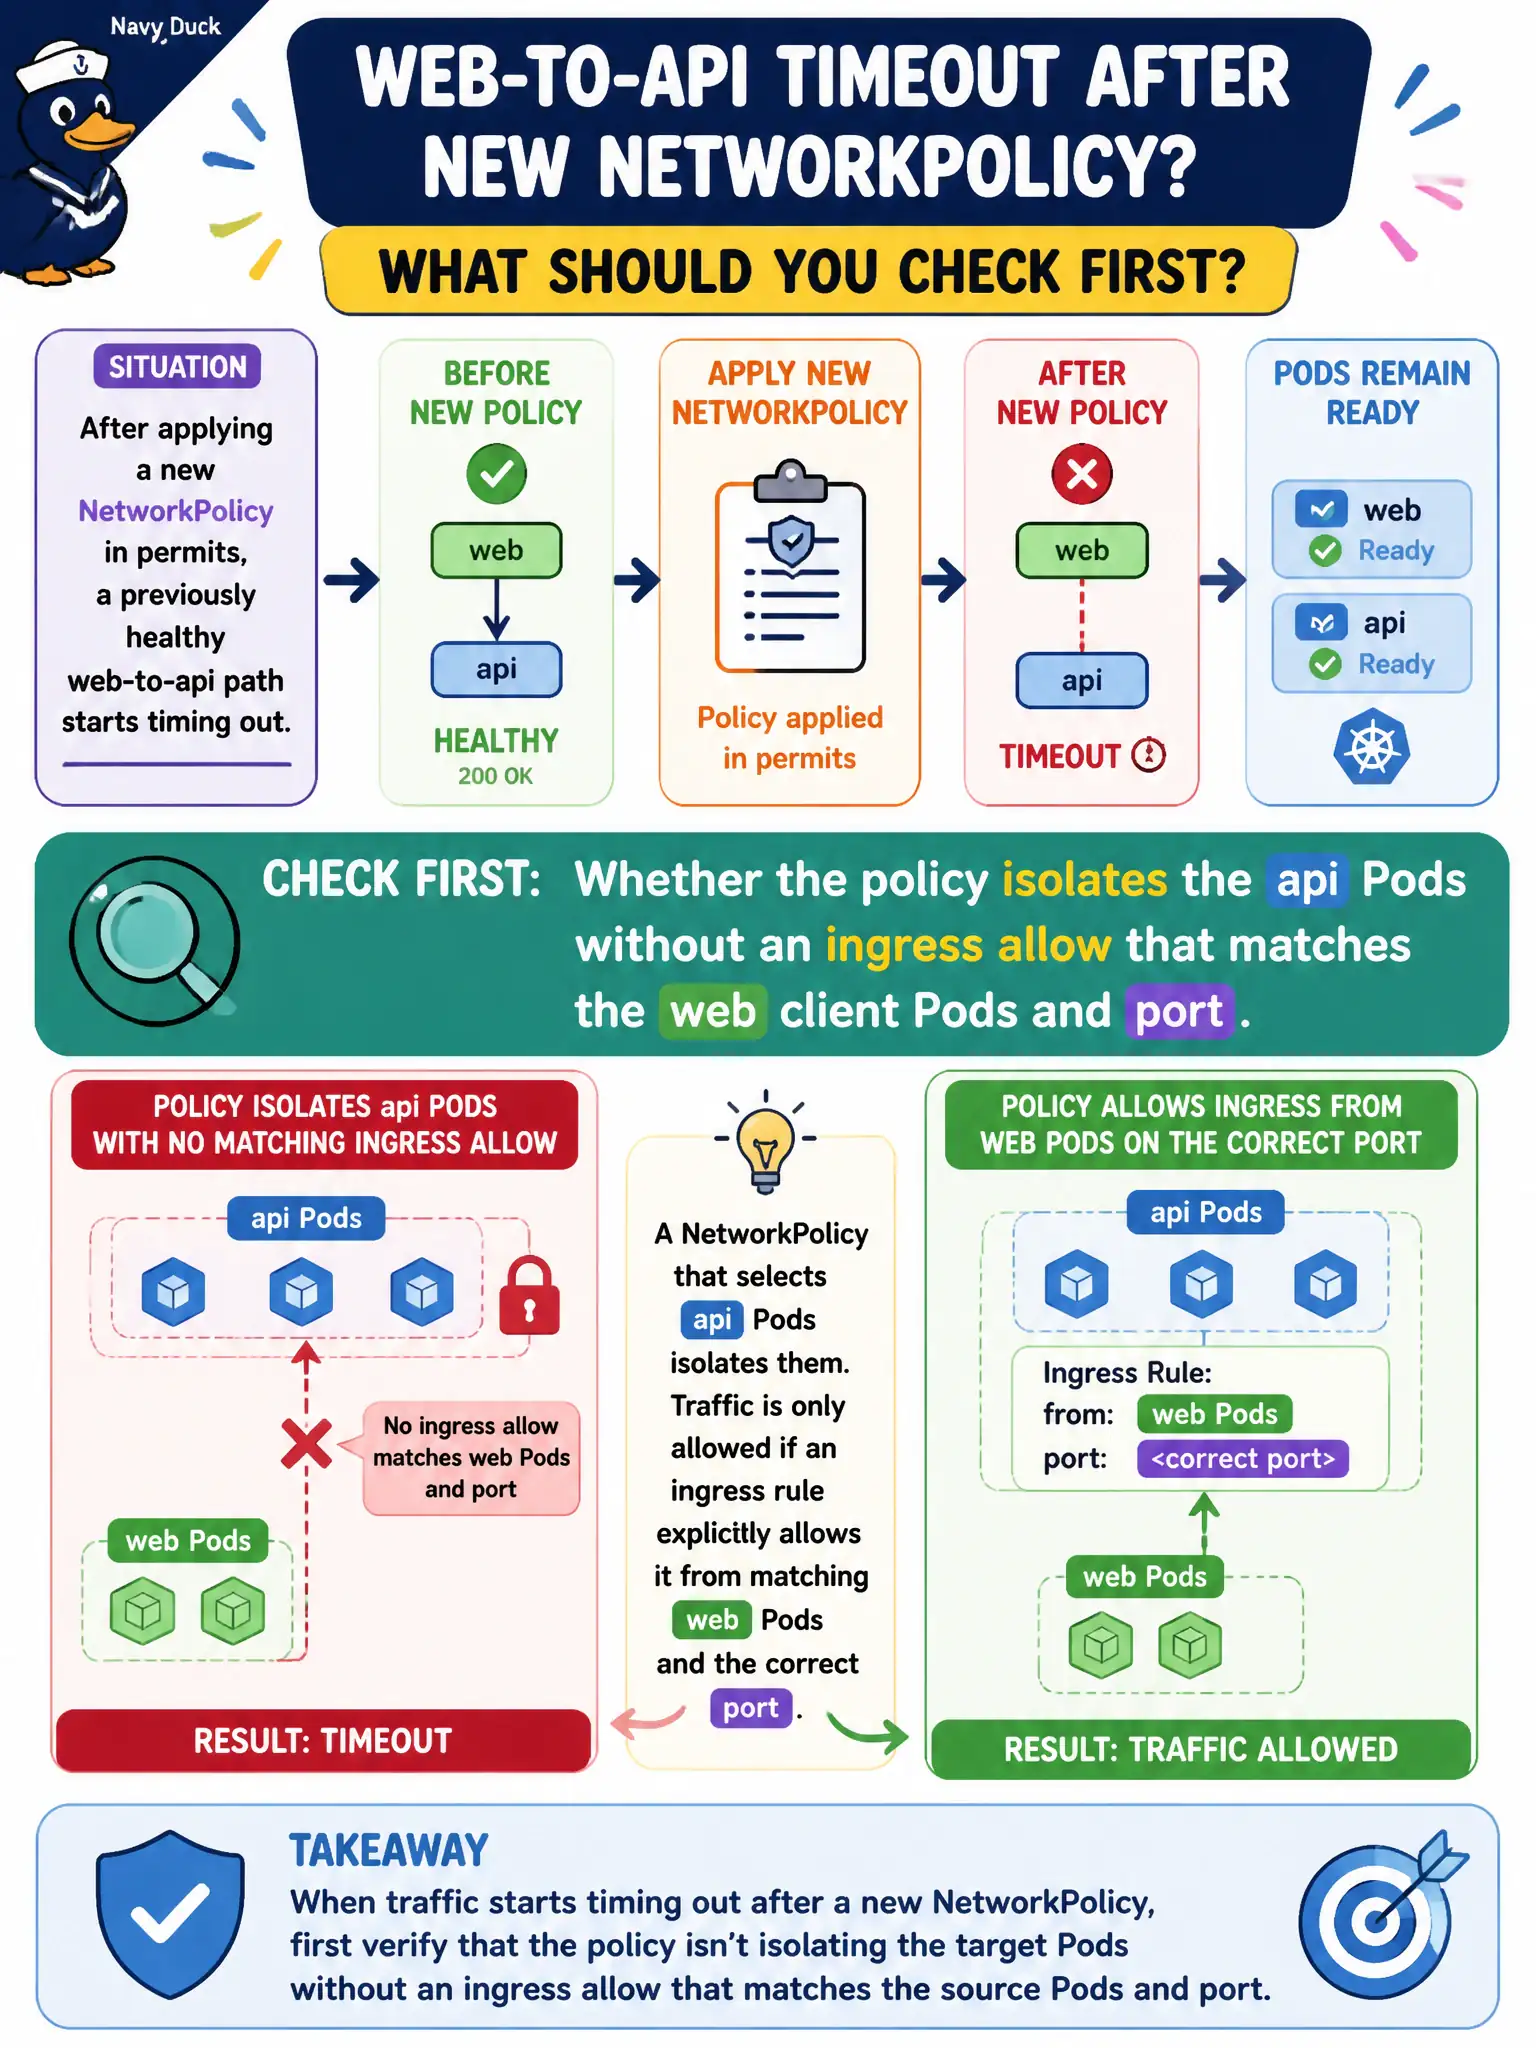
After applying a new NetworkPolicy in permits, a previously healthy web-to-api path starts timing out. Pods remain Ready. What should you check first?
Select an answer to reveal the explanation.
Short Explanation
New policy, sudden timeouts, Pods still green—classic “door locked, nobody on the allow list.” Start by reading who the policy selects and whether web clients and the right port are actually allowed. Don’t chase DNS restarts until the allow rules look right.
Full Explanation
After applying a new NetworkPolicy in permits, a previously healthy web-to-api path that starts timing out while Pods remain Ready should first be checked for isolation without a matching ingress allow. Ask whether the policy selects the api Pods and whether there is an ingress allow that matches the web client Pods and the correct port/protocol. Ready status only means probes succeed; it does not prove NetworkPolicy permits the client path. This is the classic locked door with nobody on the allow list—new policy, sudden timeouts, Pods still green.
You should not first assume kube-dns must be restarted whenever any NetworkPolicy is created; DNS restarts are unrelated to a missing ingress allow on api Pods. Deployment replica counts do not automatically drop to zero under NetworkPolicy. Ready Pods also do not lose their Service ClusterIP merely because NetworkPolicy objects exist—ClusterIP and Endpoints readiness are separate from packet policy allows.
Exam caveat: distinguish probe success from policy-allowed east-west traffic. Also verify peer labels and protocol, not only numeric ports, because a TCP/UDP mismatch produces the same symptom class. Operational check: kubectl describe networkpolicy in permits; kubectl get pods --show-labels; curl from a web Pod to the api Service; temporarily add a correct allow from the web podSelector on the api port and confirm restoration. File the root cause as a policy allow gap in the municipal incident record rather than as an application crash or DNS outage, and keep the before/after policy YAML for auditors.