
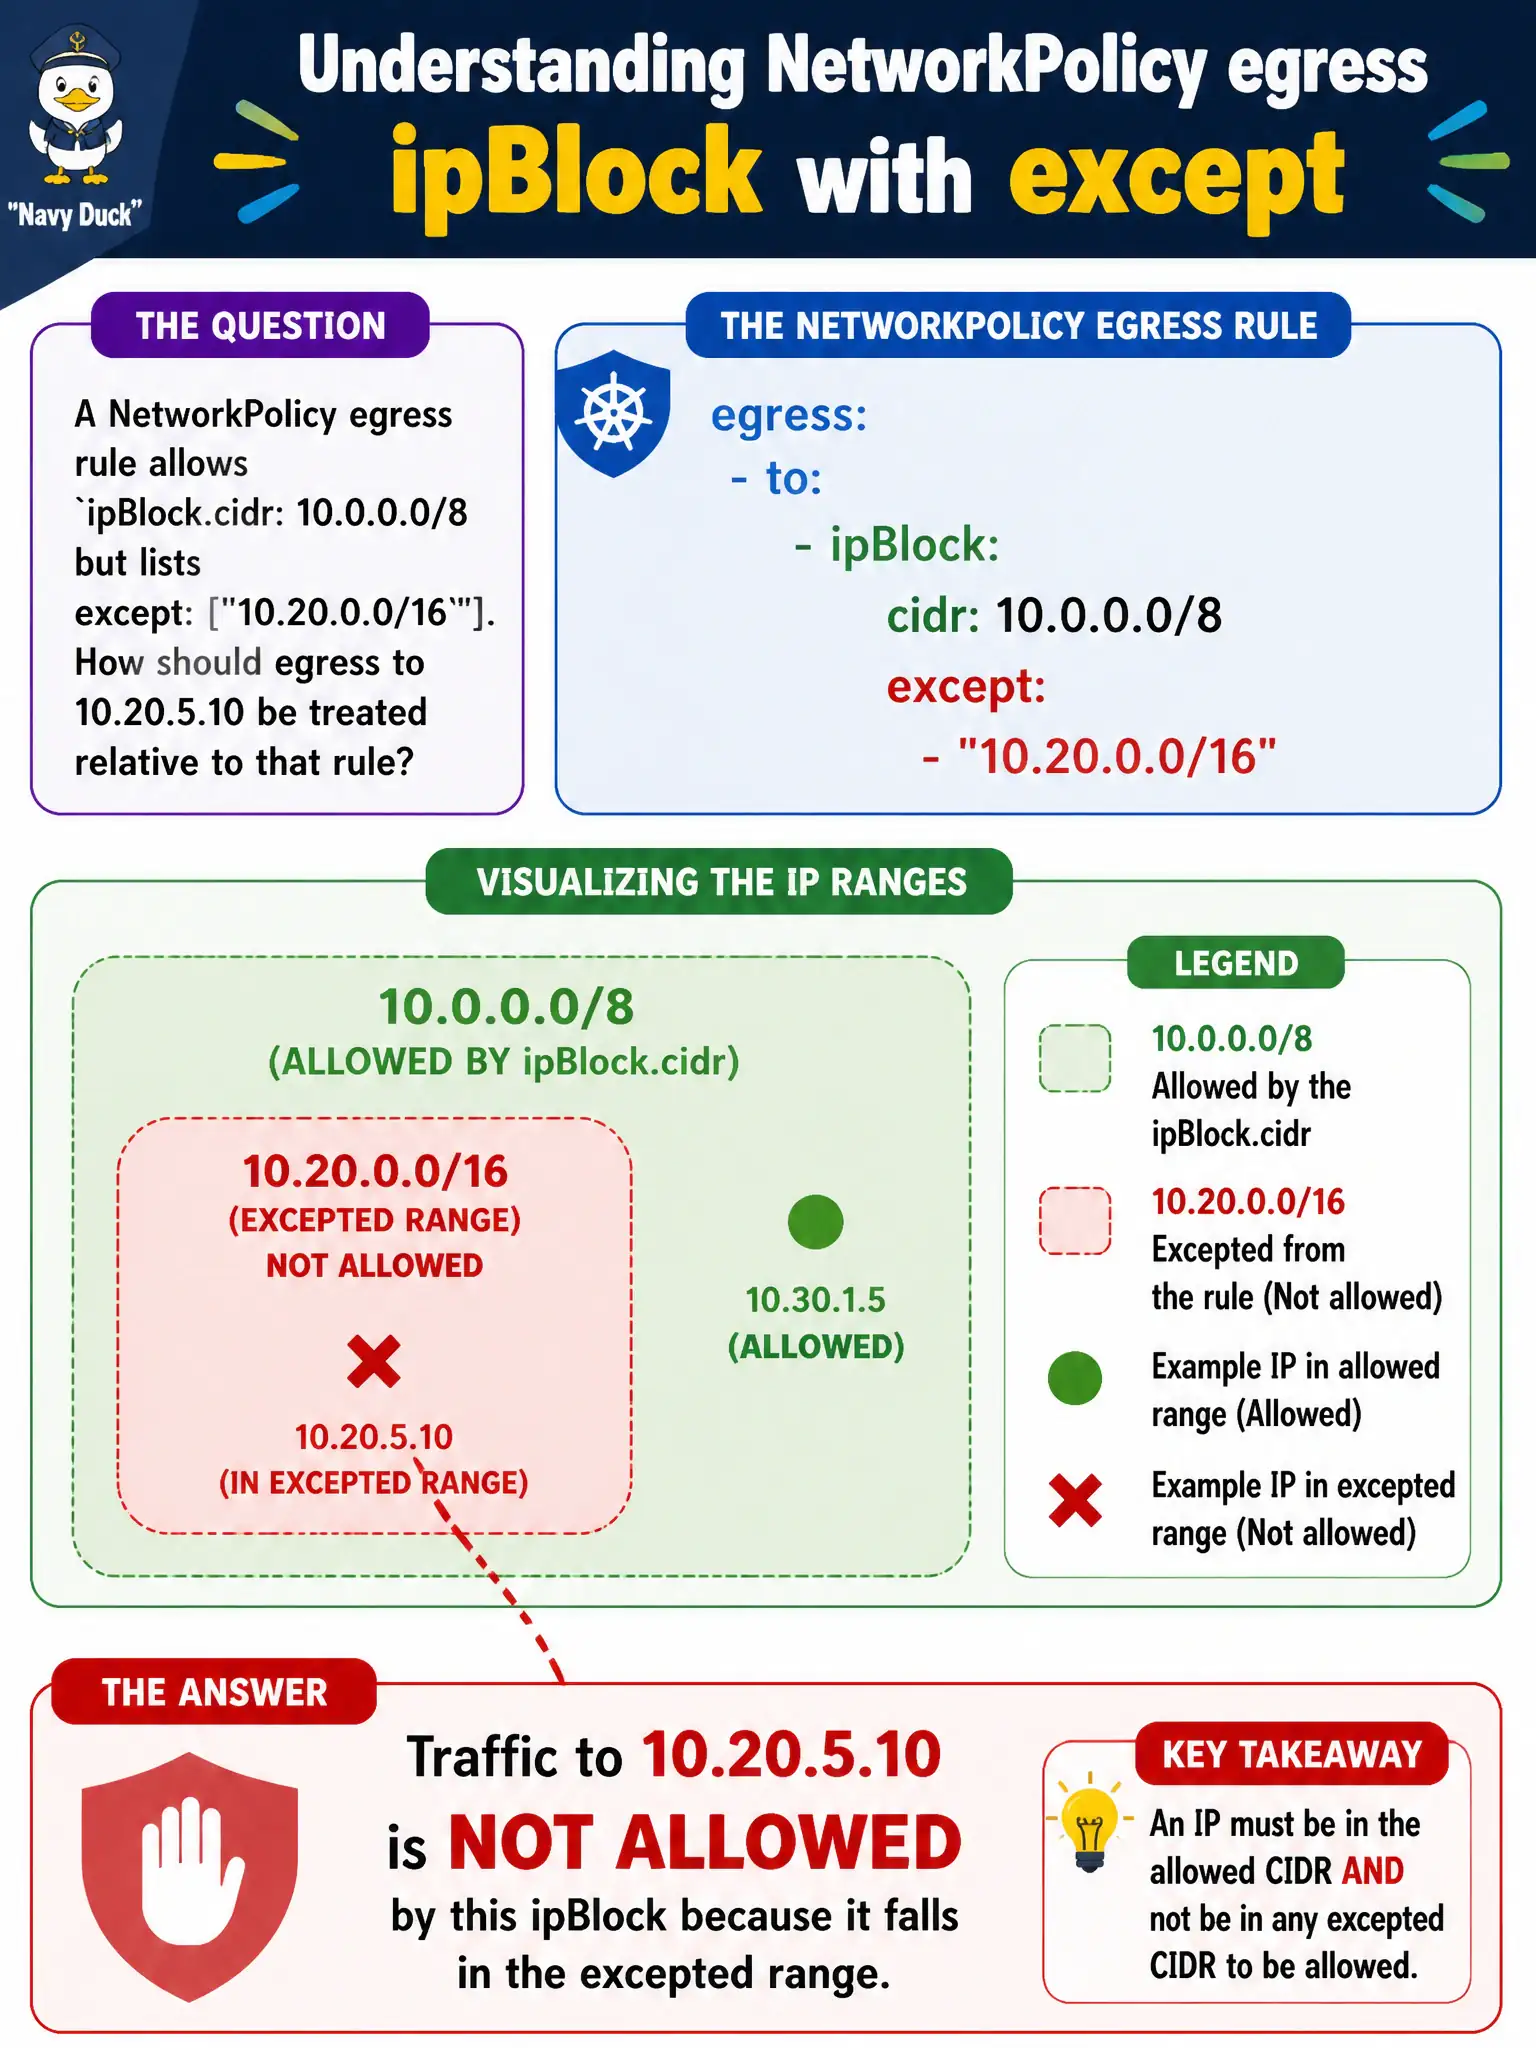
A NetworkPolicy egress rule allows ipBlock.cidr: 10.0.0.0/8 but lists except: ["10.20.0.0/16"]. How should egress to 10.20.5.10 be treated relative to that rule?
Select an answer to reveal the explanation.
Short Explanation
An except clause is like saying “the whole neighborhood is OK except that one cul-de-sac.” The /8 opens a big range, then except pulls 10.20.0.0/16 back out. 10.20.5.10 sits in that cul-de-sac, so this allow rule does not cover it.
Full Explanation
An NetworkPolicy egress rule that allows ipBlock.cidr 10.0.0.0/8 but lists except ["10.20.0.0/16"] permits the broad range minus the carved-out subnet. Egress to 10.20.5.10 falls inside 10.20.0.0/16, so it is not allowed by this ipBlock rule. An except clause is like saying the whole neighborhood is OK except that one cul-de-sac—the /8 opens a big range, then except pulls 10.20.0.0/16 back out.
except is not limited to ingress rules; when present on an egress ipBlock, it subtracts from that egress allow. except does not merely carve hosts out of DNS while leaving IP egress to 10.20.5.10 allowed. The except list is not ignored until a second NetworkPolicy repeats the CIDR—it applies to the ipBlock where it is defined.
Exam caveat: read except as subtraction from the parent CIDR allow, not as a standalone global deny mechanism for unrelated destinations. Operational check: from the selected Pod, probe an address inside 10.0.0.0/8 but outside 10.20.0.0/16 (should be allowed by this rule) and probe 10.20.5.10 (should not be allowed by this rule). Document parent CIDRs and excepted ranges in the municipal destination inventory so network reviewers can validate payment or partner exclusions.