
A shared monitoring namespace must scrape app Pods in another namespace. Which NetworkPolicy source matches that whole monitoring namespace?
Select an answer to reveal the explanation.
Short Explanation
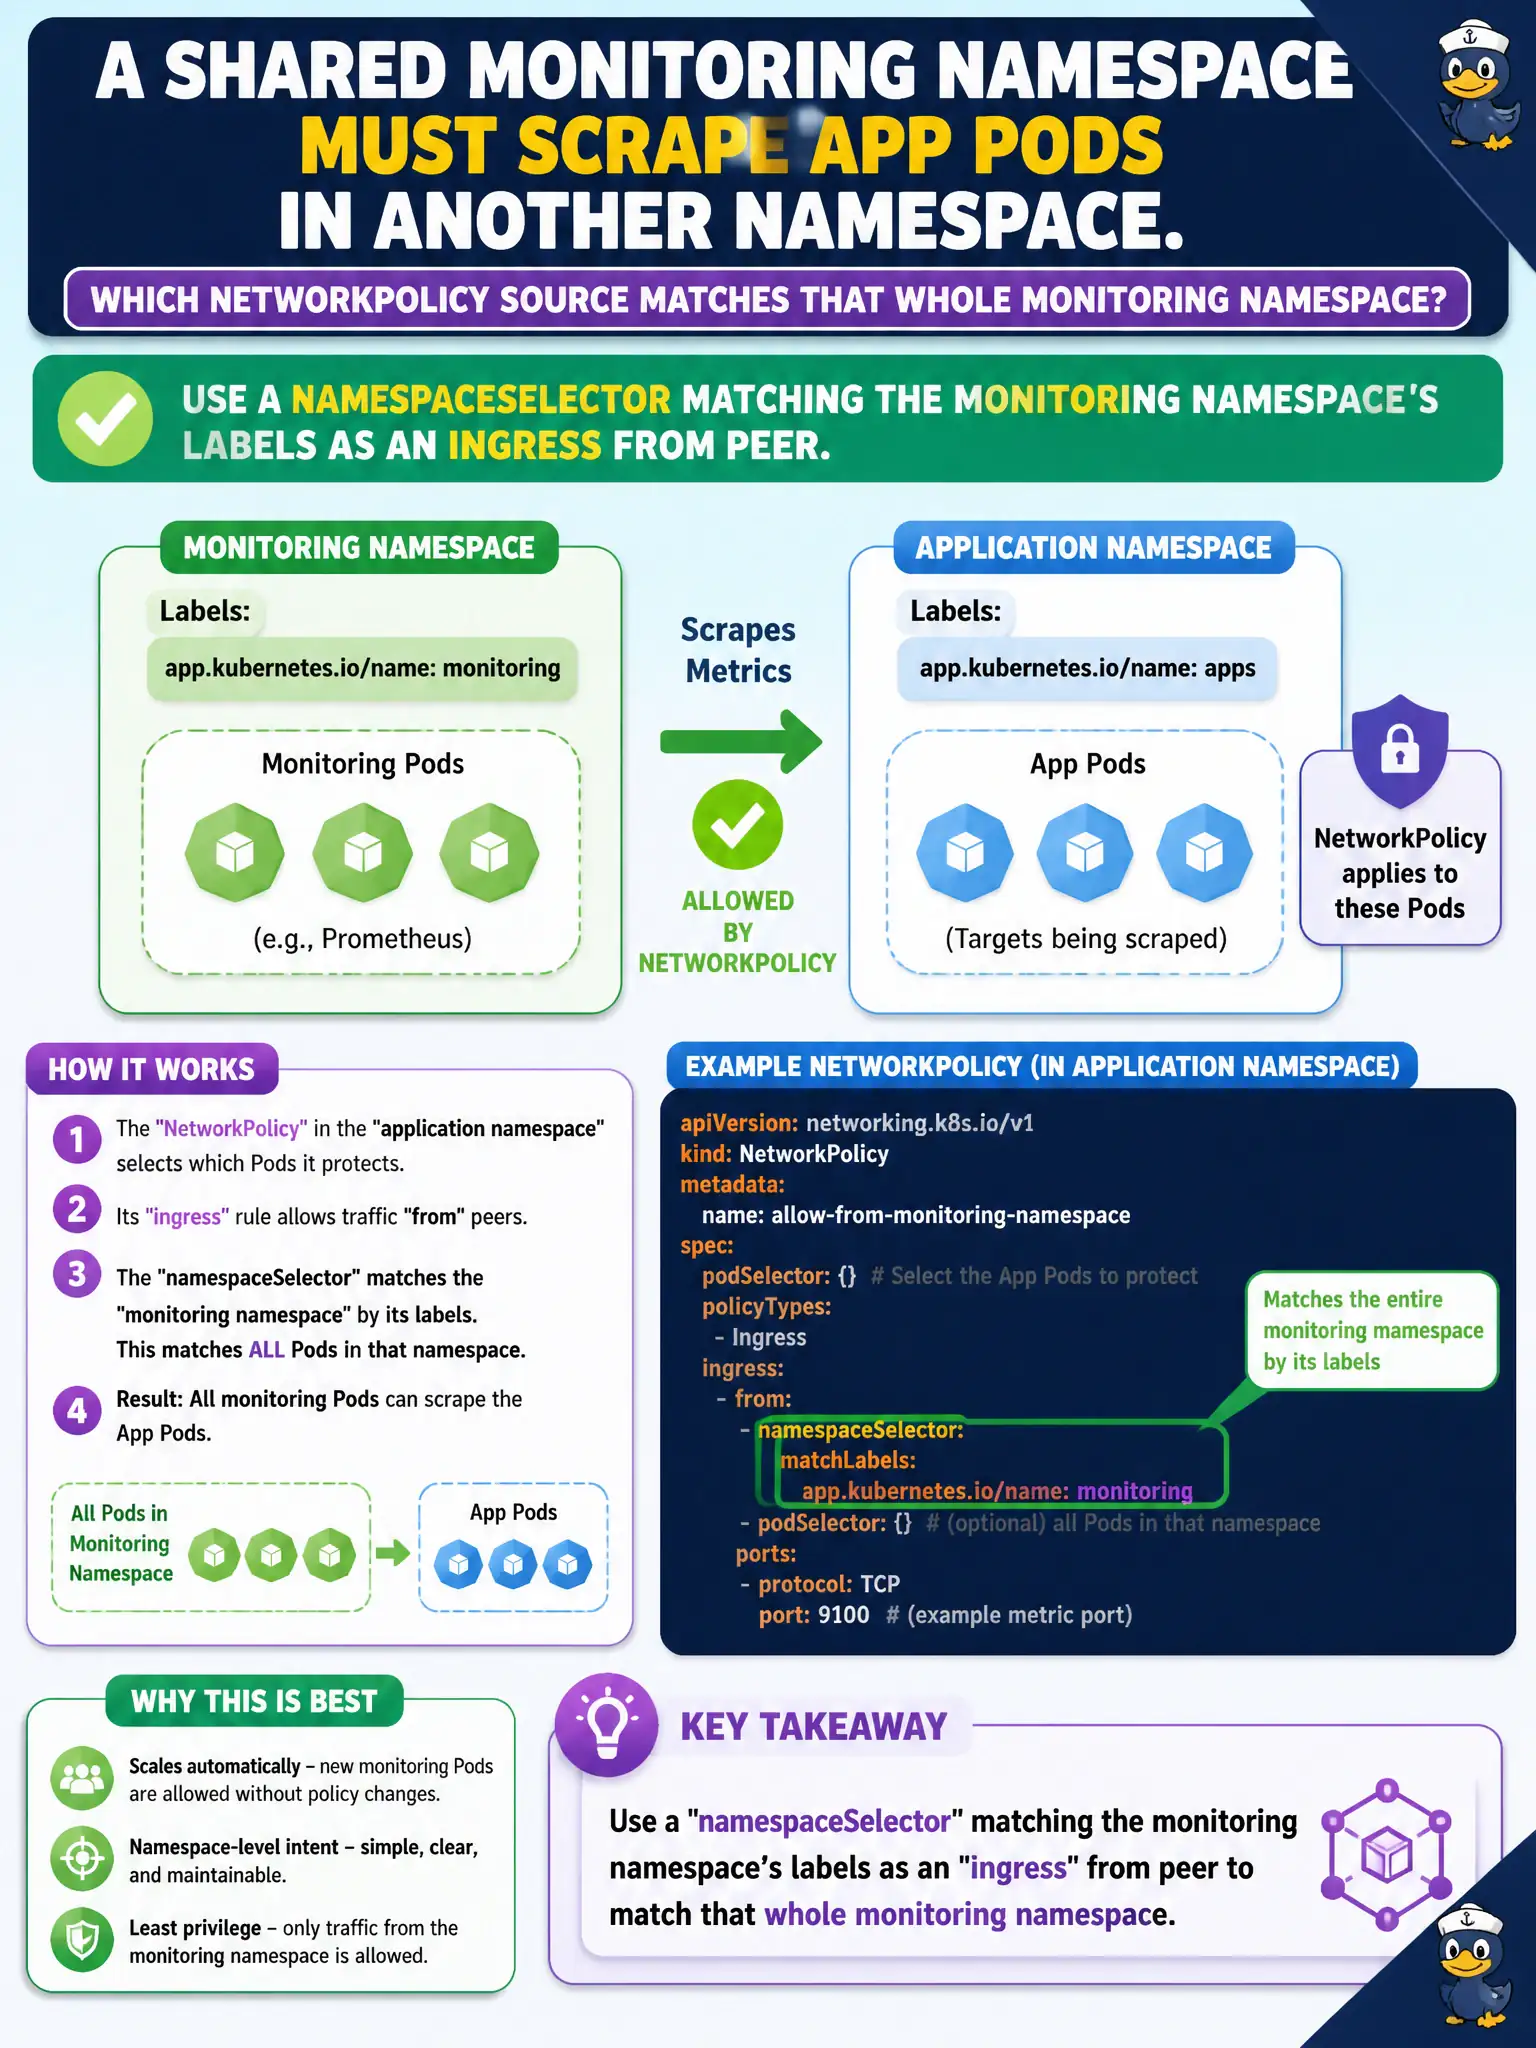
namespaceSelector is the "anyone wearing this building's badge" match. Label the monitoring namespace and allow it as an ingress source. RBAC admin rights or hostNetwork aren't NetworkPolicy peers.
Full Explanation
Cross-namespace monitoring scrapes need NetworkPolicy peers that can match an entire monitoring namespace. Use namespaceSelector against labels on the monitoring Namespace object as an ingress from peer (optionally combined with a podSelector). Label the monitoring namespace and allow that selector toward the app Pods’ scrape port. That “building badge” match is how municipal platform teams authorize a shared monitoring neighborhood without listing every scraper Pod name.
A podSelector for app=monitoring only inside the app namespace will not select Pods that actually live in the monitoring namespace; namespaceSelector is required for whole-namespace peers. Granting cluster-admin to the monitoring ServiceAccount affects API authorization, not NetworkPolicy packet allows. hostNetwork on app Pods is an isolation-weakening bypass, not a proper scrape allow.
Exam caveat: namespaceSelector matches Namespace labels, not a free-form namespace name field—label the Namespace first. Operational check: kubectl label namespace monitoring purpose=monitoring; apply the allow; verify scrapes from monitoring succeed and scrapes from other namespaces fail. Describe the NetworkPolicy peers for city auditors.