
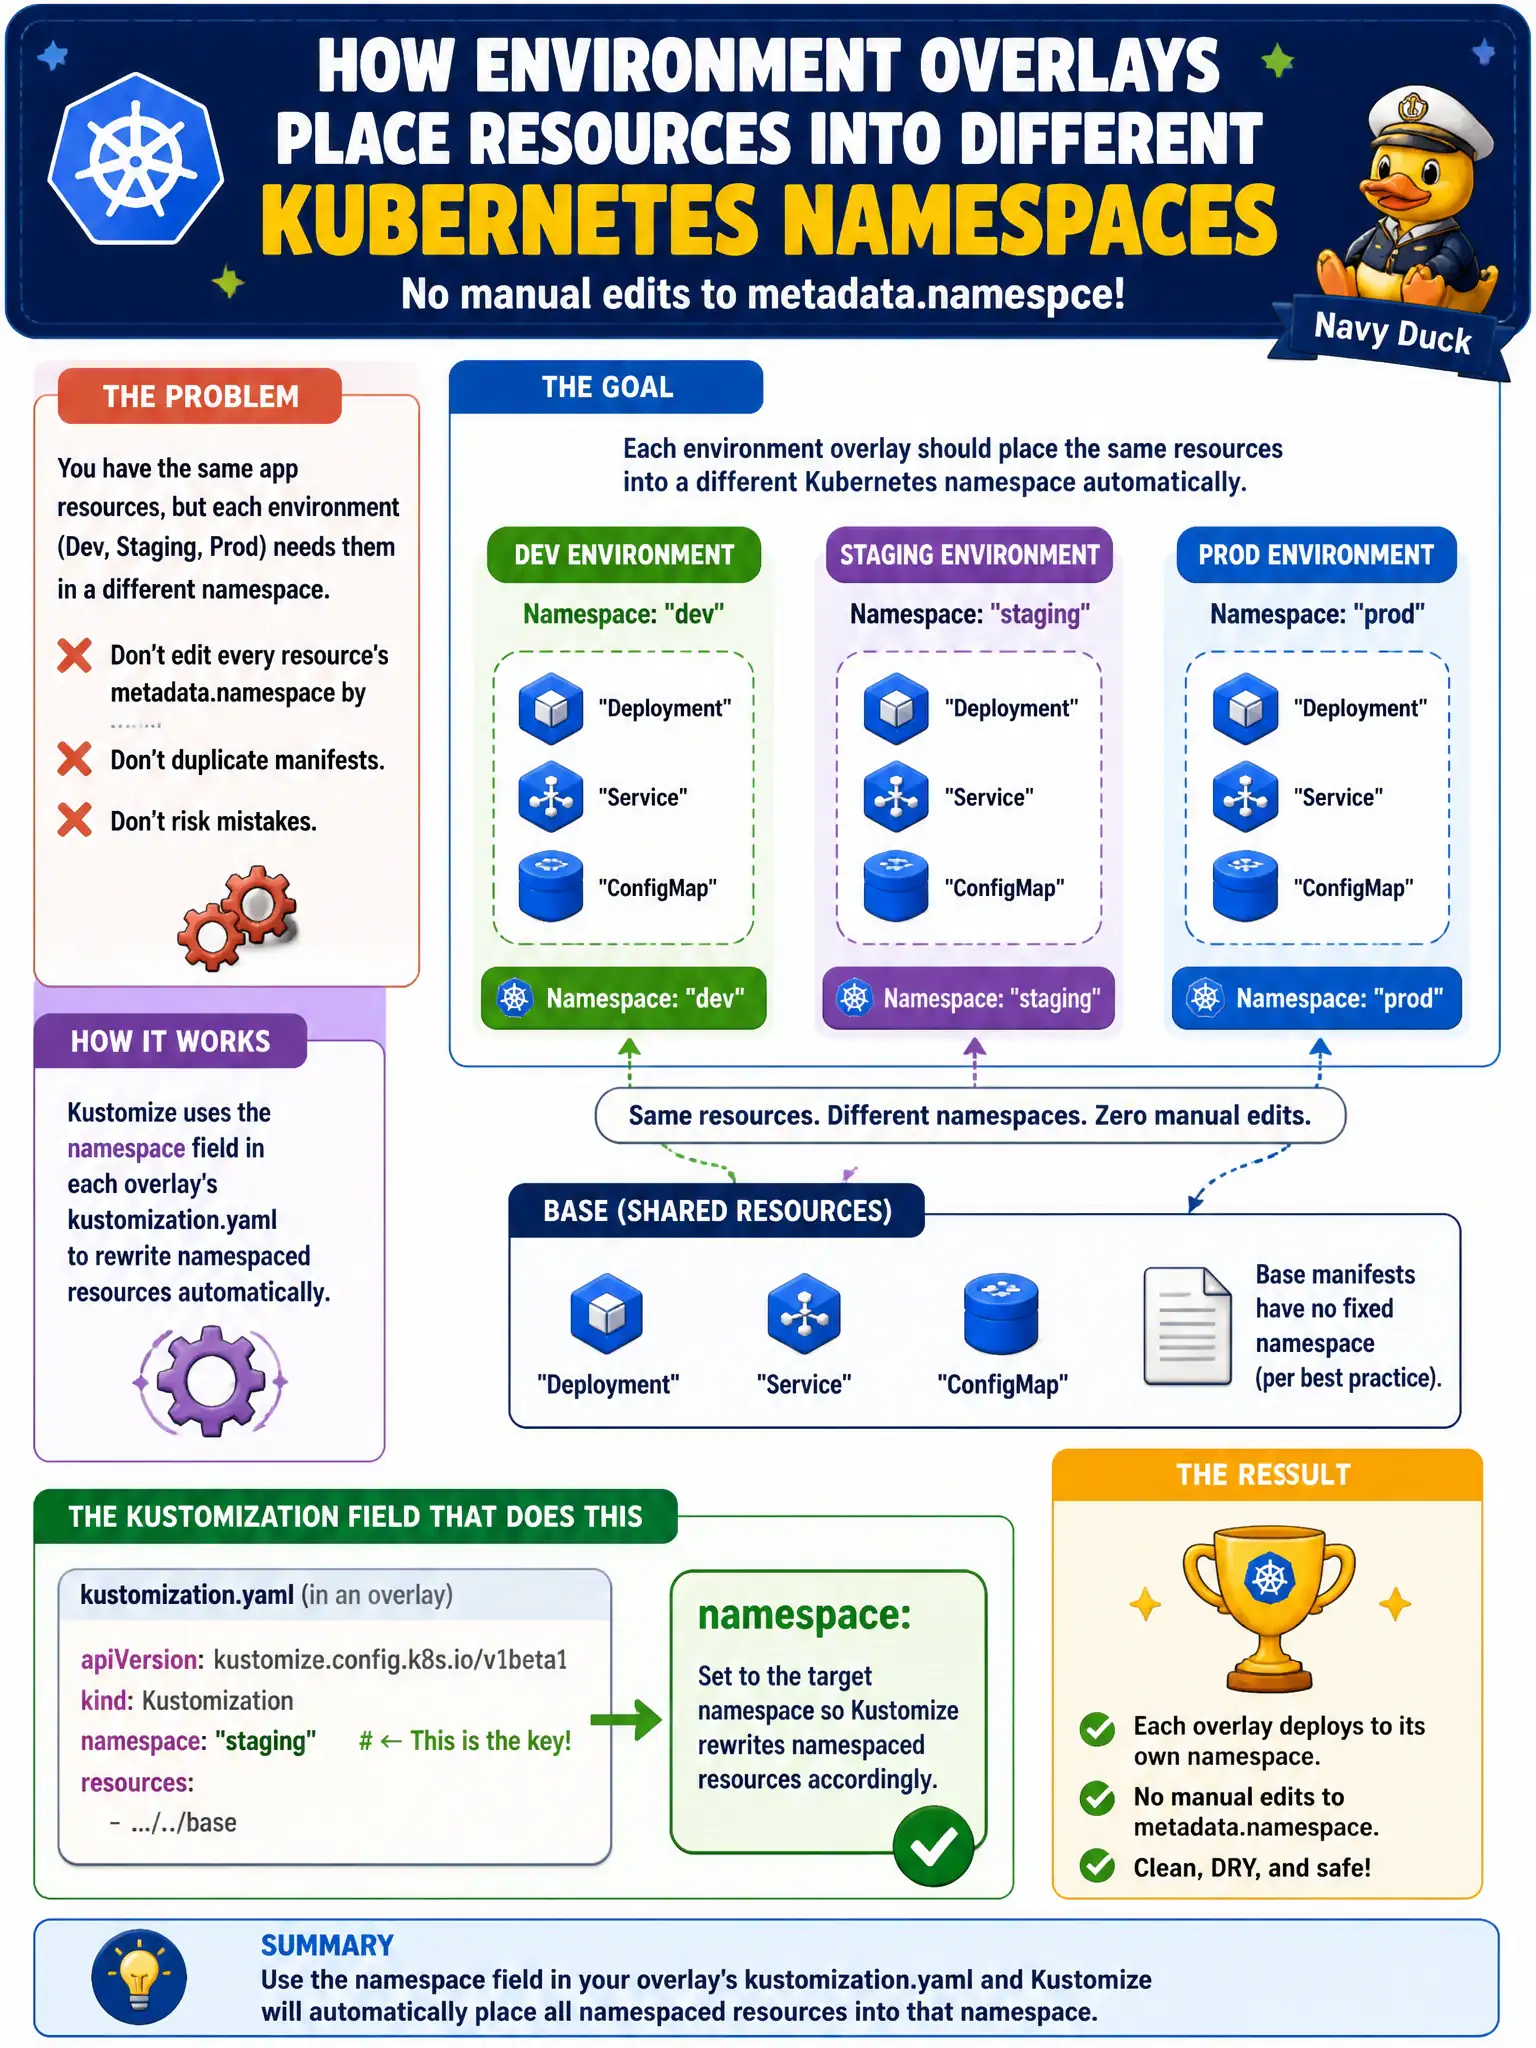
Each environment overlay should place rendered objects into a different Kubernetes namespace without editing every resource’s metadata.namespace by hand. Which kustomization field does that?
Select an answer to reveal the explanation.
Short Explanation
The namespace field is the destination stamp on every envelope leaving the overlay printer. One line, and namespaced resources head for staging or prod without rewriting each file.
Full Explanation
Each environment overlay should place rendered objects into a different Kubernetes namespace without editing every resource’s metadata.namespace by hand by setting the namespace: field in kustomization.yaml. Kustomize rewrites namespaced resources to that target namespace, letting municipal staging and production overlays share base YAML while landing in ns-staging versus ns-prod cleanly.
Why the other options fail by concept: images newTag set to a namespace string does not relocate objects. commonLabels with a key named namespace does not always relocate objects to a Kubernetes namespace. secretGenerator with a namespace literal does not move Deployments into that namespace by itself the way the namespace: field does.
Exam caveat: Cluster-scoped resources (ClusterRole, PV, etc.) are not namespaced by this field—review renders. Namespace objects themselves may need to be created separately (--create-namespace or a Namespace manifest). Combined with namePrefix, avoid overly long resulting names.
Operational check: Set namespace: permits-staging in the staging overlay, kubectl kustomize and grep metadata.namespace, apply -k, and kubectl get deploy -n permits-staging to confirm placement. Repeat for production with a different namespace value.