
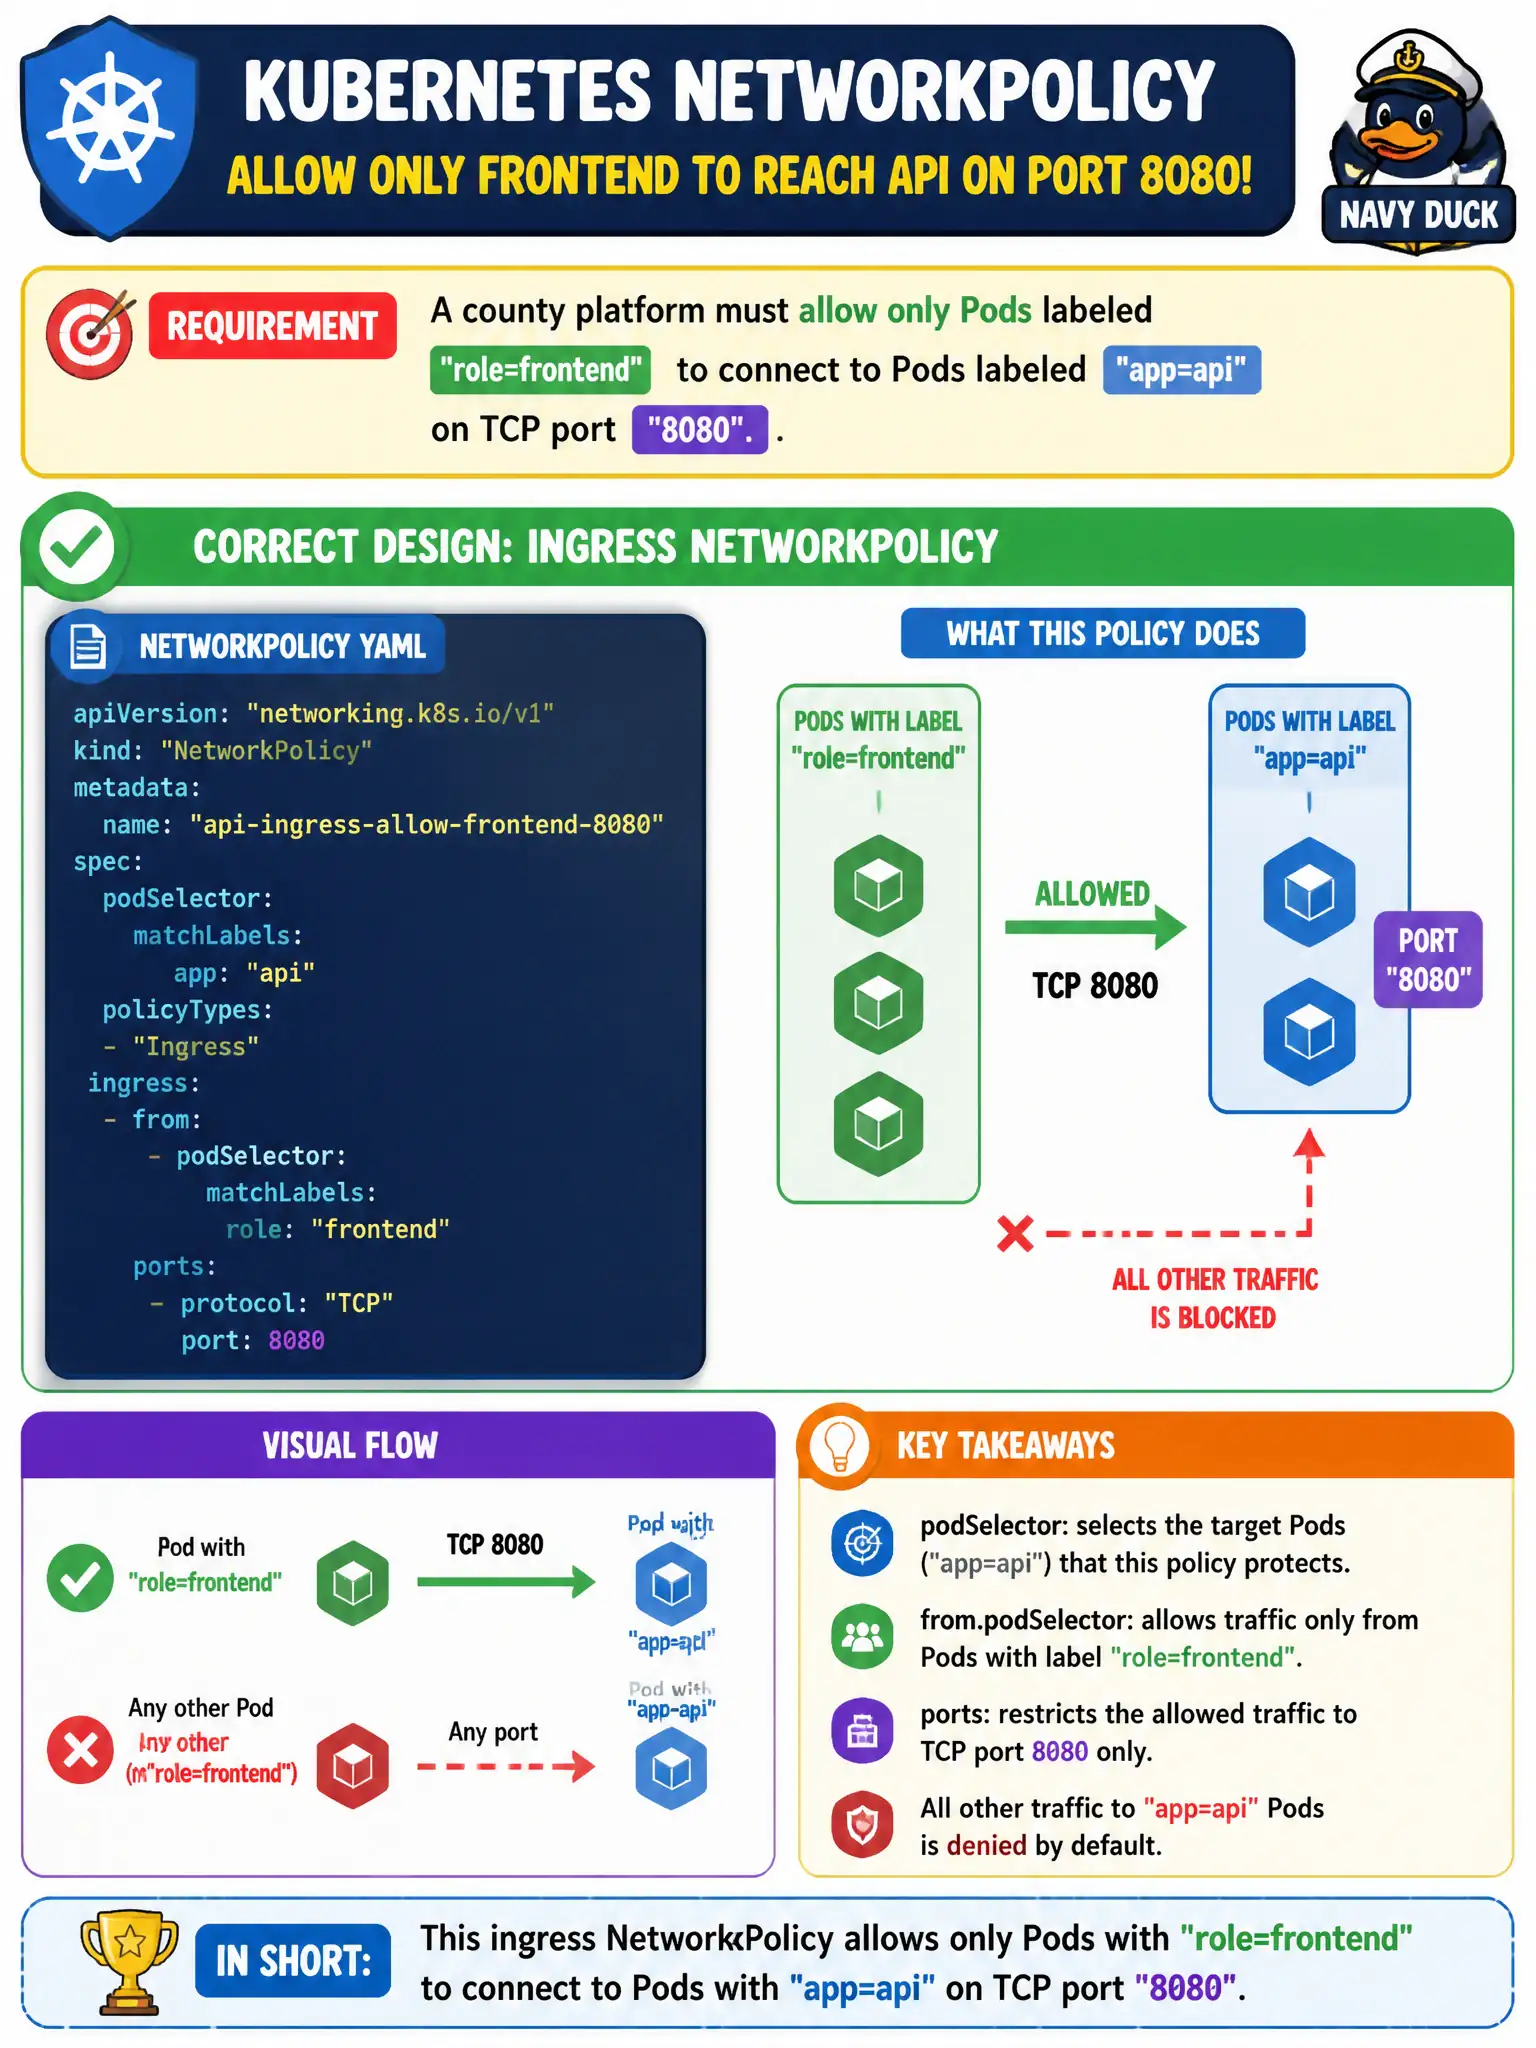
A county platform must allow only Pods labeled role=frontend to connect to Pods labeled app=api on TCP port 8080. Which NetworkPolicy design matches that requirement?
Select an answer to reveal the explanation.
Short Explanation
Want only the front desk to knock on the API door at port 8080? Write an ingress rule with the frontend podSelector and that exact port.
Full Explanation
A county platform that must allow only Pods labeled role=frontend to connect to Pods labeled app=api on TCP port 8080 should use an ingress NetworkPolicy selecting app=api Pods with a from podSelector for role=frontend and a ports entry for TCP 8080. That policy expresses the peer, direction, and port precisely—the CKA-depth pattern for least-privilege east-west access to a municipal API tier.
An egress-only policy on frontend Pods that lists every node CIDR and omits port numbers does not correctly encode the stated ingress allow to api:8080. A LimitRange that caps CPU does not authorize sockets to port 8080. A PodDisruptionBudget with minAvailable equal to 8080 does not authorize ingress traffic.
Exam caveat: unless a default-deny exists, unmatched traffic may still flow; combine with namespace default-deny for real isolation. Operational check: apply the policy, test connect from frontend versus other labels to api:8080, and confirm only frontend succeeds. This distinction matters on the CKA because distractors often mix adjacent objects that sound related but solve a different control-plane problem. This distinction matters on the CKA because distractors often mix adjacent objects that sound related but solve a different control-plane problem.