
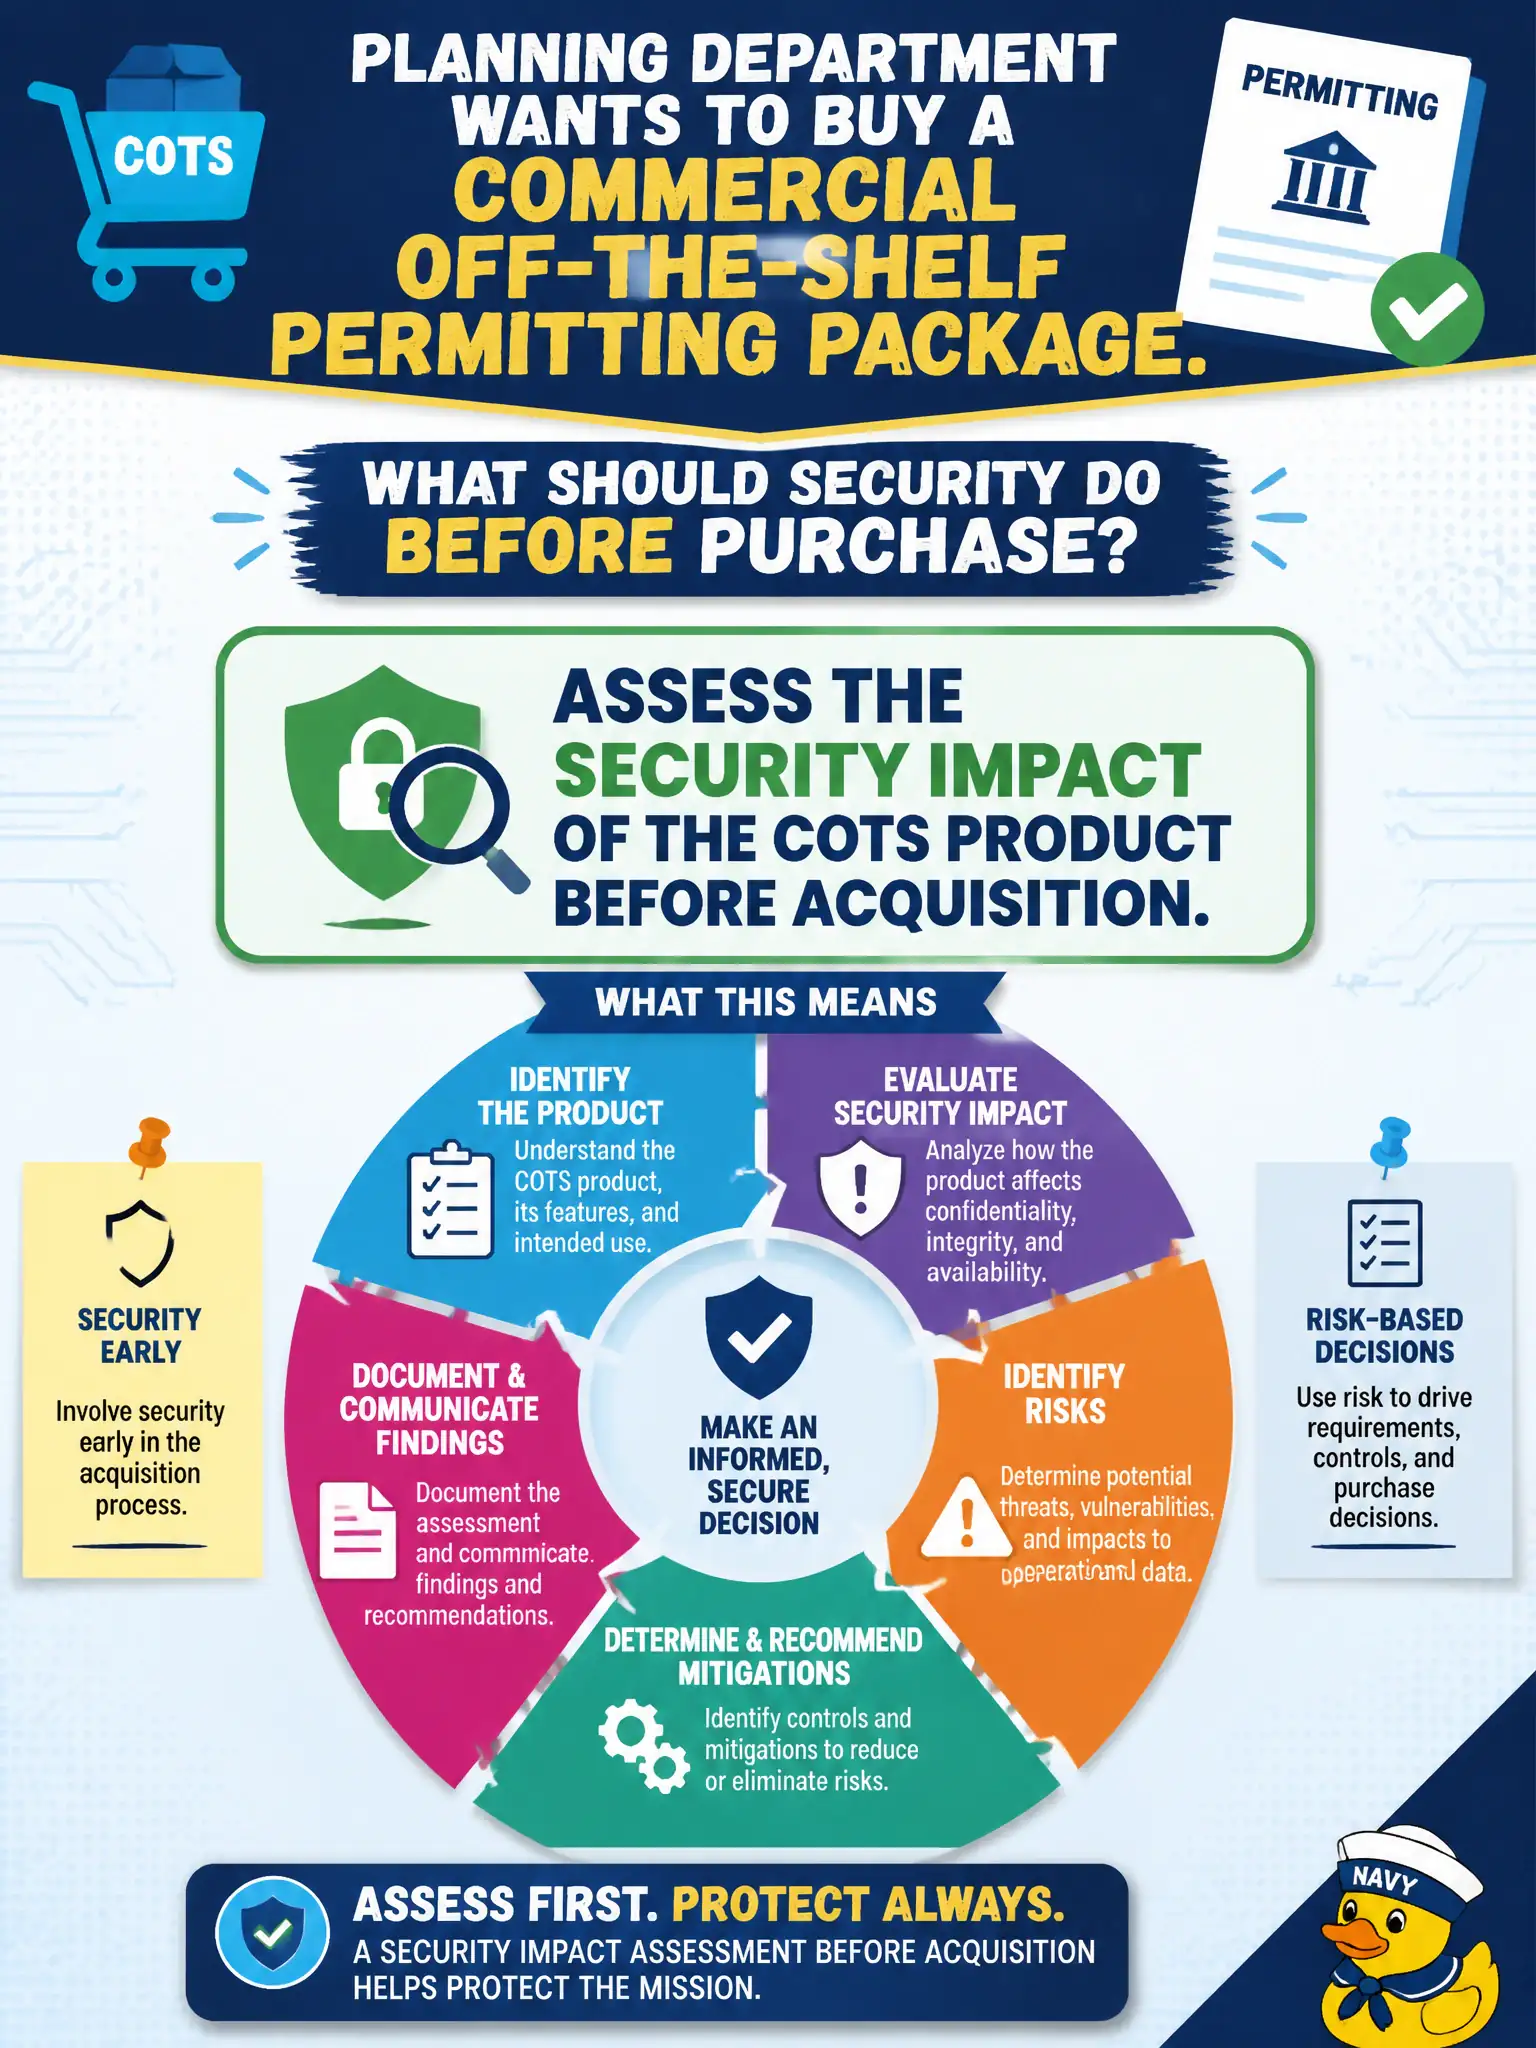
The planning department wants to buy a commercial off-the-shelf permitting package. What should security do before purchase?
Select an answer to reveal the explanation.
Short Explanation
Buying a shiny permitting package is still adopting someone else's risk. Do the security homework before the purchase order—auth, data handling, patch cadence, integrations. COTS is not "secure by brochure."
Full Explanation
Before purchasing a commercial off-the-shelf permitting package, security must assess the security impact of the COTS product—authentication and SSO fit, data residency and encryption, patch cadence, integration surfaces, admin model, logging, subprocessors, and known vulnerabilities. Buying software is adopting another party's design and residual risk into municipal permitting workflows; acquisition-time assessment prevents locking the city into an indefensible platform after funds and process changes are committed.
Skipping review because brand-name vendors never have vulnerabilities is false assurance; major vendors still ship CVEs and misconfigurations.
Installing the trial directly on the production mainframe for realism risks production stability and data exposure; trials belong in isolated evaluation environments.
Mandating that all source be rewritten in-house regardless of cost ignores legitimate COTS value and is not required for security—assessment and contractual controls can manage many COTS risks without a full rewrite.
Exam caveat: COTS and acquired software still require security assessment in Domain 8; brand reputation is not a control. Operational check: run a security questionnaire and architecture review before PO, require right-to-audit/patch commitments in contracts, evaluate in a sandbox with SCA on shipped components where possible, and document residual risk for the permitting business owner.