
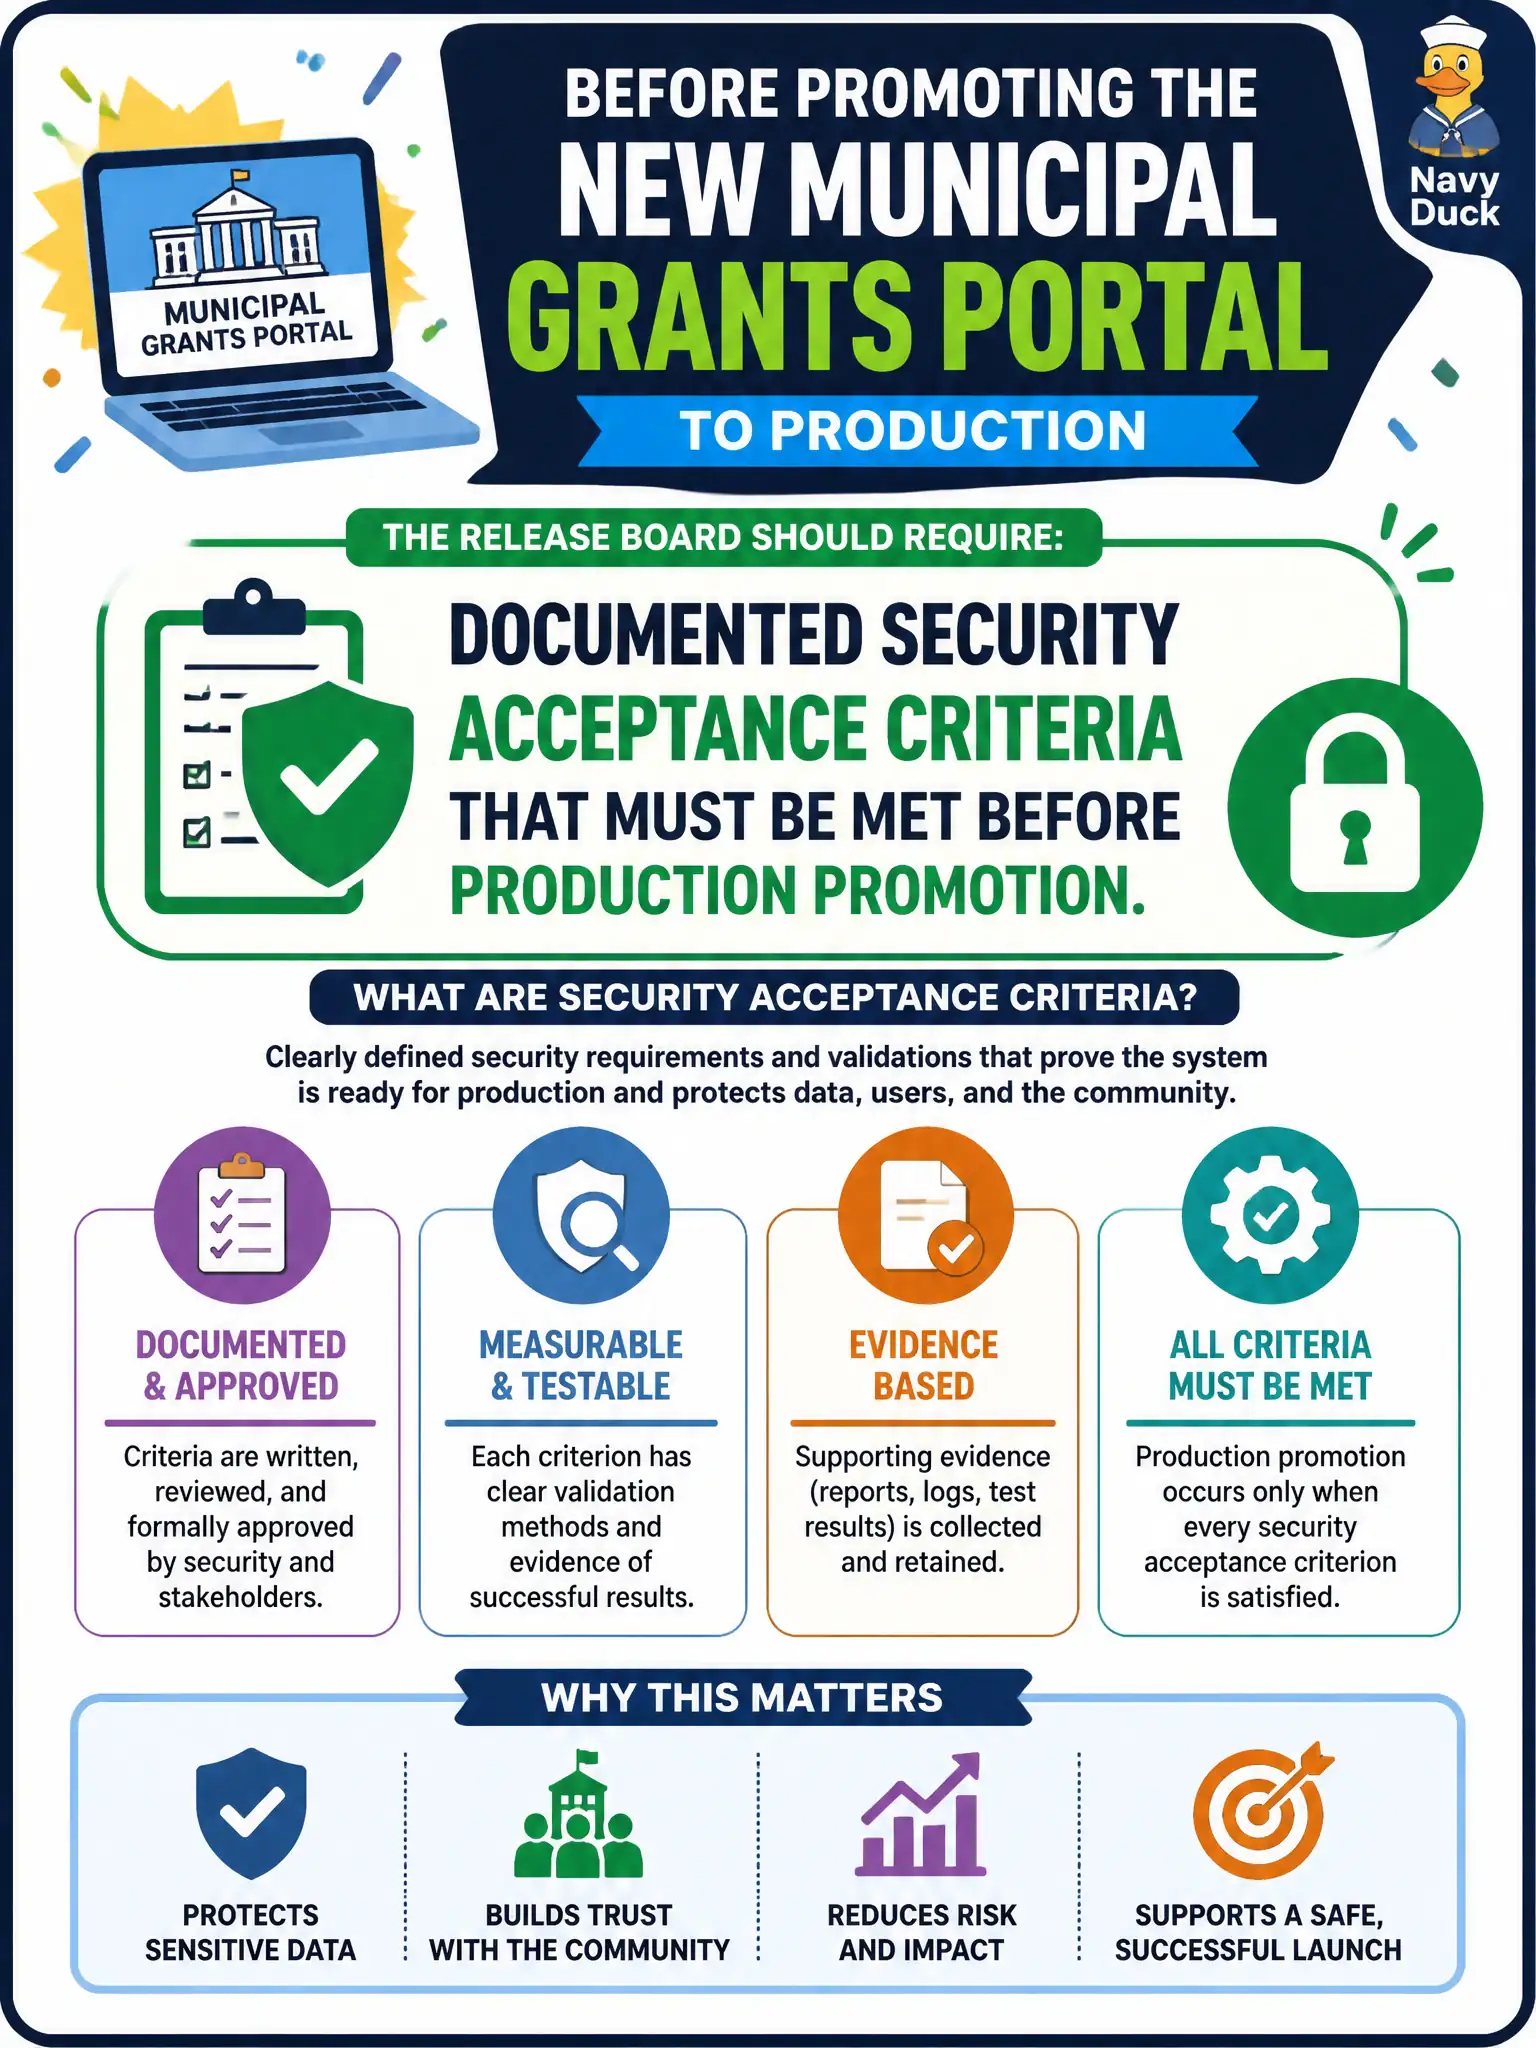
Before promoting the new municipal grants portal to production, what should the release board require?
Select an answer to reveal the explanation.
Short Explanation
Do not ship the grants portal on vibes and a good speech. Write down the security bar—tests passed, critical findings cleared, owners signed off—before production. Acceptance criteria turn "looks fine" into a real gate.
Full Explanation
Before promoting a municipal grants portal to production, the release board should require documented security acceptance criteria that must be met—clear, testable conditions such as critical/high findings resolved or waived with risk acceptance, required SAST/DAST/SCA gates green, secrets scanning clean, authZ tests passed, and logging/monitoring hooks verified. Written criteria turn go-live from opinion into evidence and create a shared definition of done for security on a system that may handle applicant PII and funding decisions.
A promise to run SAST sometime after the ribbon-cutting ceremony postpones assurance until after exposure; acceptance belongs before promotion, not after ceremony.
Unlimited emergency break-glass deploys with no rollback plan normalize uncontrolled change and leave the city unable to recover cleanly when a bad grants release lands.
Removal of all logging to improve perceived performance blinds detection and investigation precisely when a new portal is most likely to show auth and data-handling bugs.
Exam caveat: security acceptance criteria are a release-governance control in the secure SDLC—know that vague future promises are not acceptance. Operational check: attach a security checklist to the change record, require named approvers, verify monitoring dashboards before DNS cutover, and refuse promotion when critical criteria remain open without documented compensating controls and expiry.