
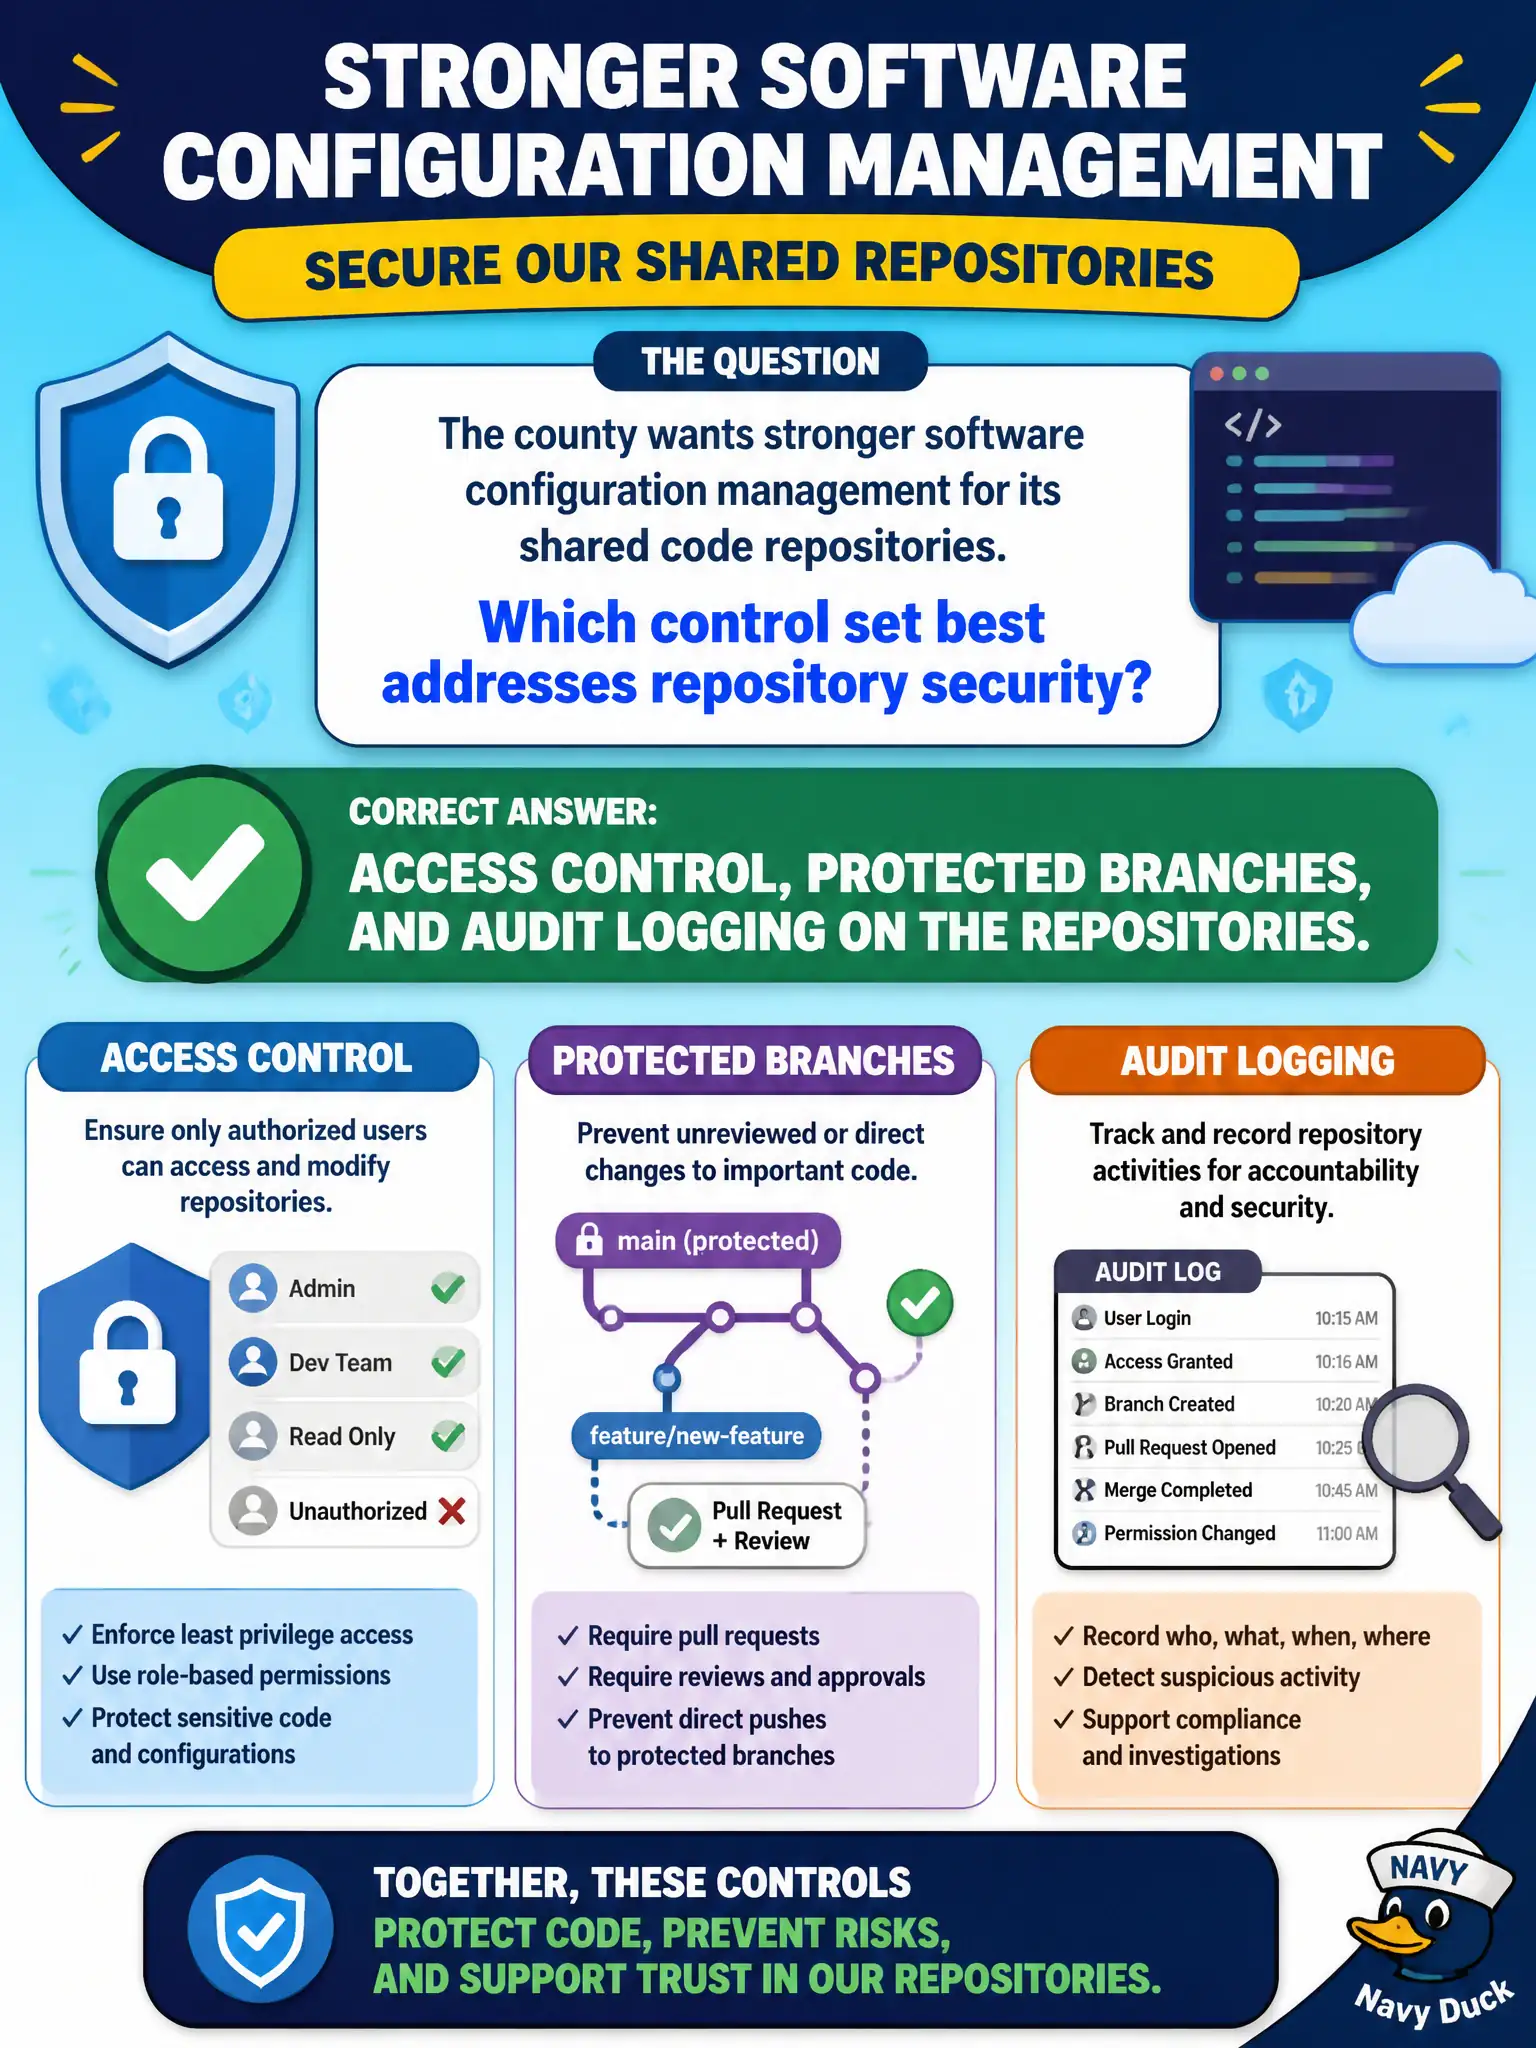
The county wants stronger software configuration management for its shared code repositories. Which control set best addresses repository security?
Select an answer to reveal the explanation.
Short Explanation
Think of the repo like the city's deed vault—not everyone gets a key, and every change leaves a paper trail. Access control, branch protection, and audit logs keep municipal code from getting rewritten in the dark. Configuration management without those controls is just hope.
Full Explanation
Software configuration management for shared county repositories rests on access control, protected branches, and audit logging. Repositories hold source, infrastructure definitions, and sometimes embedded configuration that can affect production. Role-based permissions limit who can read or write sensitive projects; protected branches require reviews and status checks before merge; immutable or tamper-evident audit logs provide accountability for who changed what and when. Together these controls treat the repo as a controlled civic asset rather than an open workshop.
Anonymous write access so volunteers can fix bugs overnight destroys integrity and attribution. Unauthenticated writers can plant backdoors, sabotage builds, or erase history; municipal code must not be world-writable.
Storing production API keys in README files for convenience is a secrets-management failure. READMEs are widely cloned and indexed; embedded production credentials enable lateral movement and data exposure far beyond developer convenience gains.
Disabling commit history to simplify storage quotas removes forensic and rollback value. History supports blame analysis, incident investigation, and safe reverts; storage pressure should be handled with retention policy and LFS—not by erasing the audit trail.
Exam caveat: CISSP links SCM to integrity and accountability—access control, branch protection, and logging are the core set, not convenience anti-patterns. Operational check: enforce SSO/MFA on the code host, protect main/release branches, require CODEOWNERS reviews, ban secrets in repos via scanning, and retain audit logs long enough for municipal investigation and compliance needs.