
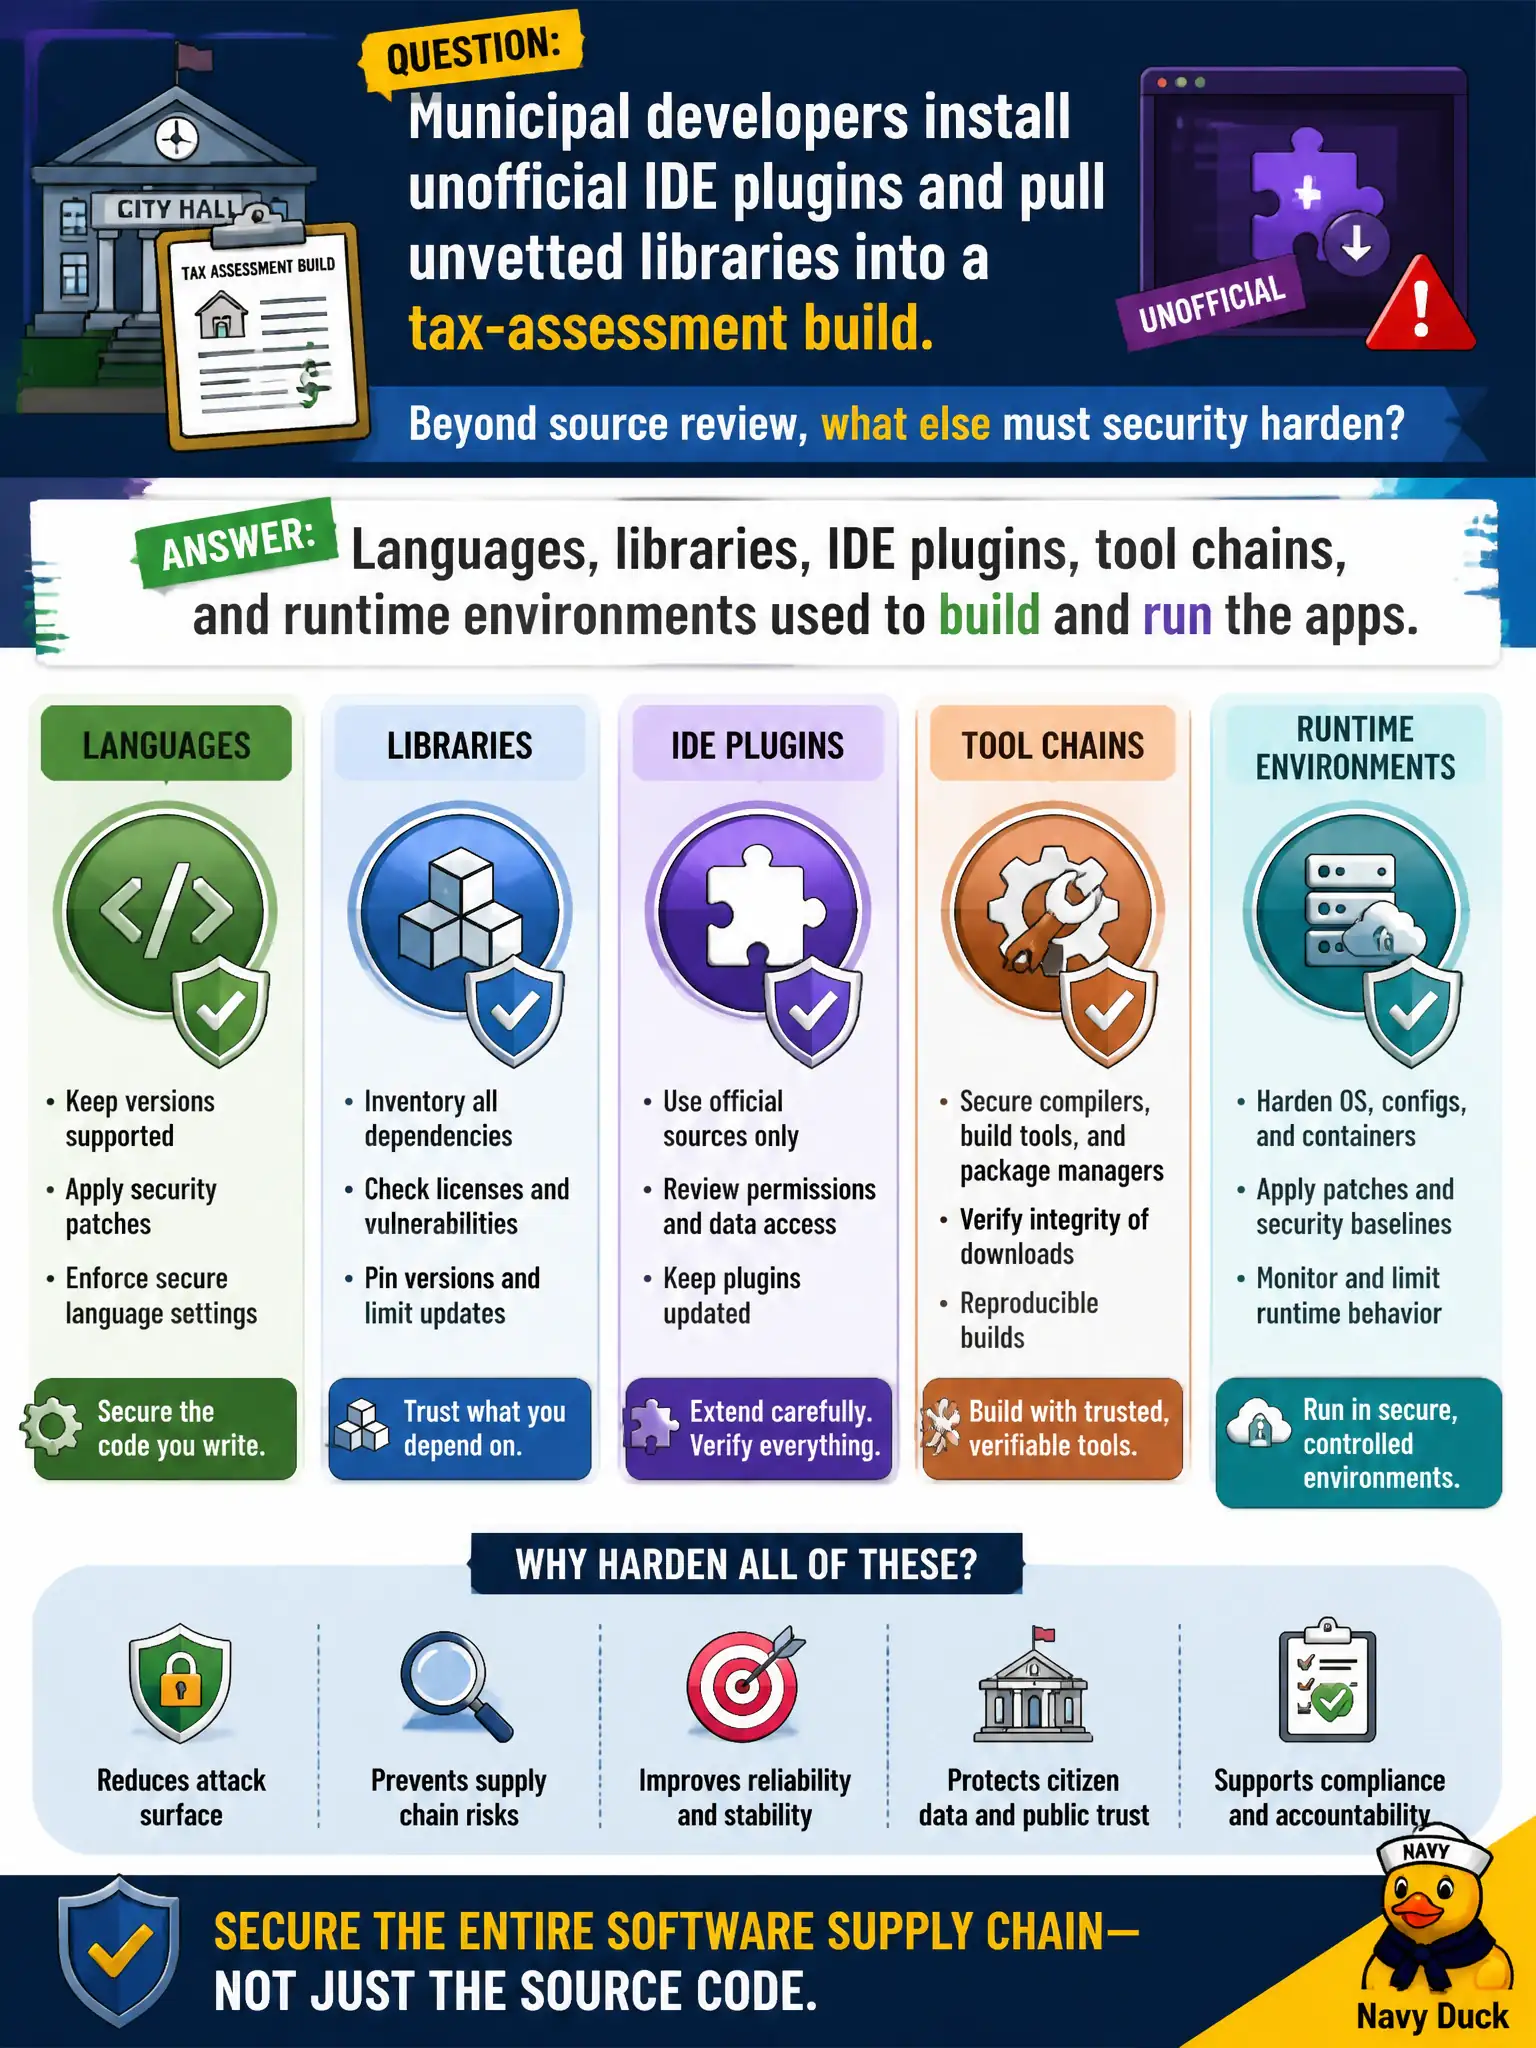
Municipal developers install unofficial IDE plugins and pull unvetted libraries into a tax-assessment build. Beyond source review, what else must security harden?
Select an answer to reveal the explanation.
Short Explanation
It's not just the app code that can bite you—the workshop, the power tools, and the garage matter too. Risky libraries and sketchy IDE plugins are back doors into city projects. Harden languages, libraries, tools, IDEs, and runtimes, not only the finished binary.
Full Explanation
Municipal software security must harden the entire development and runtime toolchain, not only finished application source. Languages, frameworks, libraries, IDE plugins, build agents, package registries, and runtime environments are part of the software supply chain. Unofficial plugins and unvetted libraries can introduce malware, credential theft, weak crypto defaults, or known CVEs before a line of city business logic is reviewed. Domain 8 therefore extends assurance to how code is authored, compiled, packaged, and executed for tax-assessment and similar civic workloads.
Limiting attention to public website CMS theme files is far too narrow. Theme files matter for web presentation, but they do not address the compilers, package managers, or IDE extensions used on assessment systems that process parcel and valuation data. Scope must match where untrusted code can execute during build and run.
Physical badge printers in the permit lobby are physical-access controls outside this software-toolchain question. They do not mitigate malicious plugins or vulnerable libraries pulled into a tax-assessment build.
Vendor marketing slides from conferences are not security controls. Marketing does not inventory, pin, scan, or approve components; treating slides as assurance creates a paper comfort gap around real supply-chain risk.
Exam caveat: CISSP Domain 8 includes development environment security and third-party component risk alongside application code review. Operational check: maintain an approved plugin and package allowlist, require SCA and provenance checks in CI, isolate build runners, and periodically audit developer workstations for shadow tooling that bypasses municipal standards.