
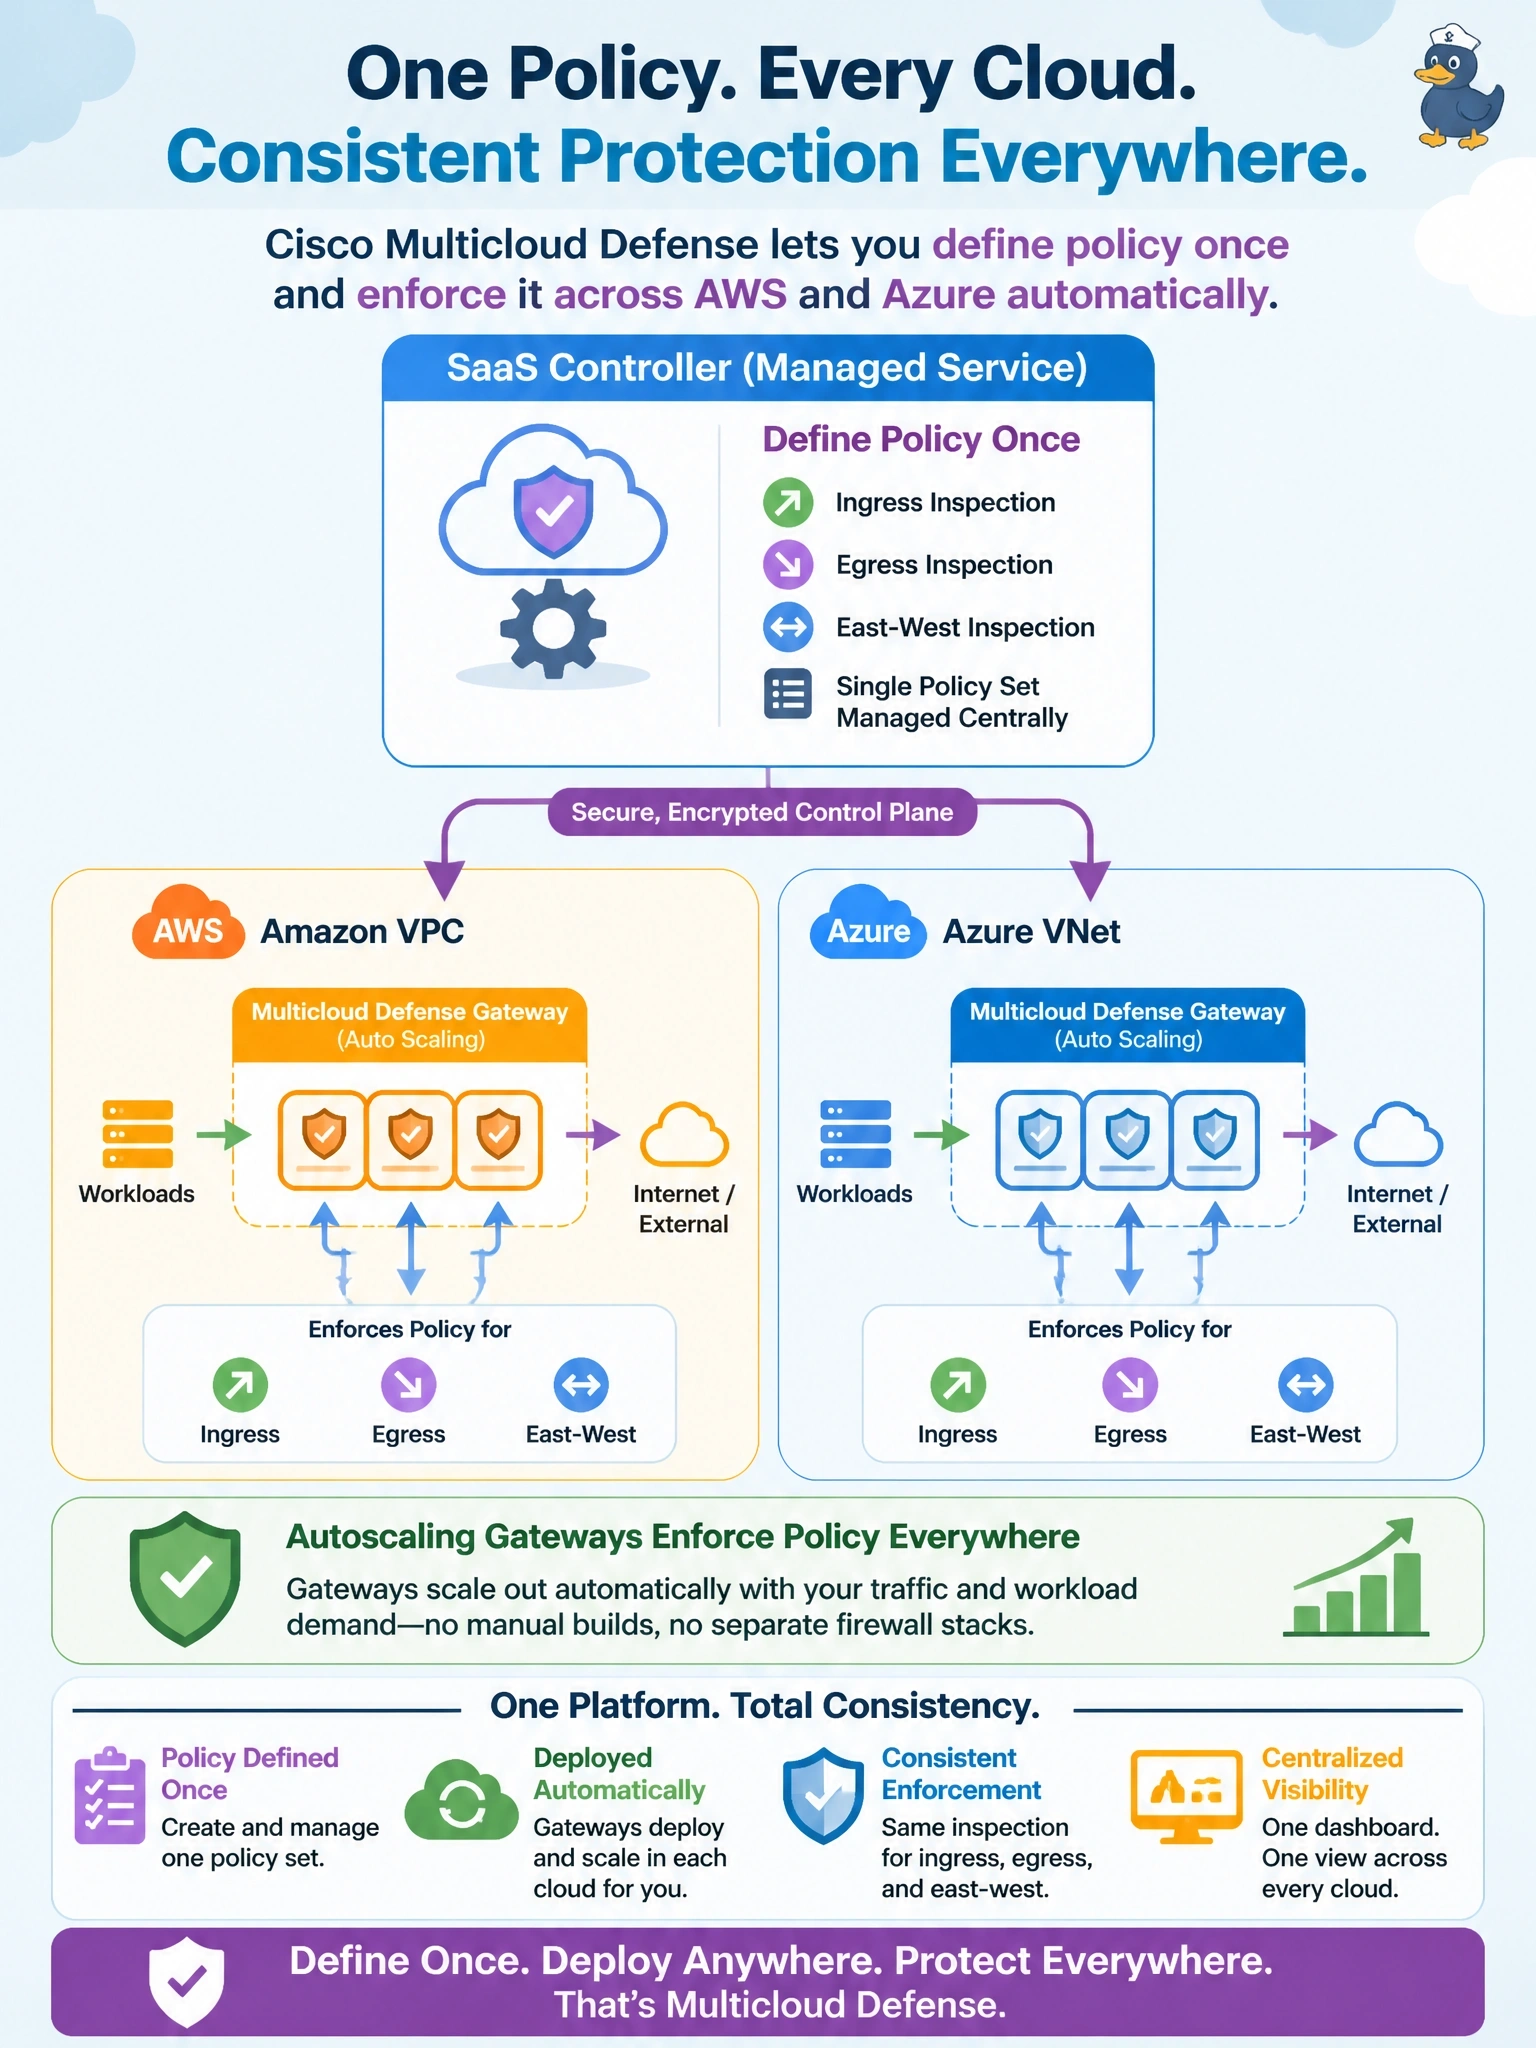
A team runs applications in AWS VPCs and Azure VNets and must apply ingress, egress and east-west inspection with one policy set managed centrally, without hand-building and scaling separate firewall stacks in each cloud. How does Cisco Multicloud Defense deliver this?
Select an answer to reveal the explanation.
Short Explanation
Think of a head chef who writes one recipe and sends cooks to every kitchen you run. Multicloud Defense works that way: a SaaS controller holds the policy and drops autoscaling gateways into each cloud to enforce it. Don't confuse it with Secure Workload's agents — that's workload microsegmentation, not network inspection at the cloud edge.
Full Explanation
Cisco Multicloud Defense separates management from enforcement. A cloud-delivered SaaS controller connects to the organization's cloud accounts, discovers assets and holds a single policy set, and it orchestrates Multicloud Defense gateways that run inside the customer's AWS, Azure, Google Cloud or Oracle environments. The gateways scale out and in automatically with traffic and provide ingress, egress and east-west inspection, including capabilities such as intrusion prevention, URL and FQDN filtering and TLS decryption. Because the controller automates the cloud networking constructs and gateway lifecycle, the team avoids building and scaling separate firewall stacks per cloud. A Secure Workload agent enforces microsegmentation at each workload through the host firewall; that is valuable, but it is a different product and is not a cloud network inspection gateway. A Secure Access network tunnel sends branch or site traffic to Cisco points of presence for internet security; it does not provide east-west inspection between cloud workloads. Splunk ingests and correlates data but does not sit inline to block sessions. Exam caveat: Multicloud Defense and Secure Workload are complementary in the blueprint; one inspects network paths in clouds, the other segments workloads. Operational check: onboard each cloud account to the controller, confirm gateways are deployed in the intended regions, and verify traffic is steered through them.