
Network administrators log in to IOS XE switches through Cisco ISE using TACACS+. Authentication succeeds and the ISE shell profile returns privilege level 15, yet every administrator lands at the user EXEC prompt. Which missing configuration on the switches explains this?
Select an answer to reveal the explanation.
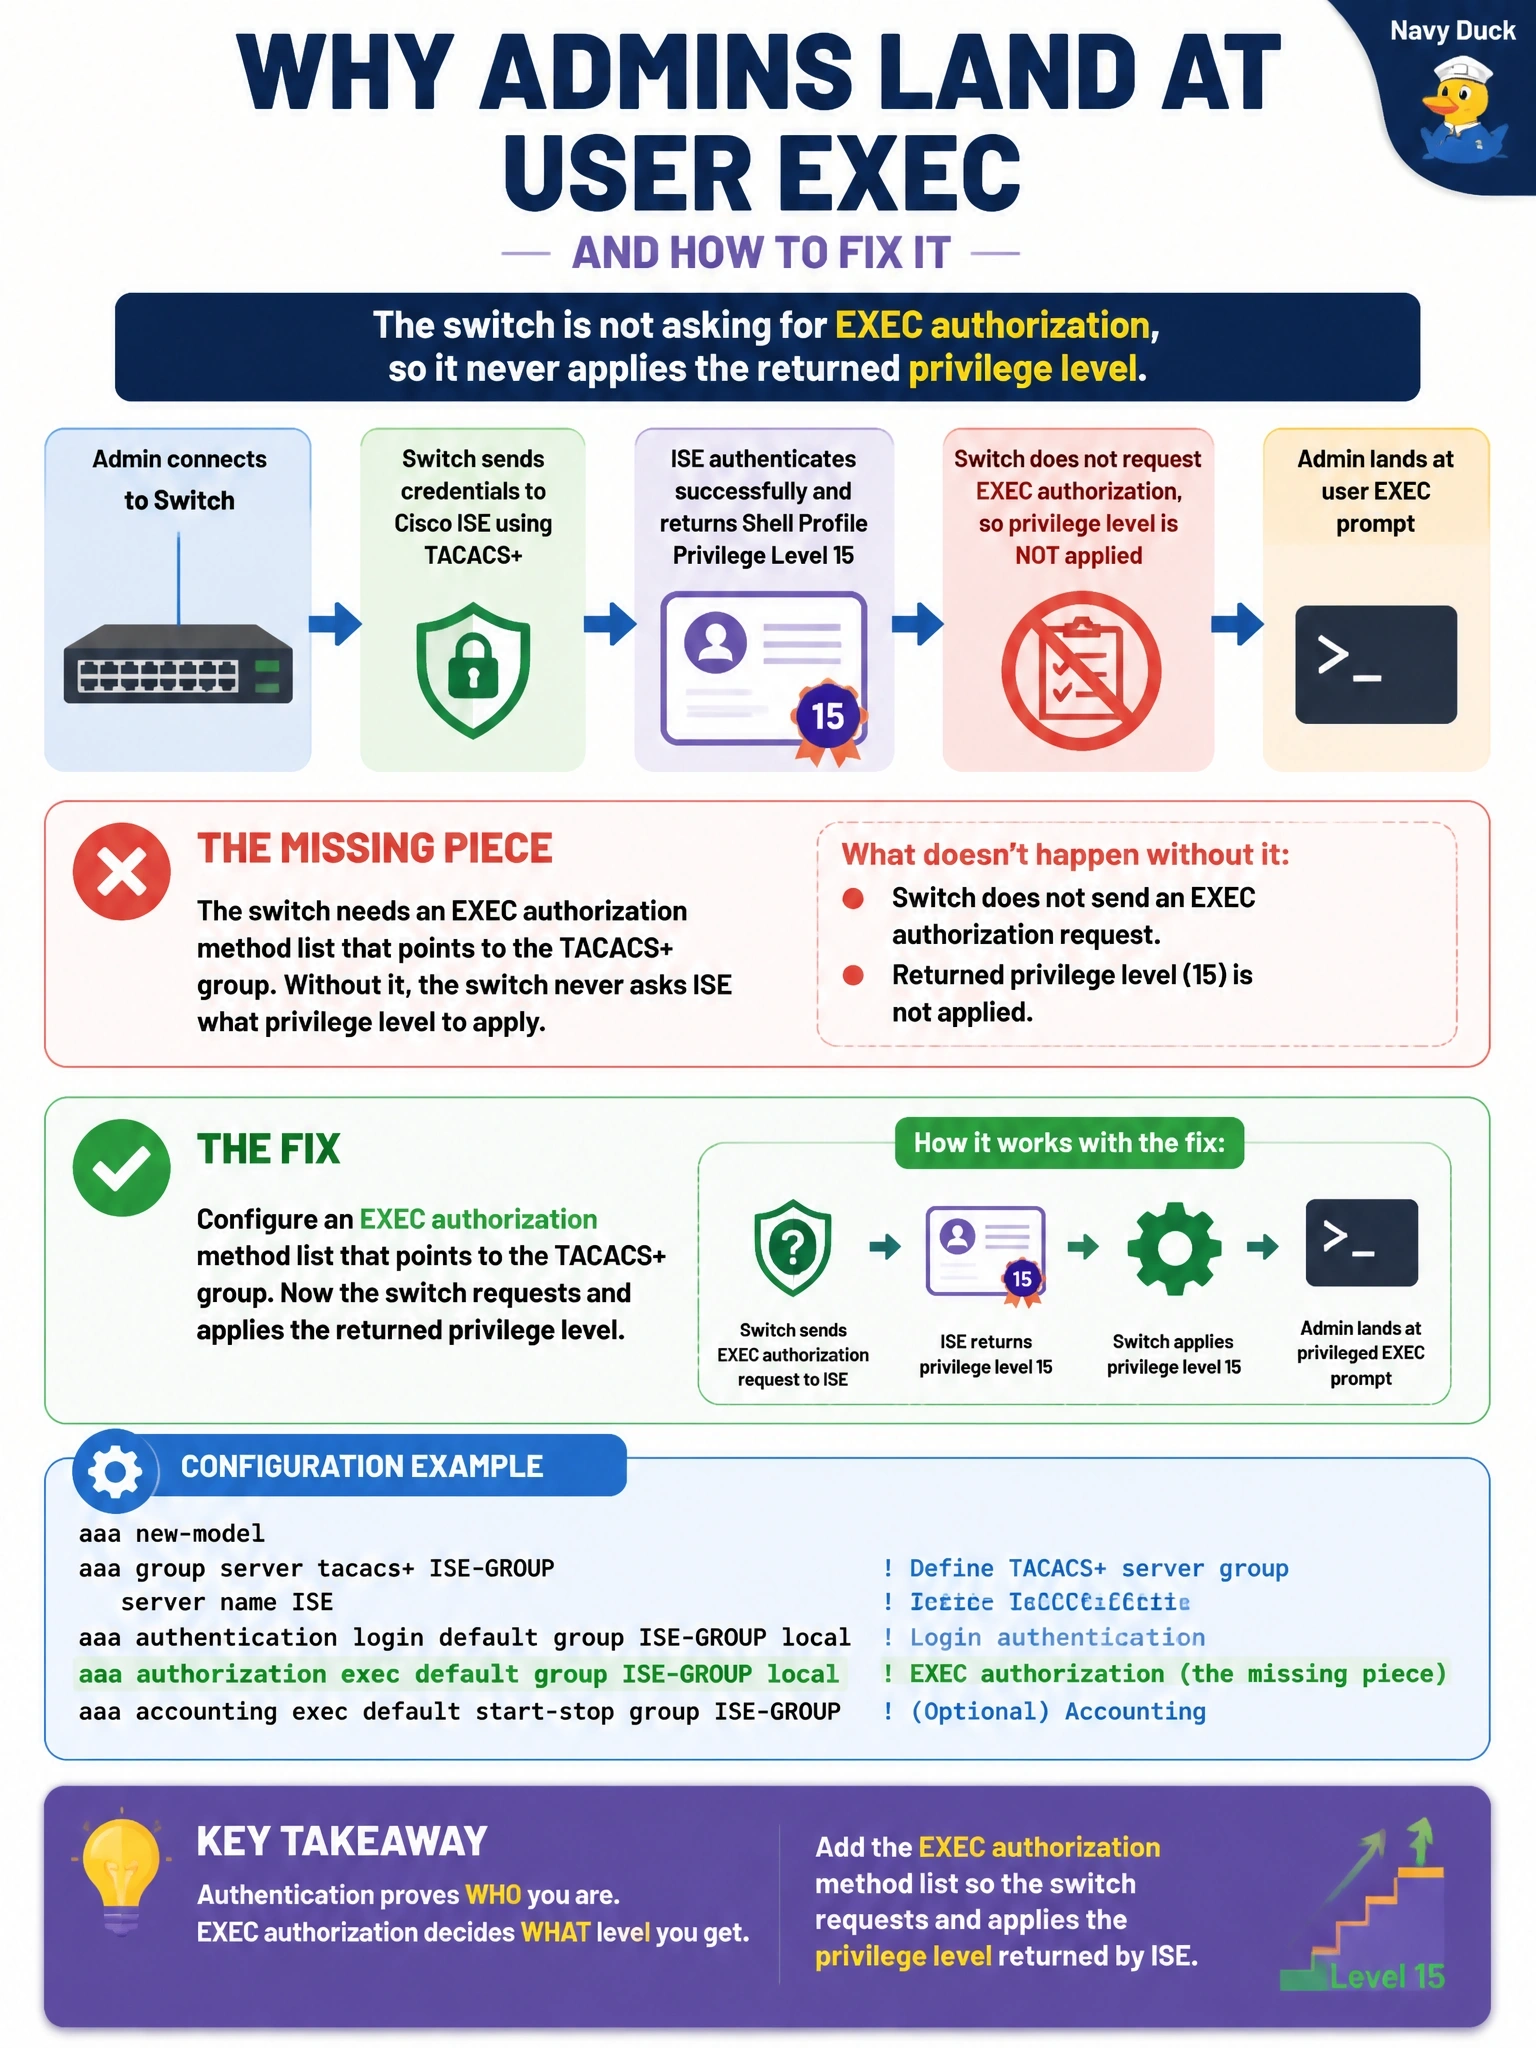
Short Explanation
Here's the deal: authentication just proves who you are, it doesn't hand you the keys to the building. The switch has to ask the server what you're allowed to do, and it only asks if exec authorization is configured. Don't fall for the idea that the server pushes privilege on its own; no authorization request, no privilege level.
Full Explanation
TACACS+ separates authentication, authorization and accounting into independent exchanges. Authentication confirms identity, but the privilege level in a shell profile is delivered in an authorization response, and the device sends an authorization request only when an exec authorization method list is configured to use the TACACS+ group. Without that list, the switch authenticates the user, never asks for attributes, and places the session at its default user EXEC level, which matches the symptom. Adding a second server affects redundancy, not attribute handling; a single reachable server is fully able to return privilege information. Accounting records session start, stop and commands for audit, but accounting replies carry no authorization attributes, so an accounting list cannot raise privilege. Switching to RADIUS is based on a false premise: TACACS+ carries privilege level natively in its authorization exchange and is the preferred protocol for device administration precisely because it keeps authorization separate. Exam caveat: when authentication succeeds but rights are wrong, look at authorization on both the device and the server before blaming credentials. Operational check: add exec authorization to the TACACS+ group on the switch, log in again, confirm the privilege level with a show privilege command, and verify in the ISE TACACS live log that an authorization request was received and the expected shell profile was returned.