
A newly installed access switch is configured to send 802.1X requests to Cisco ISE. Ping from the switch to ISE succeeds, but endpoints time out and the RADIUS server never answers the switch, not even with an Access-Reject. What is the most likely cause?
Select an answer to reveal the explanation.
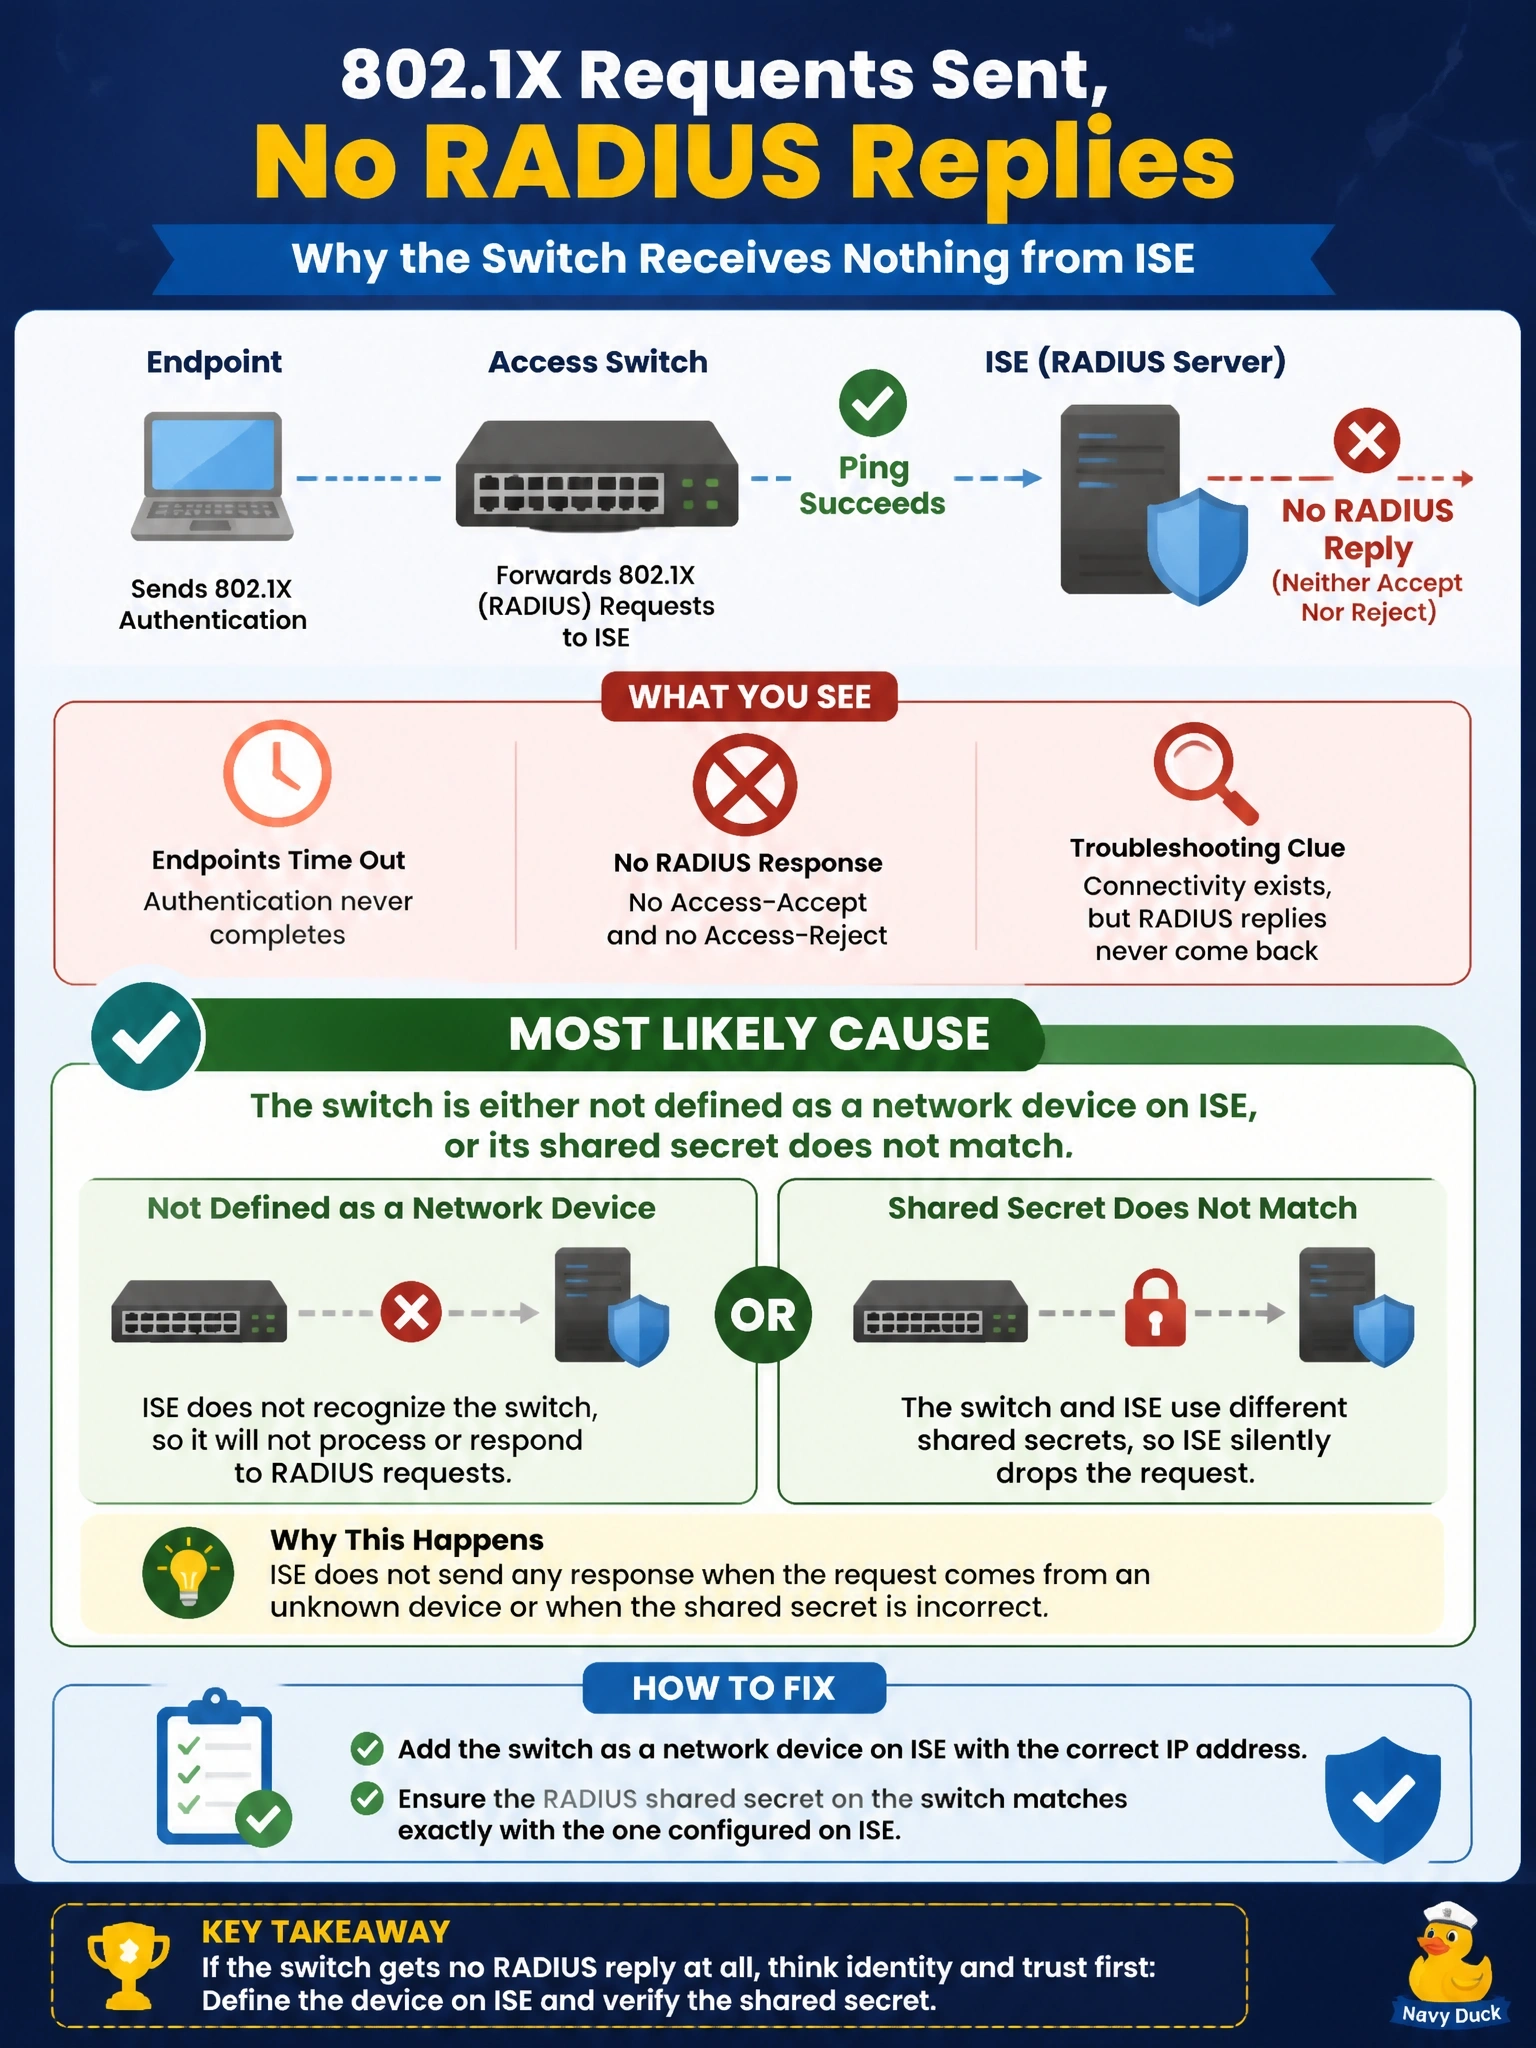
Short Explanation
Think of RADIUS like a members-only club: if the bouncer doesn't know you, he doesn't argue, he just ignores you. A NAD that isn't defined on the server, or one using the wrong shared secret, gets silence instead of a reject. The trap is blaming users or policy, because both of those would produce an Access-Reject you can actually see.
Full Explanation
RADIUS trust between a network access device and the server rests on the server knowing the client and sharing a secret with it. RFC 2865 says a request from a client for which the server has no shared secret must be silently discarded, and a request whose authenticator fails verification under the configured secret is likewise unusable. The visible symptom is exactly the one described: IP reachability is fine, yet the switch sees timeouts rather than any response, so it marks the server dead or retries forever. Disabled directory accounts are a credential problem that ISE can only report after it has accepted and processed the request, which means the switch would receive an Access-Reject. A missing authorization rule is similar: authorization runs after a valid request is parsed, and a default deny also returns a reject that the switch can log. Sending accounting to UDP 1813 does not explain authentication timeouts, because authentication and accounting are separate exchanges and an accounting mismatch leaves authentication on 1812 untouched. Exam caveat: silence points to the transport or trust layer, while a reject points to identity or policy. Operational check: confirm the switch's source IP exactly matches the network device entry on ISE, re-enter the shared secret on both sides, and look in ISE logs for unknown-device or bad-authenticator entries.