
A university replacement MDS is rejected when it joins the SAN. Fabric binding already lists that switch WWN, paired with a domain ID the switch is not running. What has to match before the switch is allowed in?
Select an answer to reveal the explanation.
Short Explanation
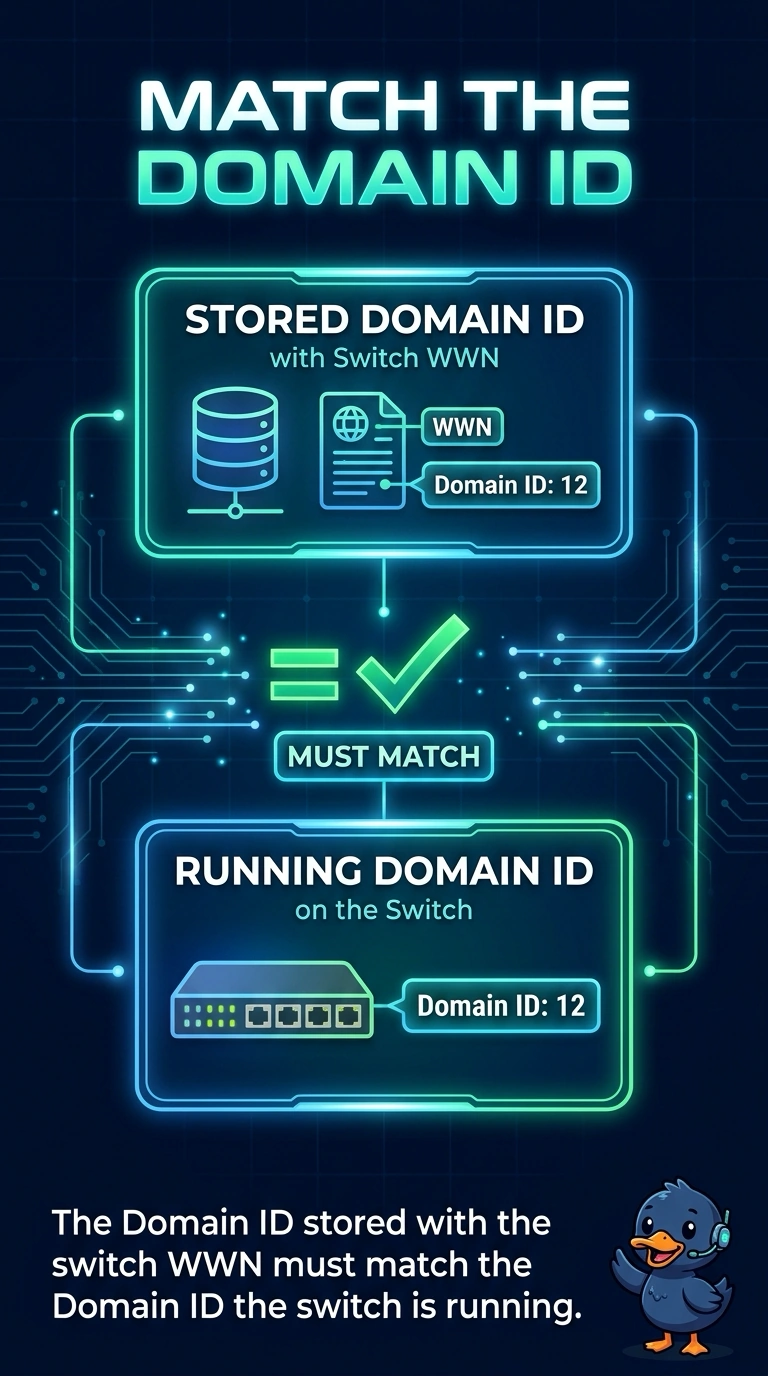
The guest list has your name, and the wrong seat number. Fabric binding allows a switch WWN only together with the domain ID you recorded for it. The WWN being present is not enough when the running domain ID is different.
Full Explanation
Fabric binding checks the identity of a switch that wants to join, not the identity of a host. The entry is the switch WWN plus the domain ID that switch is allowed to use. A replacement that presents the listed WWN and a different domain ID fails the check until those two values agree, either by correcting the binding entry or by bringing the switch up with the allowed domain ID. A host PWWN bound to an F port is port security. It does not admit a switch. The default-zone policy controls traffic among devices that are in no zone, and the zoneset name is not a switch identity. A TACACS key checks operator logins. It is not the fabric membership test. Caveat: binding is enforced per VSAN, so a domain ID that is legal in one VSAN can still be rejected in another. Operational check: compare the switch WWN and the runtime domain ID in that VSAN with the binding entry before you try the ISL again. Host port security and operator AAA stay out of this check. A switch can pass both of those and still be refused at the ISL when the binding's domain ID is wrong.