
A regional hospital UCS domain has several organizations. One administrator should create service profiles only inside the imaging organization and should not see the others. The account already has a server-admin role. What else is required?
Select an answer to reveal the explanation.
Short Explanation
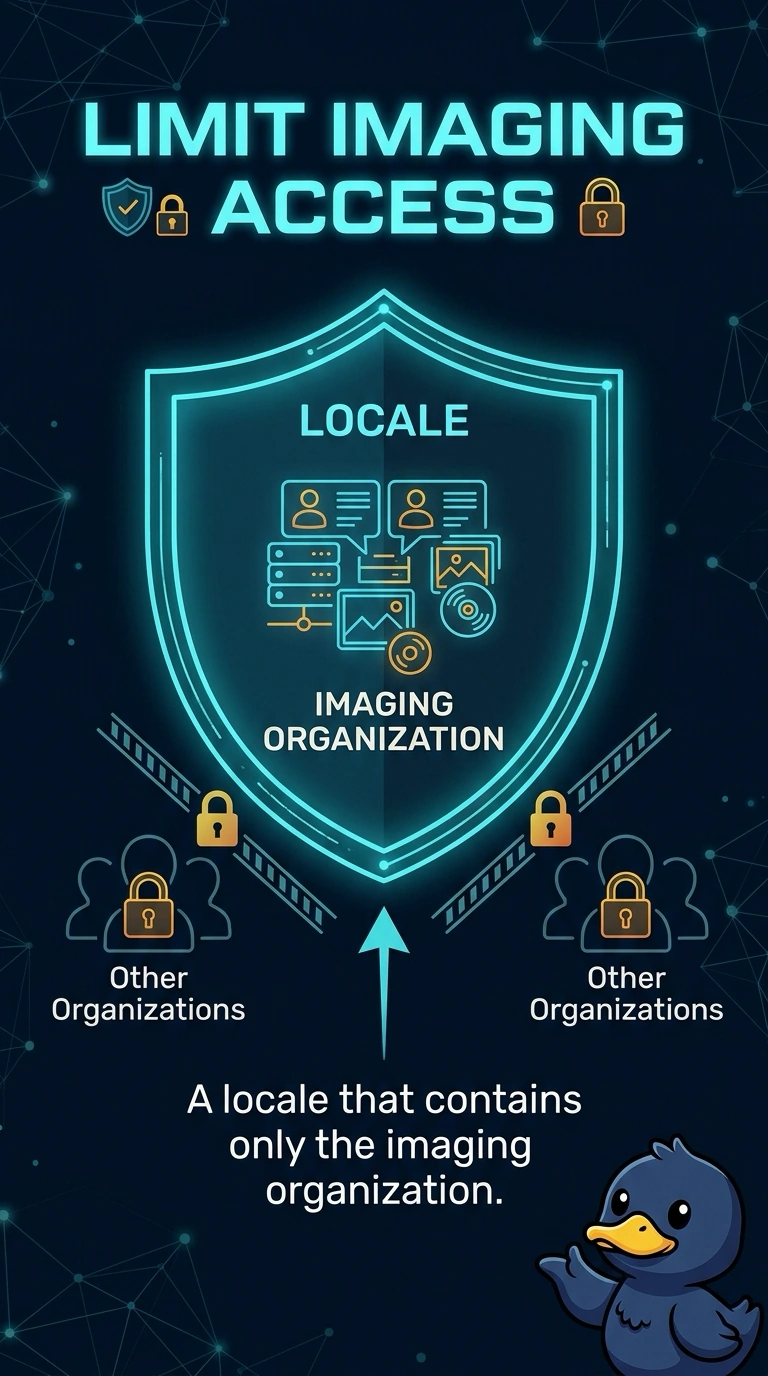
A role is the set of tools on the cart. A locale is which rooms you may roll it into. You already gave this person the server-admin tools, so you still have to limit the locale to the imaging organization or they can open every door in the hospital domain.
Full Explanation
UCS Manager separates what an account may do from where it may do it. The role, such as server-admin, grants operations like creating service profiles. The locale lists the organizations those operations apply to. An account with the right role and a locale that contains only the imaging organization can work there and is not granted the other organizations. Adding another fabric interconnect cluster would split the domain into separate equipment, which is far beyond an authorization change and is not how org visibility is limited. A BIOS policy sets firmware-visible hardware options for servers that use it. The policy name does not confine an administrator to an organization. MDS port security binds a Fibre Channel PWWN to an F port. It has no effect on which UCS organizations an account can see. Caveat: if the account also has a locale of the root organization, that broader locale still exposes the other orgs, so you remove the wide locale rather than only adding the narrow one. Operational check: sign in as the imaging administrator, confirm service profiles can be created in that org, and confirm the other organizations are not available in the session.