
A game studio can log in to Nexus switches, and the team cannot tell which account entered a configuration command after an outage. Authentication already works. Which AAA function records those commands?
Select an answer to reveal the explanation.
Short Explanation
Authentication only checks the badge at the door. You turn on accounting so the badge swipe is written down next to every configuration command. A routing key chain does not keep that diary.
Full Explanation
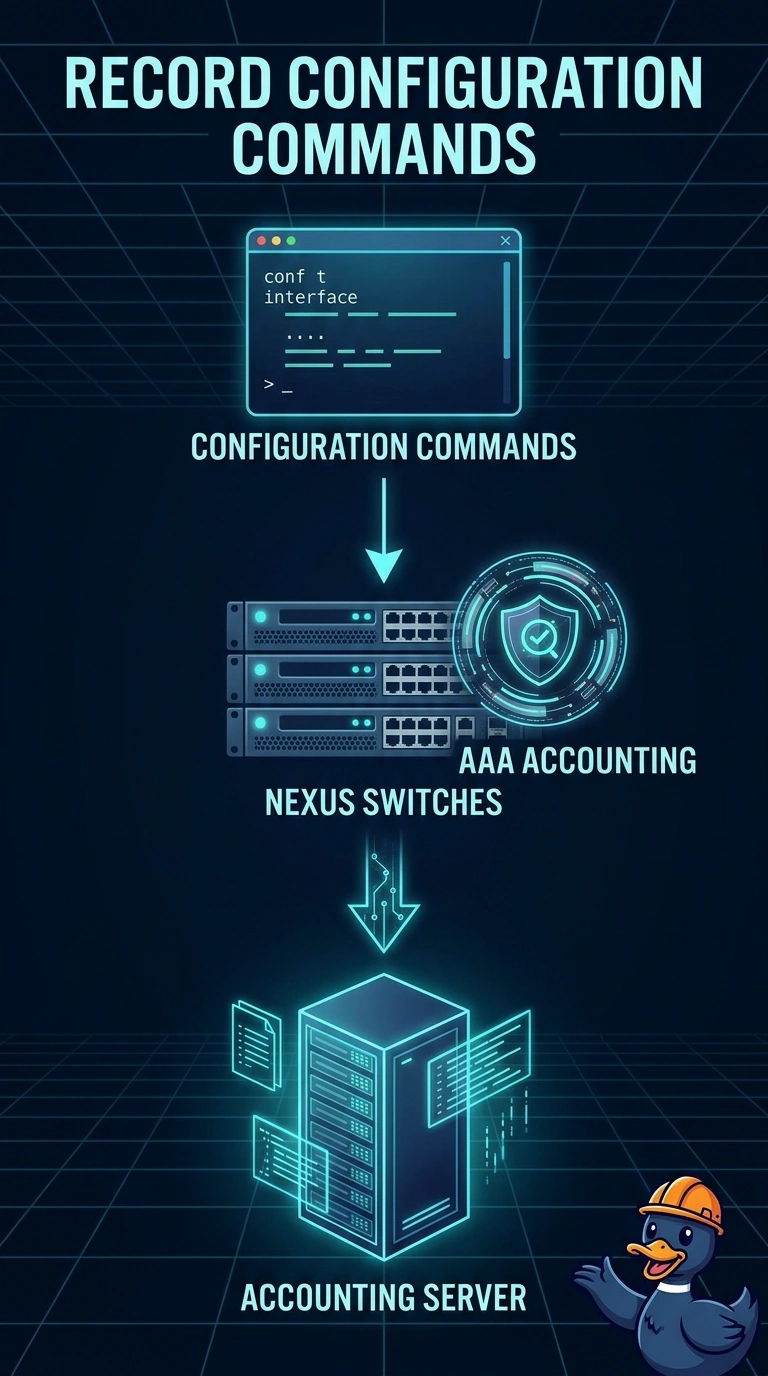
AAA accounting records what an authenticated session does. On NX-OS, accounting for configuration commands sends those commands, with the user and the time, to the configured accounting server. Authentication already works for the studio, so the missing function is accounting, not another login method. An OSPF key chain authenticates routing peers. It does not write CLI commands into the link-state database. MACsec encrypts link frames. It does not store a transcript of configuration commands, on the console or anywhere else. A SPAN session of the management port copies frames. Someone could try to reconstruct a session from a capture, and that is not the AAA accounting record the switches are built to emit. Caveat: accounting shows what was sent to the server. If the server was unreachable and you have no local fallback log, the outage window can still be blank, so confirm the accounting path before you need it. Operational check: enter a harmless configuration command as a test user and confirm the accounting server shows that user, that command, and the time.