
A government agency account in UCS Manager can change every organization, but this person should keep the same privileges and touch only one organization. Which control adds that boundary?
Select an answer to reveal the explanation.
Short Explanation
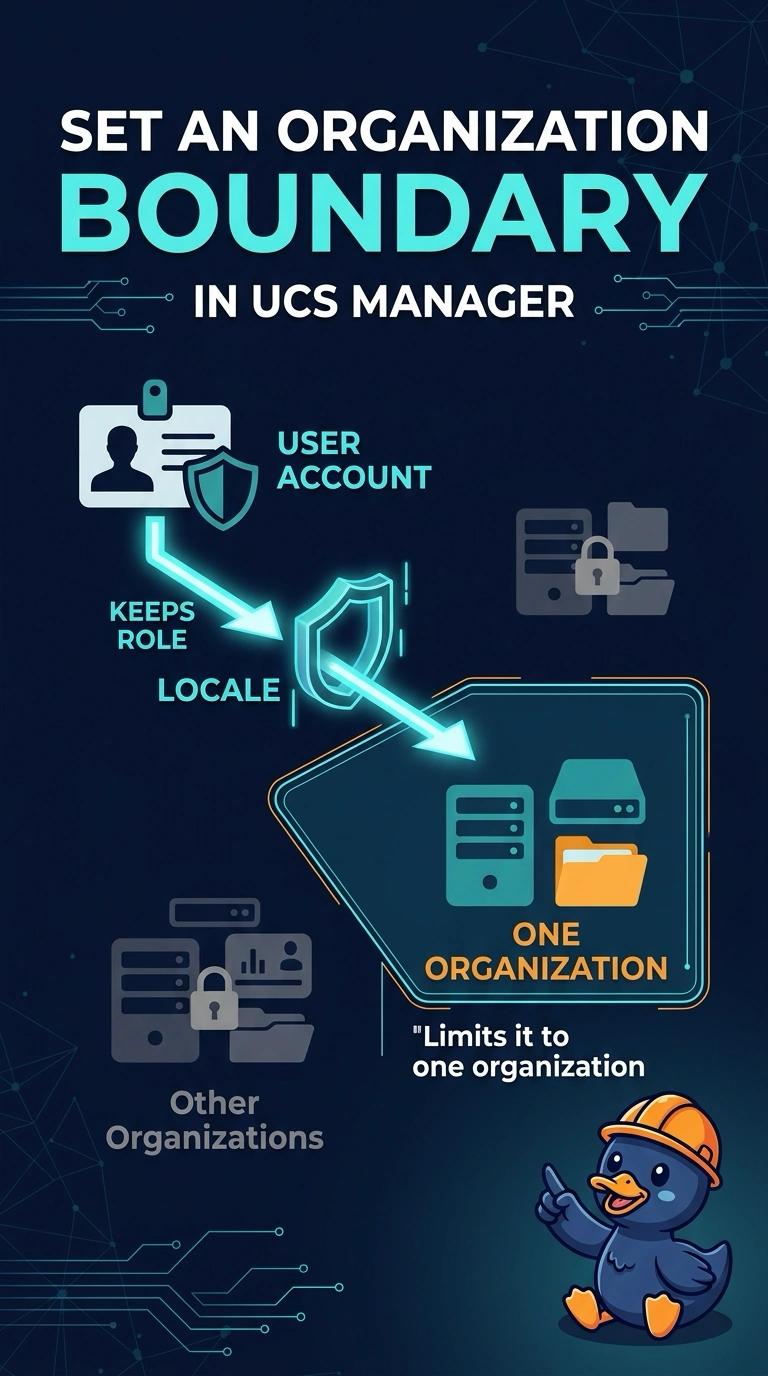
A job title says what you are allowed to do, and a badge reader says which floor you may enter. You keep the same UCS role and add a locale so the account can work in only one organization. Another login method does not draw that boundary, because it only decides how the person proves who they are.
Full Explanation
UCS Manager separates privileges from scope. A role decides which operations an account may perform, and a locale decides which organizations those operations apply to. This agency account already has the right privileges and is missing the scope, so the fitting control is a locale pointed at the one organization. An authentication domain selects the provider that checks the password, such as local accounts or an external server. It does not limit which organizations a successful login can see. The fabric interconnect cluster address is the management target for the whole domain. Logging in there does not confine the session to one chassis or one organization. A maintenance policy controls when a disruptive server change is allowed to proceed. It does not hide the other organizations from an account that can already open them. Caveat: the built-in admin account is not a good stand-in for this scoped operator, so the locale has to be applied to the account people actually use. Operational check: sign in as that user, confirm the chosen organization is writable, and confirm the other organizations are not available for changes.