
A regional hospital wants only one known host PWWN to complete FLOGI on a specific MDS F port. A different HBA plugged into that same port should be rejected before it gets a fabric address. What enforces that?
Select an answer to reveal the explanation.
Short Explanation
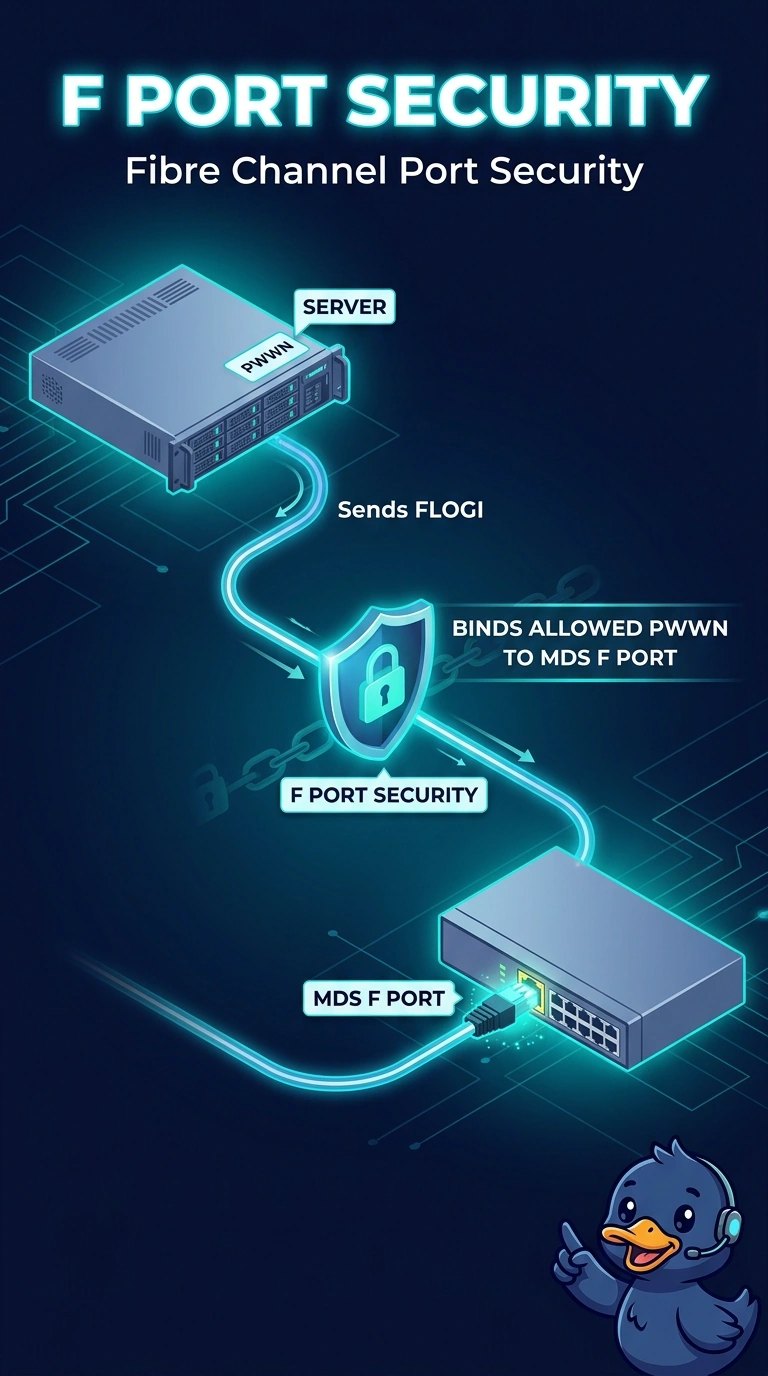
Port security is the door list for one F port. You bind the known host PWWN to that port so a different HBA cannot complete FLOGI there. A zone decides who may talk after login, and it does not reserve the port.
Full Explanation
Fibre Channel port security on an MDS binds permitted PWWNs to an interface. When it is enforced on the hospital F port, only the bound host PWWN can complete FLOGI. A different HBA is rejected and does not receive an FCID on that port. That is the control the request describes. A zone decides which logged-in devices may exchange traffic. A stranger can still complete FLOGI on an open F port and receive an address even when zoning later prevents useful communication. Zoning is the wrong layer for reserving the port. Fabric binding checks switch WWNs and domain IDs before a switch joins the fabric. It is not how an F port selects a host HBA, and a host PWWN is not a switch WWN. An fcalias is a VSAN-local nickname in the zoning database. Creating one does not reserve an F port. Caveat: port security has to be activated for the VSAN, or the binding sits in the configuration and still does not reject the stranger. Operational check: plug in the known HBA and confirm FLOGI succeeds, then present a different PWWN on that port and confirm it is rejected.