
A government agency needs a Nexus account that can run show commands and cannot enter configuration mode. An engineer is searching for an IOS-style privilege level. Which NX-OS control enforces this limit?
Select an answer to reveal the explanation.
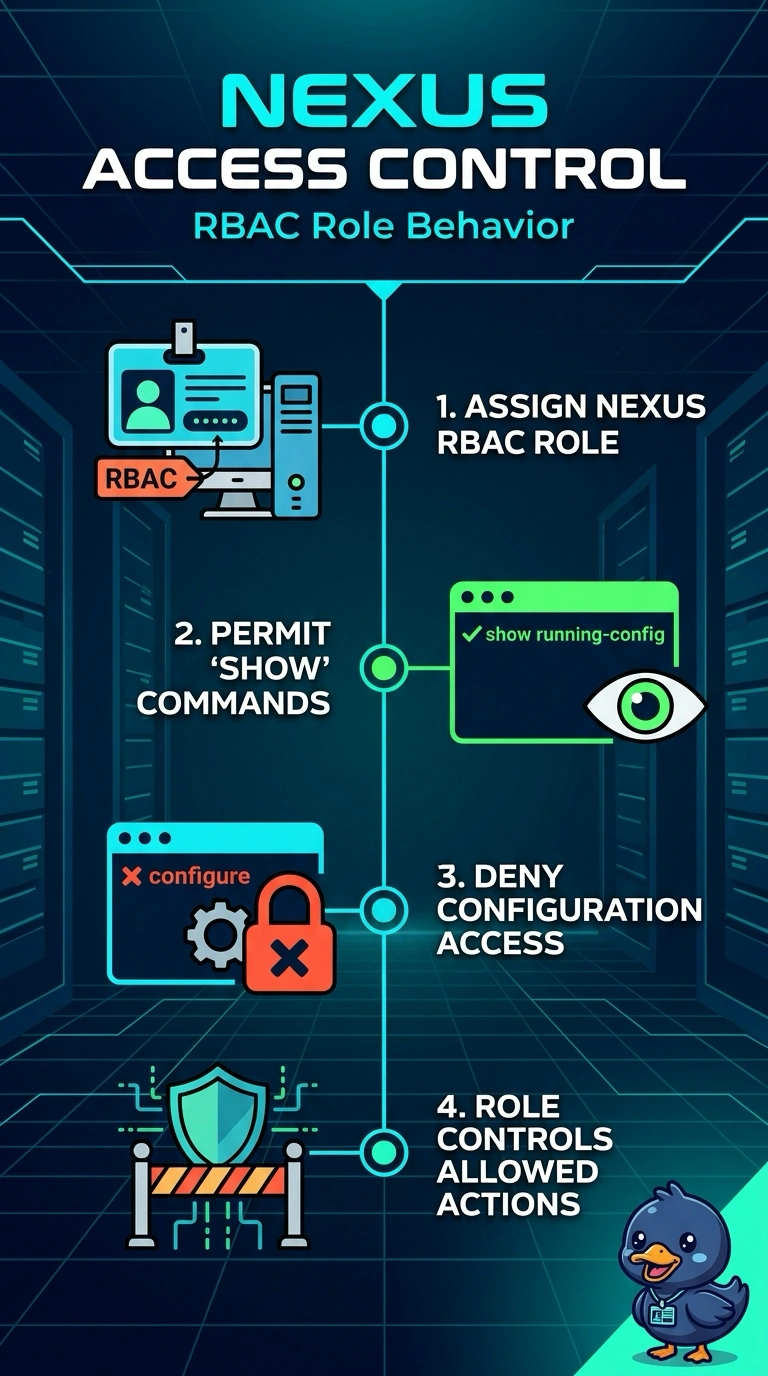
Short Explanation
NX-OS hands out job titles, not a numbered ladder of privilege. You give this operator a role that can look and cannot change, and the switch enforces that on the commands themselves. Picking TACACS+ or local login only decides how the person proves who they are.
Full Explanation
NX-OS authorization is role-based. A role contains rules that permit or deny command families, and the built-in network-operator role is the usual read-only job. A custom role with permit rules for show commands and deny rules for configuration does the same thing for this agency. Authentication, whether local, RADIUS, or TACACS+, only decides whether the login succeeds and which role is assigned. The method list by itself does not describe which commands the session may run. MACsec encrypts frames on a link. It does not filter CLI verbs for a logged-in user. A key chain supplies rotating keys so a routing protocol can authenticate its peers. It has no effect on whether an operator can type configure terminal. Caveat: if the AAA server sends a role the switch does not have, the user can fall back to a default role you did not intend, so the role name has to exist on the switch. Operational check: log in as the operator, confirm show commands work, and confirm configuration mode is rejected without using a network-admin account.