
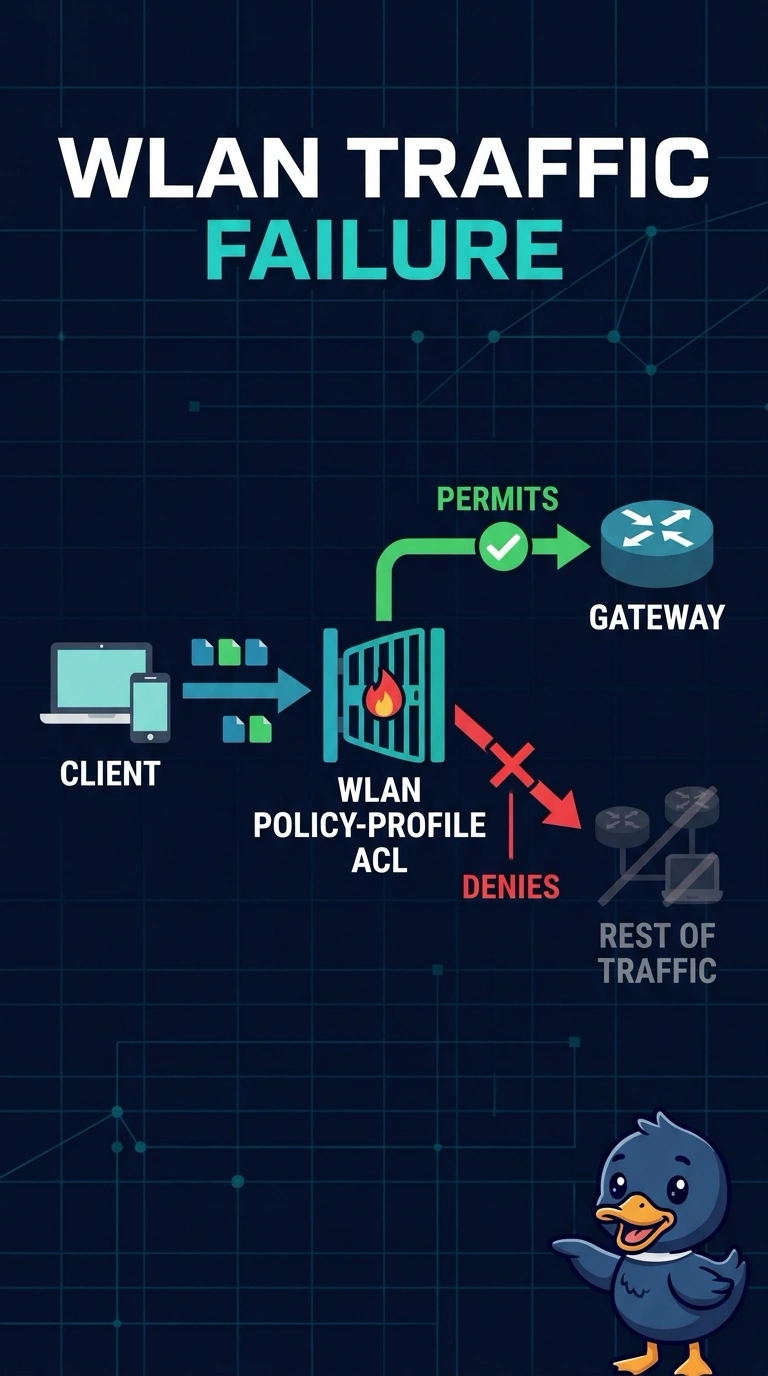
Retail clients associate, receive an address, and can ping their gateway. Traffic beyond the gateway fails. An ACL on the WLAN policy profile denies that traffic. Where is the failure?
Select an answer to reveal the explanation.
Short Explanation
Your clients have an address and the gateway answers, so the radio and the lease did their jobs. The policy profile ACL is the door that lets the ping through and shuts everything else. Turning the antenna does not write that ACL.
Full Explanation
A policy profile on a Catalyst 9800 can apply an ACL to client traffic after the client is on the WLAN. These clients have associated, have an address, and can ping the gateway, so the SSID, the authentication, and DHCP are working. Traffic beyond the gateway fails, and the ACL on that policy profile is the rule doing the denying. The failure is the ACL, not the radio. The PSK is already accepted. A half-accepted passphrase does not produce a working ping and a selective deny of everything else. Beacons advertise the BSS. They do not carry application traffic, and the beacon interval cannot implement an ACL. Antenna gain changes coverage. A client that can ping the gateway has enough signal for that frame, and gain does not selectively block routed traffic while leaving the gateway ping alone. The ACL does exactly that. Exam caveat: an ACL that permits only DHCP and the gateway will look like a successful join and a dead network. Read the hits on the ACL, not only the client state. Operational check: on the policy profile, read the ACL and test one denied destination, then permit a known good destination and confirm that client can reach it.