
A city NOC wants wireless controller events in its existing SIEM, using the controller's own event messages. Which integration does that?
Select an answer to reveal the explanation.
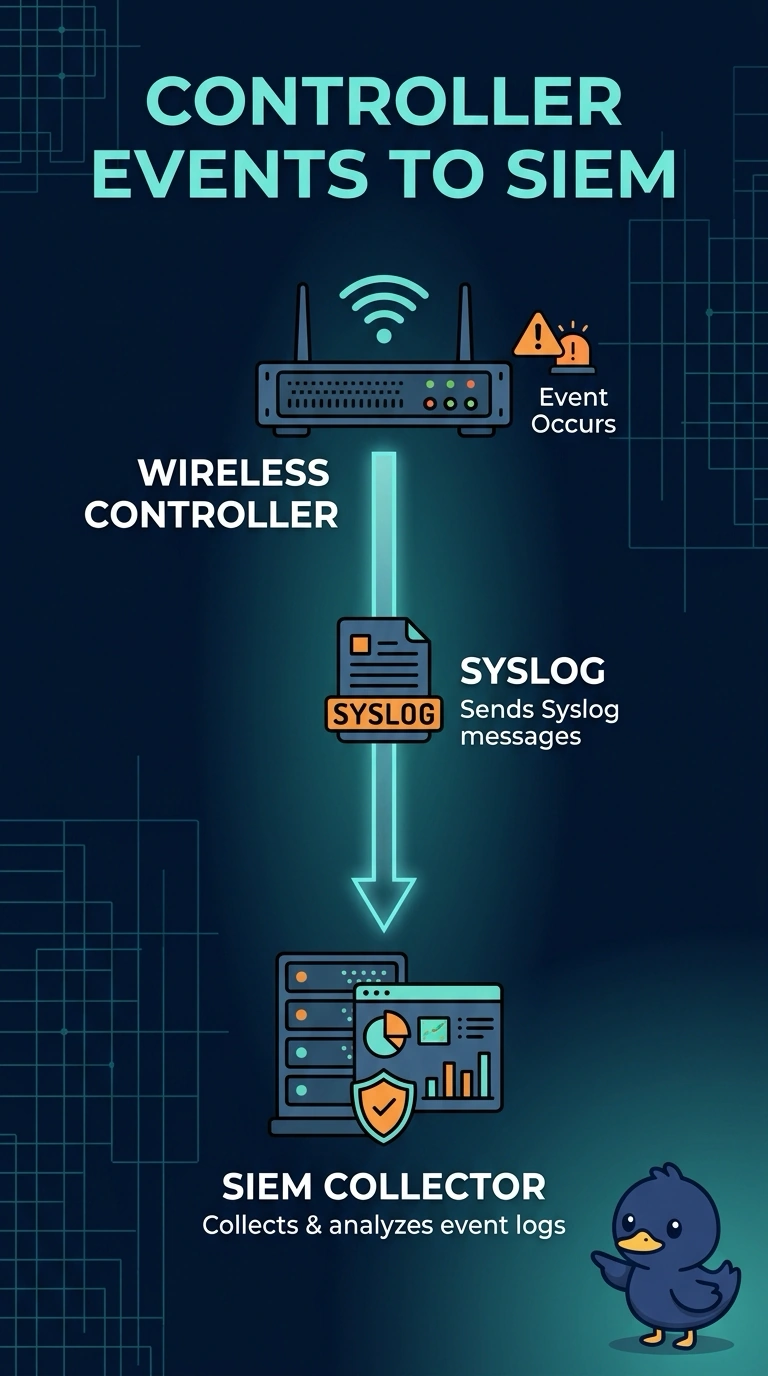
Short Explanation
The SIEM is a log book, and the controller already writes the lines. Point syslog at the collector and your NOC can read them. An RF tag does not ship those events, and a guest VLAN is not an archive.
Full Explanation
Syslog is the controller's event stream. Sending it to the SIEM collector is the integration that puts controller events where the NOC already hunts for problems, without inventing a new event format. The controller can log joins, failures, and security messages, and the SIEM stores and searches them. An RF tag binds radio profiles. It does not forward client frames into a SIEM, and client frames are not the controller event messages the NOC asked for. A guest anchor tunnels guest sessions to a DMZ. It is not a log archive, and the DMZ VLAN does not become the SIEM because guests land there. A monitor-mode access point scans RF. It can help find rogues, and it does not replace controller syslog. The NOC asked for the controller's own events, which the monitor access point does not emit on behalf of the controller. Exam caveat: syslog tells you what the controller recorded. It is not a packet capture and it is not client assurance history. Pick it for events, not for a user's throughput chart. Operational check: generate a test event, confirm it arrives at the collector from the controller address, and confirm the NOC search finds it.