
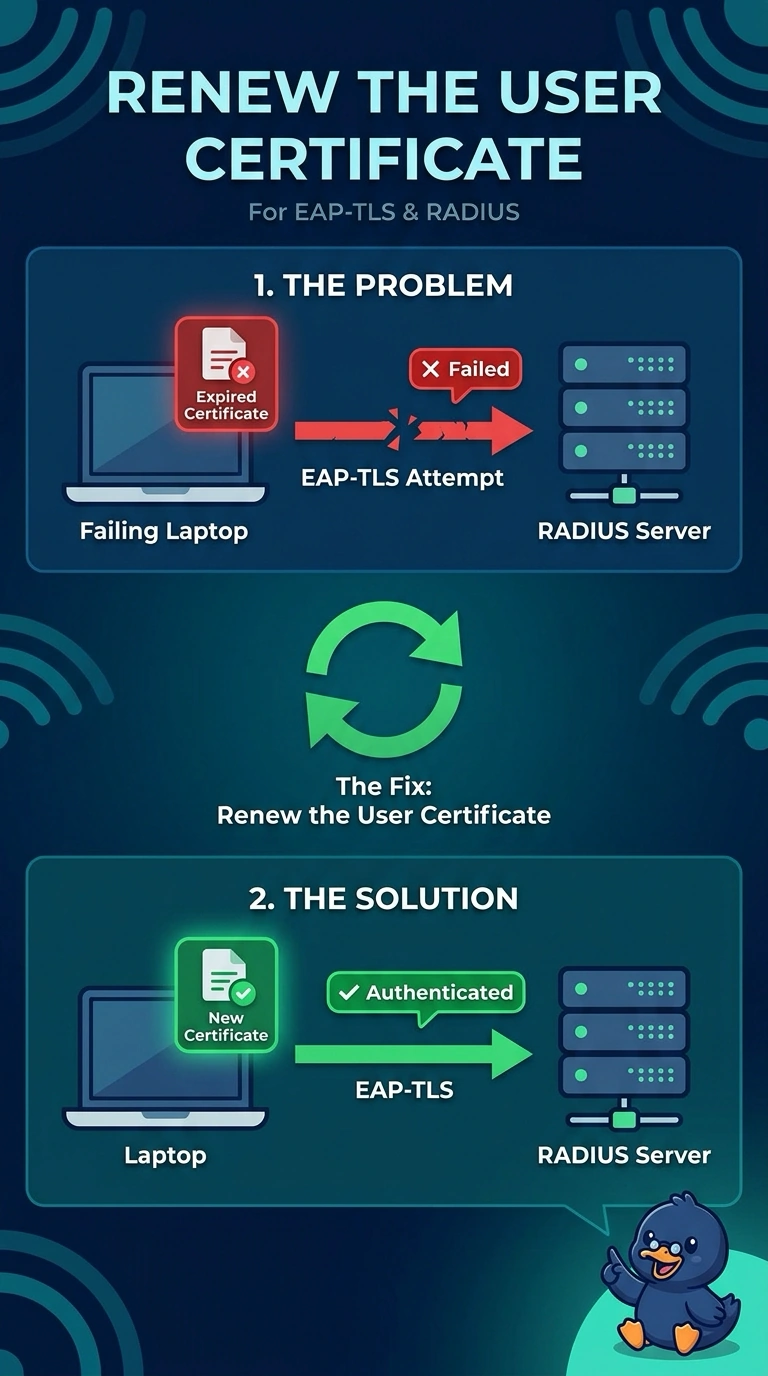
A laptop fails EAP-TLS. Its user certificate expired last week. The RADIUS server certificate is valid, and a laptop with a current user certificate joins. What should be renewed?
Select an answer to reveal the explanation.
Short Explanation
The server's badge is fine, and this laptop is carrying one that ran out last week. Renew your user certificate. Another laptop with a current certificate already proved the server.
Full Explanation
EAP-TLS fails when the certificate the client presents is outside its dates. This user certificate expired last week, and a different laptop with a current user certificate joins, so the RADIUS server certificate is not the one that needs renewal. Renew the expired user certificate. Shortening the beacon does not renew a certificate. A guest passphrase is not a substitute for a user certificate on an EAP-TLS WLAN. The laptop's user certificate expired. The server certificate is fine. Renew the user certificate. Check one live client after the change and leave the rest of the floor alone until that client matches the result you expected. Read the live counters after you retest. Exam caveat: the new certificate still has to come from a CA the server trusts, and it has to sit in the store the supplicant uses. A renewed certificate in the wrong store fails the next attempt. Operational check: install a current user certificate on the failing laptop and confirm EAP-TLS succeeds without changing the server certificate.