
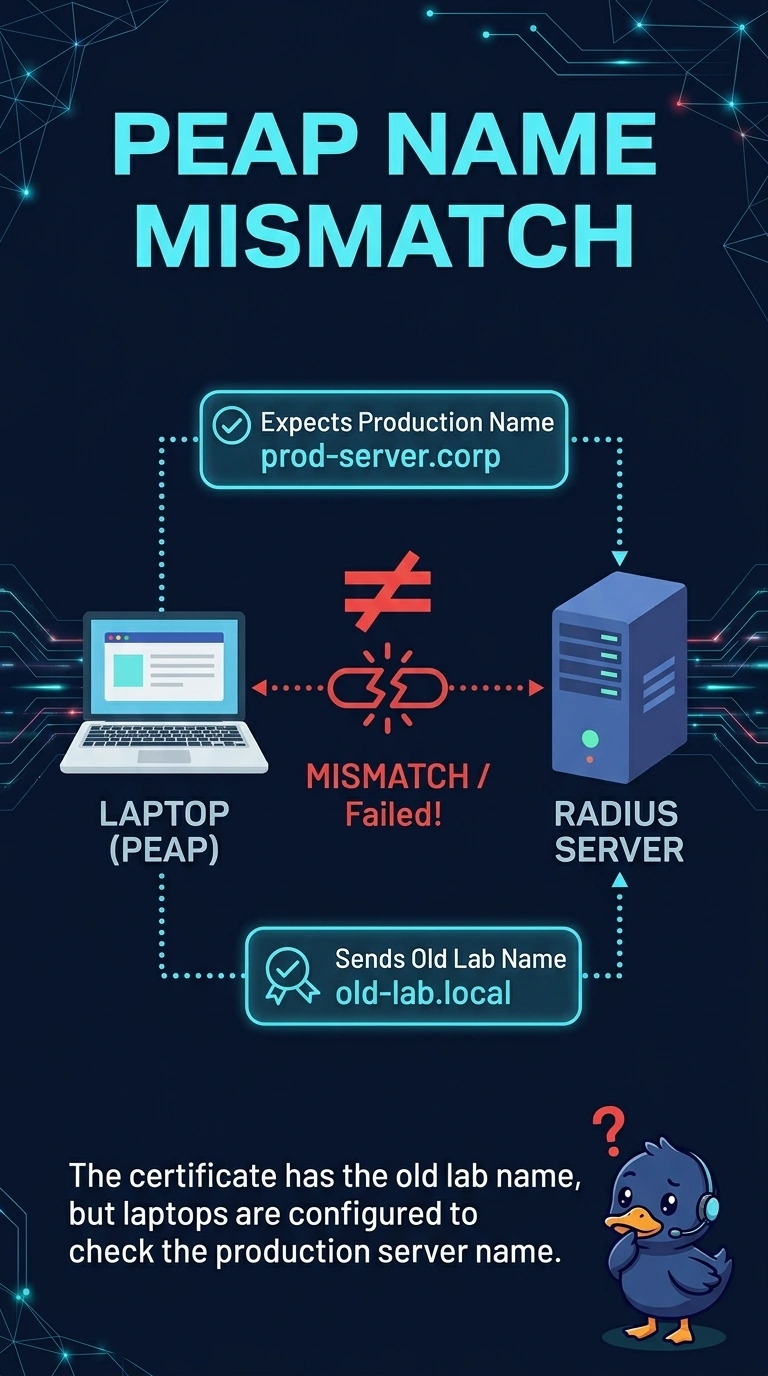
Clinic laptops reject the RADIUS server during PEAP. The certificate is inside its dates and is signed by a CA the laptops trust, and the name on the certificate is the old lab name. The laptops are set to check the production server name. What is wrong?
Select an answer to reveal the explanation.
Short Explanation
The laptops trust the signer and still refuse the server, the way a badge for the wrong building fails a door you are allowed to use. Your laptops are checking for the production name, and the certificate still says the lab. Put the production name on the certificate.
Full Explanation
PEAP clients that validate the server name accept a certificate only when a name they expect appears on it. This certificate is in date and chains to a trusted CA, and it carries the old lab name while the laptops check the production name. They are right to reject it. The dates are not the failure. The stem says the certificate is inside its dates. A client MAC address is not a field the RADIUS certificate needs for PEAP. The beacon interval is an over-the-air timer and has no relationship to the name on a server certificate. The laptops are doing the name check they were configured to do. A trusted signer does not excuse the wrong name. Confirm the result on one live client before changing anything else. Exam caveat: the name can be in the common name or a subject alternative name, and the supplicant may check one specific name. Matching a name the profile does not check will still fail. Operational check: reissue the certificate with the production name the laptops expect, then confirm a test laptop completes PEAP without a name warning.