
A regional hospital is enabling ISE posture for clinicians' laptops before they reach the electronic-records VLAN. Every laptop must show a current antivirus product and full-disk encryption, and ISE must keep its list of acceptable antivirus builds current as vendors release them. Which posture configuration supplies that application data to the compliance checks?
Select an answer to reveal the explanation.
Short Explanation
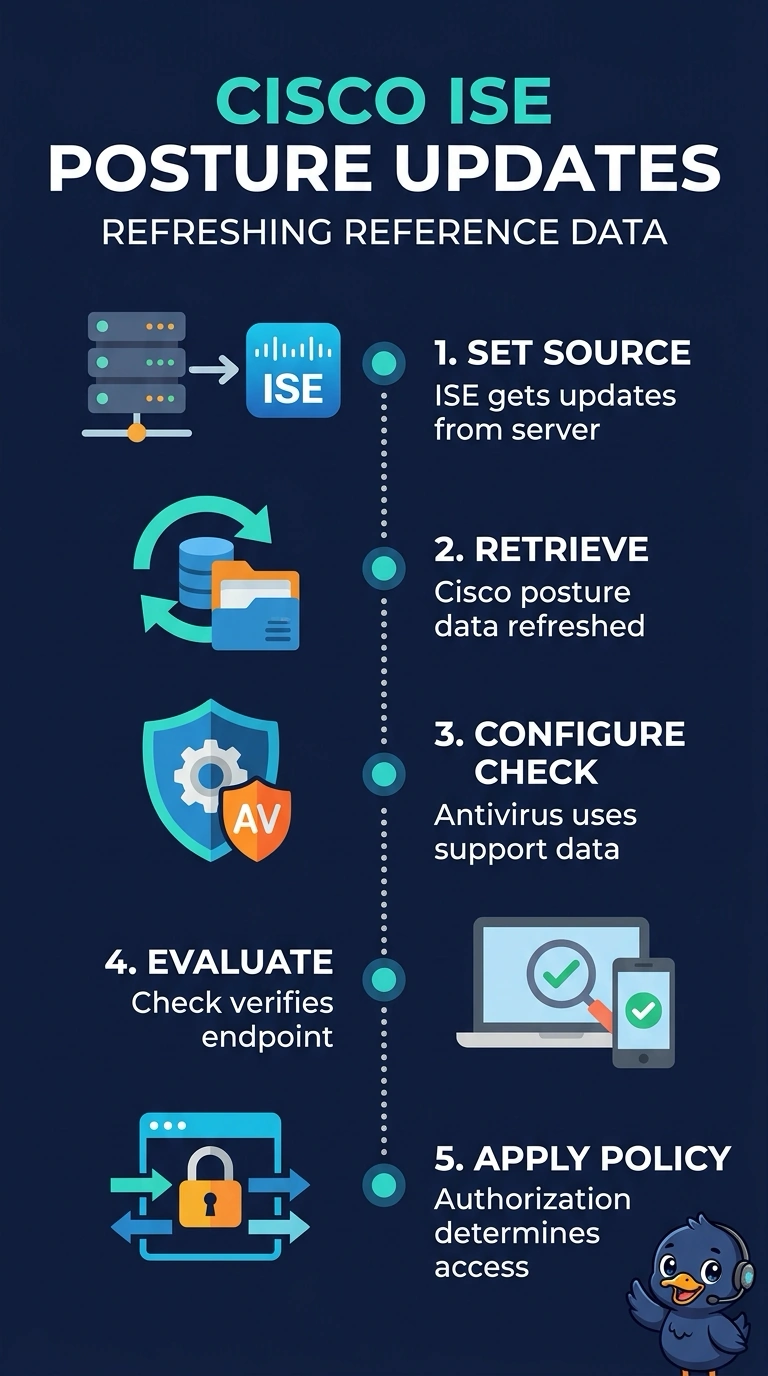
Your compliance checks need current reference data, not just results collected from each laptop. Enable posture updates so ISE refreshes Cisco’s antivirus support data—like keeping a checklist up to date as vendors release new builds.
Full Explanation
ISE posture separates the endpoint checks from the reference data those checks use. Cisco posture updates can refresh antivirus and antispyware support charts and other posture data. Configure the relevant antivirus requirement to use the updated support data, and configure a separate disk-encryption requirement for the encryption check. Updates do not guarantee that every newly released vendor build is immediately included; the support data changes when Cisco publishes an update and ISE retrieves it. An agent profile that reassesses every fifteen minutes changes how often endpoints are checked, not the reference data. A hand-typed list must be maintained separately. Exam caveat: posture updates supply reference data, but a requirement must use that data for it to affect compliance. Practical check: after an update, inspect the antivirus requirement and confirm the supported versions meet your policy.