
A bank's single ISE node at HQ handles administration, monitoring and policy for 1,200 switches. A second appliance at the branch will authenticate 3,000 wireless users with HQ's shared policy, while administration and monitoring remain at HQ. Which persona plan and registration order should the branch node follow?
Select an answer to reveal the explanation.
Short Explanation
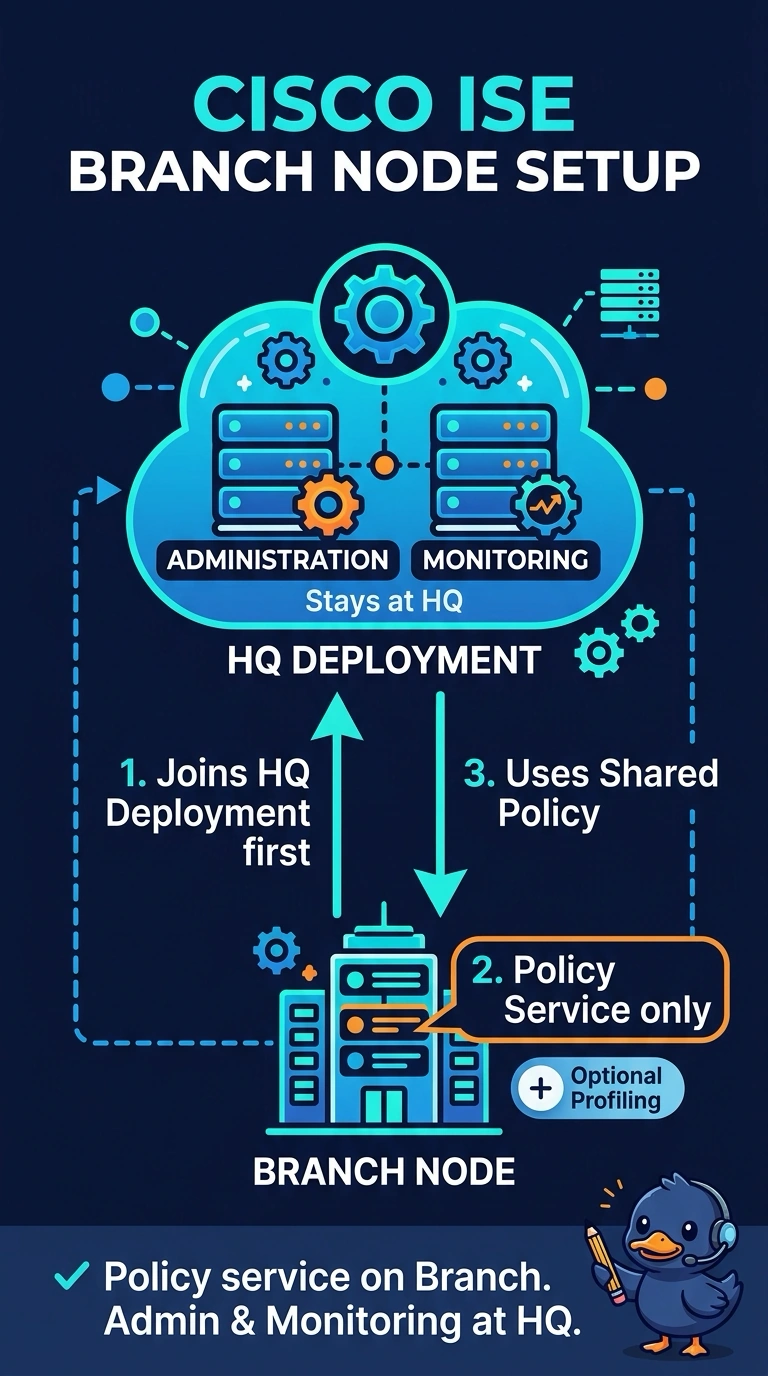
First, you’ll register the branch appliance with HQ’s deployment, then enable only the policy service persona. Think of HQ as the control room for administration and monitoring, while your branch node handles wireless authentication.
Full Explanation
In a distributed ISE deployment, the administration persona manages configuration, and a policy service node uses configuration from the deployment. Register the branch appliance with the existing deployment, then enable its policy service persona; HQ can continue to provide administration and monitoring. Administration and monitoring personas can also be deployed on additional nodes for availability, but that is not needed for the stated plan of keeping those functions at HQ. A separate deployment would have separate configuration rather than automatically sharing HQ policy, and importing exports at each change window would not provide the requested shared deployment. Enabling policy services before registration is not the specified deployment sequence and would not make the branch a registered node using the shared deployment configuration. Node registration and persona changes can affect service availability, so plan them for a maintenance window and verify the deployment status and branch sessions afterward.