
Your company is starting a BYOD program for 400 employee laptops that must join the corporate WLAN with 802.1X EAP-TLS. The security lead wants certificate lifecycle and user enrollment handled inside ISE through a guided browser flow rather than emailed files. Which BYOD component workflow should you design for supplicant and certificate provisioning?
Select an answer to reveal the explanation.
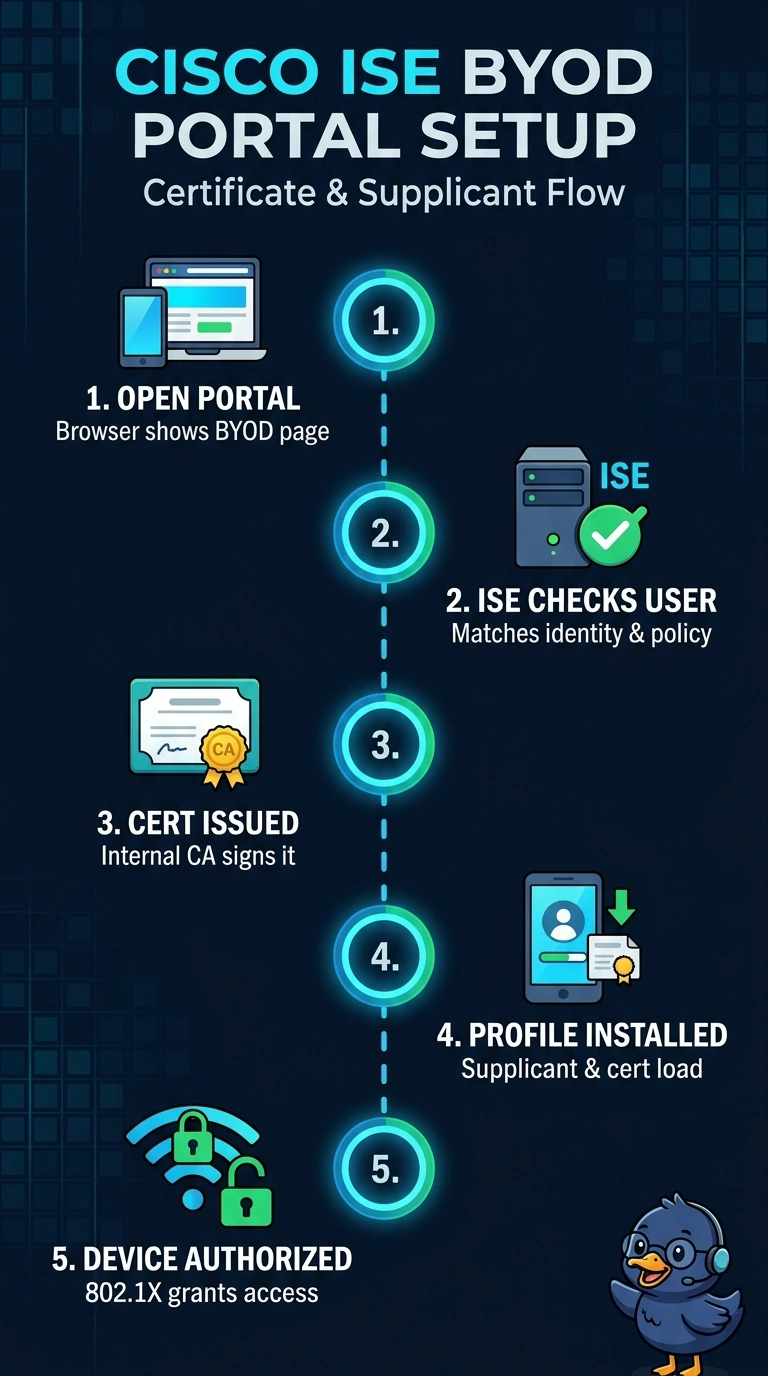
Short Explanation
Your BYOD rollout lives or dies on enrollment, and ISE's internal CA plus the BYOD portal handle it in one guided flow. Users click through a browser page and get both the supplicant and their certificate installed, so nobody ends up emailing credential files around. It works like a self-service badge machine that prints your pass and shows you how to use it, and the internal CA signs the certificate on the spot.
Full Explanation
ISE supports BYOD end to end by acting as its own certificate authority behind a self-service portal. When a user opens the BYOD page, ISE authenticates the person, issues a certificate from the internal CA, and delivers a provisioning profile that installs both the supplicant configuration and the certificate in one guided browser session, so enrollment, renewal and revocation stay in a system you already operate. Handing users a PKCS#12 file exported from an enterprise PKI such as Microsoft AD CS misses the in-ISE lifecycle requirement, because enrollment then happens outside ISE and the user performs a manual import instead of following a guided portal. EAP-FAST is a different EAP method; a PAC does not substitute for the client certificate required for EAP-TLS. MAB with profiling skips supplicant and certificate work altogether and uses the device's MAC address as its identity, which provides no cryptographic identity. Exam caveat: the internal CA is the standard BYOD issuer, while an external PKI is an optional addition rather than a prerequisite. Practical check: run one test device through the BYOD portal and confirm it then authenticates with 802.1X using the newly issued certificate.