
A network operations center is replacing per-device local accounts on its routers and switches with ISE TACACS+. Senior engineers must reach privilege 15 with unrestricted command execution, while helpdesk staff must be limited to a fixed list of read-only show commands on the same devices. The team wants a single device admin policy set to serve both roles. Which device admin design assigns the correct TACACS+ results to both groups?
Select an answer to reveal the explanation.
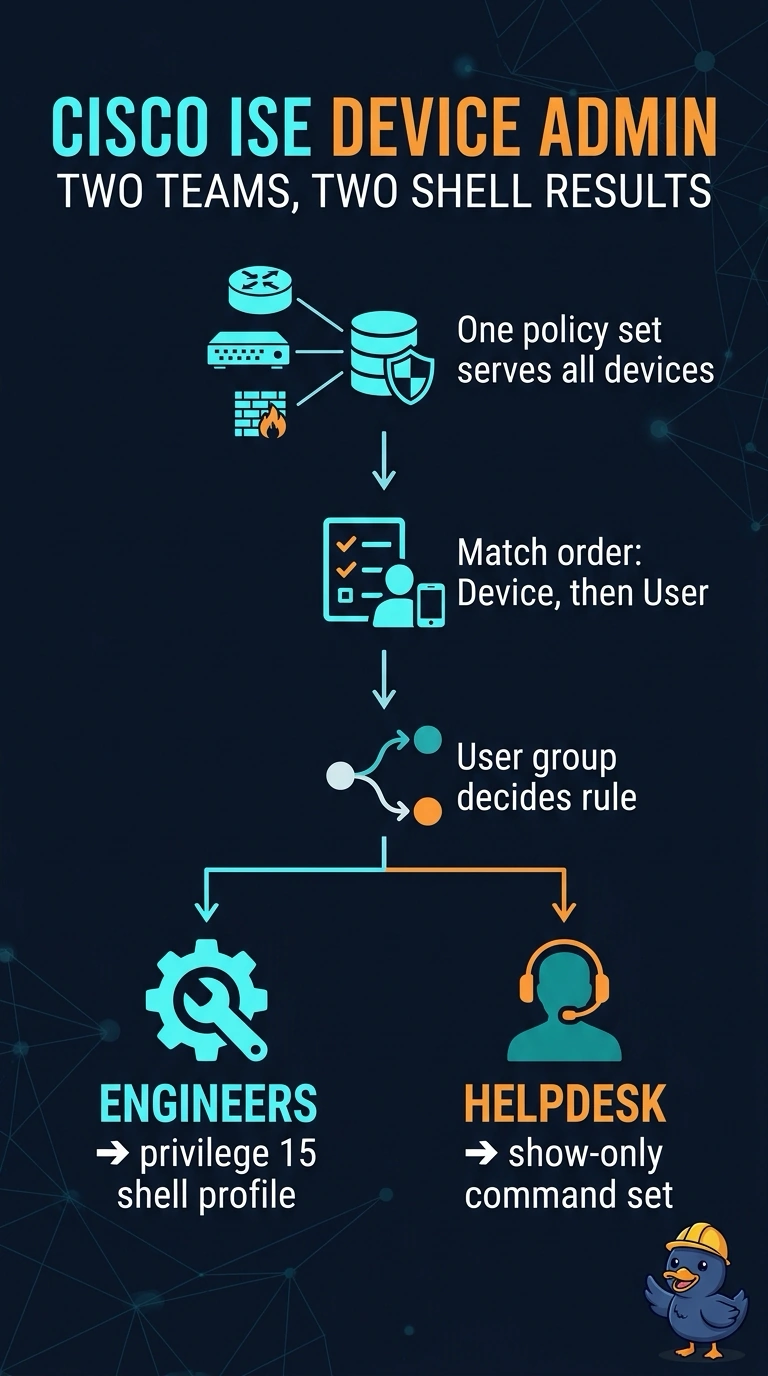
Short Explanation
You can serve both roles from one device admin policy set, with ISE returning a different result for each group. The shell profile gives engineers privilege, while the helpdesk command set lists the read-only show commands they may run—like a keycard paired with a list of rooms you can enter.
Full Explanation
Use one device admin policy set to return role-specific TACACS+ authorization results: engineers receive a privilege-15 shell profile with unrestricted command execution, while helpdesk receives a command set permitting only the specified read-only show commands. This centralizes administration in ISE and applies the required permissions to each group on the same devices. Giving helpdesk privilege-1 access instead relies on IOS privilege levels, which do not reliably express a fixed list of permitted show commands; precise restrictions require command authorization. Giving engineers a broad TACACS+ command allowlist also falls short: an allowlist can omit a valid command and therefore does not provide the unrestricted execution they need. Creating separate device admin policy sets could assign privilege-15 access to engineers and show-only commands to helpdesk, but it violates the requirement to serve both roles with a single set. Exam caveat: privilege level and command authorization are distinct controls, so a privilege-15 shell profile alone does not guarantee unrestricted commands if command authorization restricts them. Practical check: test TACACS+ authorization on a representative device with accounts from both groups, confirming engineers can execute required commands and helpdesk can run only the approved show commands.