
A logistics warehouse runs MAB for 600 handheld scanners and label printers whose access ports carry no supplicant traffic. ISE receives only the device MAC address in the RADIUS request, so every device falls into the Unknown profile and lands in the quarantine VLAN. The scanners obtain addresses from DHCP and broadcast hostname and vendor-class data. Which profiling feed must reach ISE so its rules can use that broadcast evidence?
Select an answer to reveal the explanation.
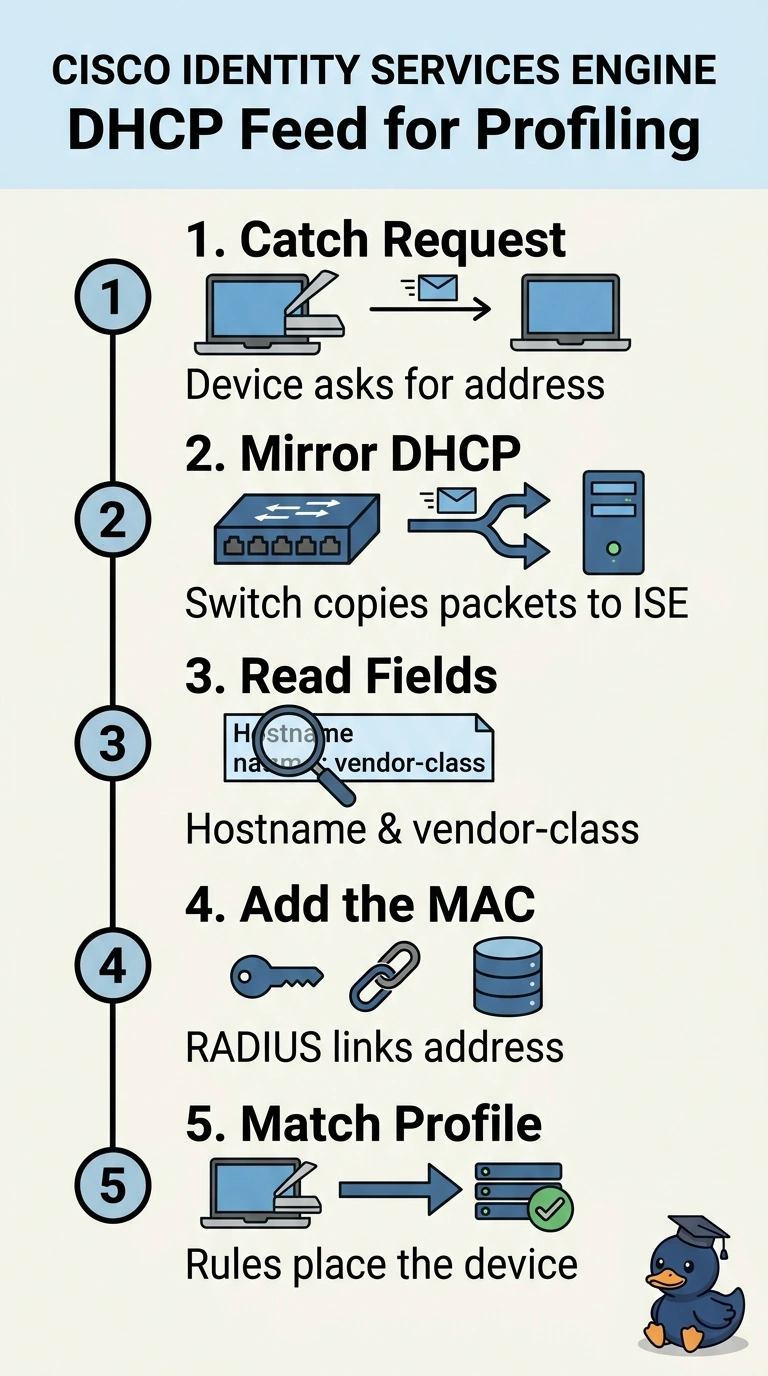
Short Explanation
A MAB request gives ISE the MAC address, but not the DHCP details your profiling rules need. Mirror the access VLAN’s DHCP traffic to the profiler so it can read hostname and vendor-class data—like giving ISE the device’s full name tag, not just its ID.
Full Explanation
Profiling uses evidence from multiple sources, and the MAB request in this scenario provides only a MAC address. Mirroring the access VLAN's DHCP traffic to ISE lets the DHCP probe receive attributes such as hostname and vendor class from the scanners' DHCP messages; profiling rules can use those attributes when matching a device profile. SNMP can provide other endpoint attributes, but it does not carry the DHCP option fields the question asks about. A DNS reverse lookup returns a name associated with an address, not the DHCP options sent by the client. NetFlow describes traffic flows rather than those DHCP options. DHCP is one of several sources the profiler can use. To verify collection, check the profiling statistics after a scanner requests an address.