
A manufacturer is standardizing wired ports across three plant floors. Every port must try 802.1X first and fall back to MAB for printers and scanners, hold unauthenticated devices on a restricted pre-authentication VLAN, and move each authorized session to the corporate VLAN with its scalable group tag. Which IBNS 2.0 policy-map and service-template arrangement meets this design?
Select an answer to reveal the explanation.
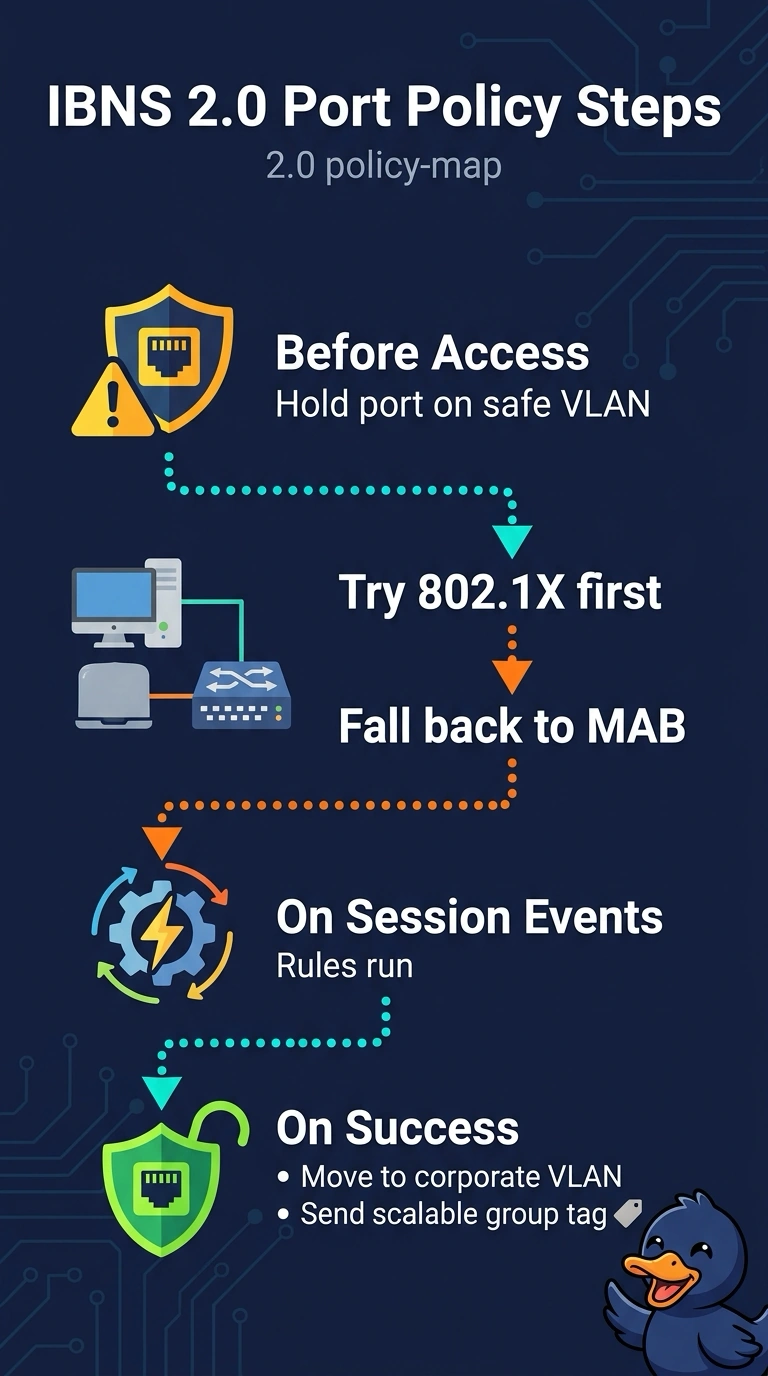
Short Explanation
IBNS 2.0 splits the job between the subscriber class, whose ordered rules pick the method, and the service templates that carry the VLAN and tag. You write that sequence once, and it's the same on every port. Printers still get their MAB fallback while unauthorized ports stay restricted.
Full Explanation
In IBNS 2.0 the policy-map of type control subscriber holds numbered rules inside each class, and those rules react to session events by choosing an authentication method or applying a service template, so the sequence you write moves a port from unauthorized to authorized. Putting 802.1X ahead of MAB gives every port a chance to authenticate with 802.1X first, while printers and scanners that do not respond to 802.1X can reach the MAC authentication bypass fallback. The restricted template keeps devices off the corporate VLAN while the port is unauthorized, and the corporate authorization result applies the VLAN and scalable group tag when authorization succeeds. Enabling MAC authentication bypass only on printer ports leaves scanners without the required fallback. Applying a corporate template only on success does not meet the requirement to restrict unauthorized ports; in the described distractor, those ports remain in the switch default VLAN. An authorization result that only installs an ACL filters traffic but delivers neither the VLAN nor the tag. Caveat: give the restricted template enough access for DHCP and portal traffic, or a waiting device may be unable to get an address or reach the portal. Practical check: plug in a scanner, confirm it sits on the restricted VLAN, then watch the corporate VLAN and tag appear after MAB succeeds.