
A logistics company is starting BYOD, and policy requires every certificate to be issued by ISE itself, with outside certificate authorities out of scope for this budget cycle. Phones must verify the ISE server during EAP-TLS, ISE must validate each issued endpoint certificate, and users must enroll on their own without a help-desk ticket. Which certificate design meets these BYOD requirements?
Select an answer to reveal the explanation.
Short Explanation
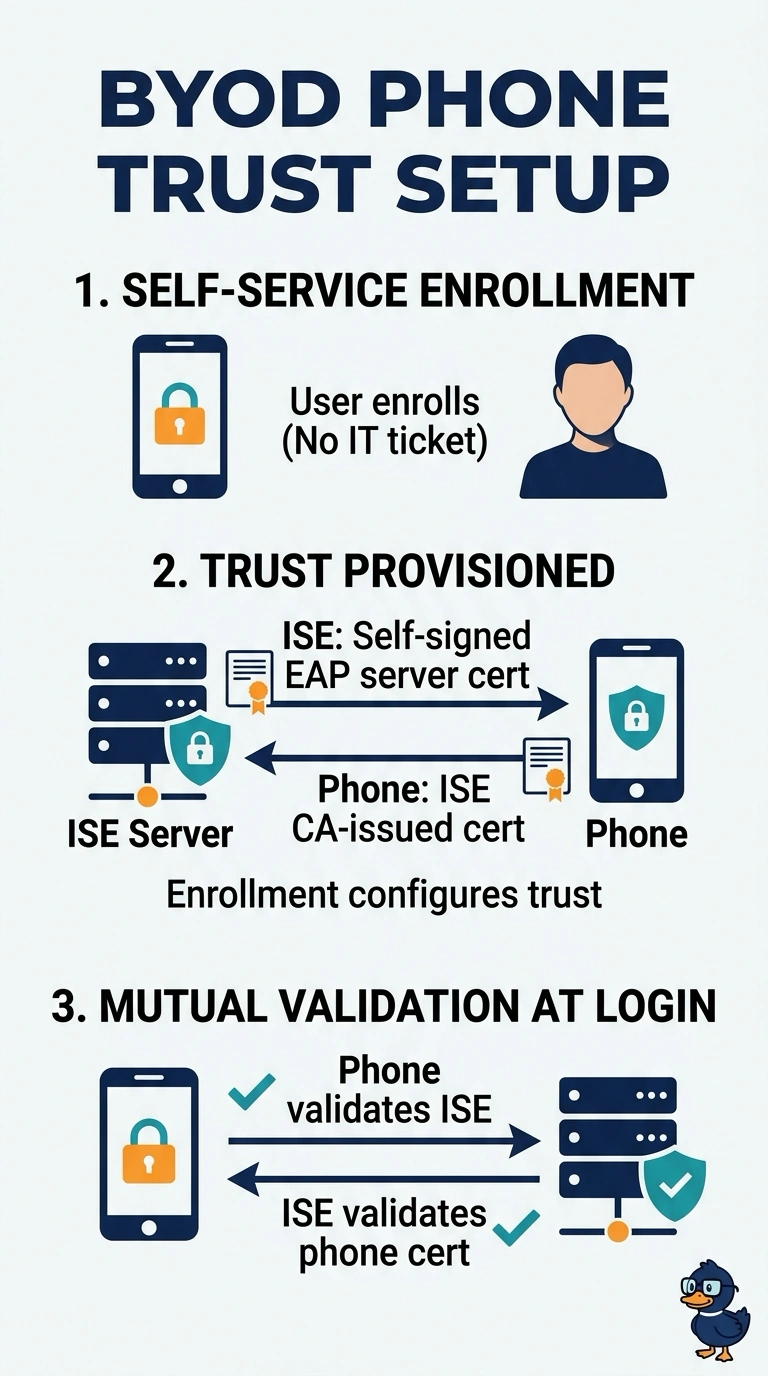
Use ISE’s self-signed certificate for the EAP server and its internal CA to issue phone certificates. During self-service enrollment, your phones can learn to trust the server certificate—like adding a trusted contact—while ISE validates each phone’s certificate.
Full Explanation
The correct design keeps certificate issuance within ISE: ISE's internal CA issues the phone certificates, while the self-signed EAP server certificate lets phones authenticate the ISE server once its trust is provisioned during self-service enrollment. ISE can then validate the endpoint certificates during EAP-TLS, and users can complete enrollment without help-desk tickets or an outside CA. A public CA-signed server certificate is a conventional way to establish server trust, but it brings an outside certificate authority into a cycle that explicitly excludes external CAs; the internal phone certificates and self-service workflow do not cure that conflict. Having help-desk staff install trust and enroll devices is also a common managed-deployment workflow, but it fails the requirement that users enroll on their own. Checking chains and validity dates while omitting revocation checks can accept a certificate that has been revoked, so it does not provide the required complete endpoint-certificate validation. Exam caveat: “self-signed” describes the EAP server certificate, whereas phone certificates can be issued by ISE's internal CA; these roles should not be conflated. Practical check: test enrollment and EAP-TLS on a representative phone, confirming it trusts the ISE server certificate, ISE accepts a valid issued phone certificate, and ISE rejects a revoked one.