
ISE must reuse each person's signed-in Windows session for network access, a new group membership must apply after ISE's directory membership cache expires with no repeat admin work in ISE, and the group list in ISE should contain only the two groups used in policy. Which directory configuration in ISE meets these requirements?
Select an answer to reveal the explanation.
Short Explanation
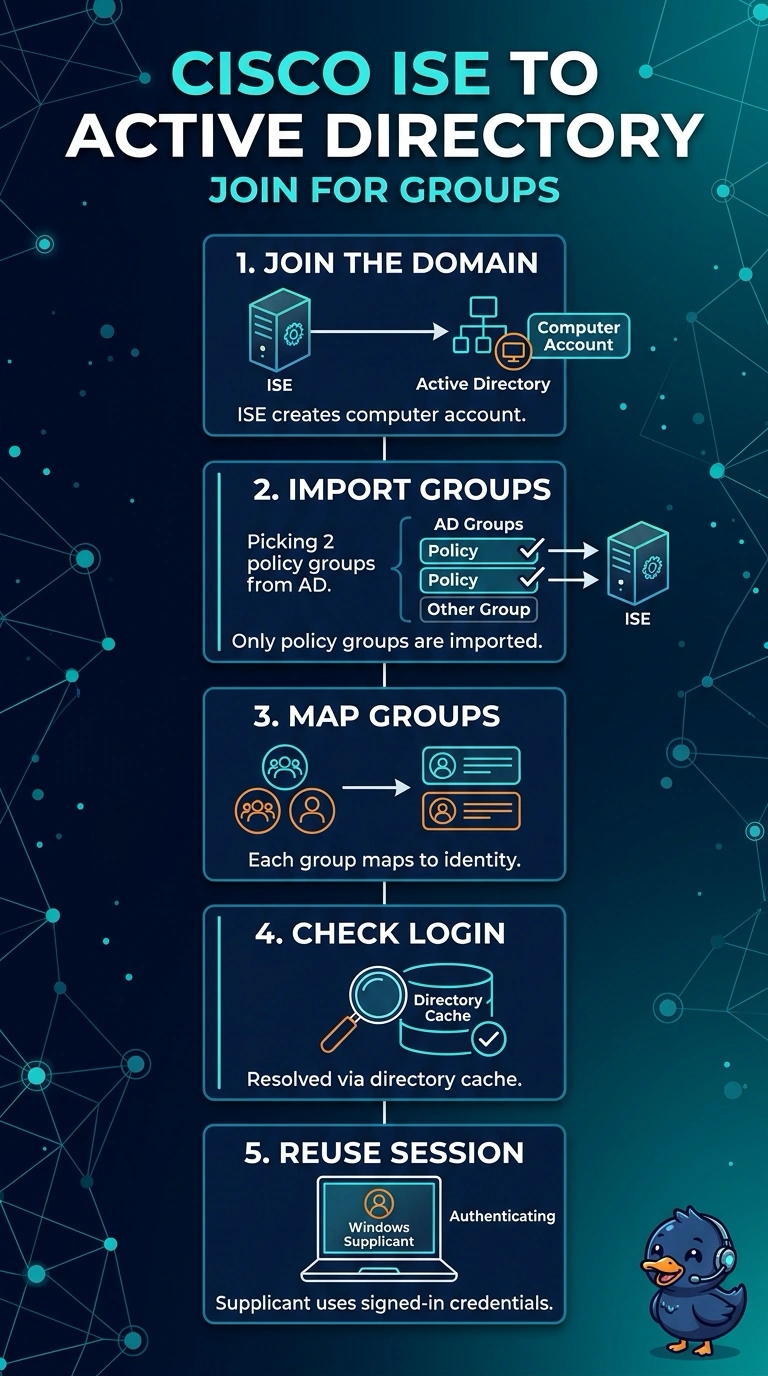
Join ISE to Active Directory, import only the two groups your policy uses, and configure the Windows supplicant to use your signed-in credentials. When someone’s group membership changes, ISE picks it up after its cache expires—like refreshing a list—without extra admin work.
Full Explanation
Joining ISE to Active Directory lets it use the user’s domain identity and retrieve directory group membership. Importing just the two groups referenced by policy keeps the configured group list limited, while Windows supplicant settings that use the signed-in user’s credentials provide session reuse. Once ISE’s membership cache expires, a subsequent authorization can reflect the user’s updated directory membership without an administrator repeating the group import. Prompting users to enter domain credentials at each login is a valid PEAP-style approach, but it does not reuse the credentials from their signed-in Windows session. Retaining authorization in an active session until the user reconnects is also common session behavior; however, cache expiration alone would not make that existing session apply the changed membership, so it misses the requirement that the change take effect after cache expiry. Importing every group from the relevant organizational unit can simplify policy administration, but it adds groups beyond the two used in policy. Exam caveat: group import and membership lookup are distinct; importing a group makes it available for policy configuration, while cache behavior governs when membership changes are seen. Practical check: verify the supplicant’s user-authentication settings, confirm only the intended groups appear in ISE, and test a membership change after cache expiry with a new authorization while reviewing ISE authentication details.