
A regional hospital wants staff to use personal phones and tablets on the corporate Wi-Fi while those devices stay outside mobile device management. Self-registration must be limited to employees who sign in first, and every device must receive its own client certificate for network access. Which BYOD onboarding capability delivers all three requirements at once?
Select an answer to reveal the explanation.
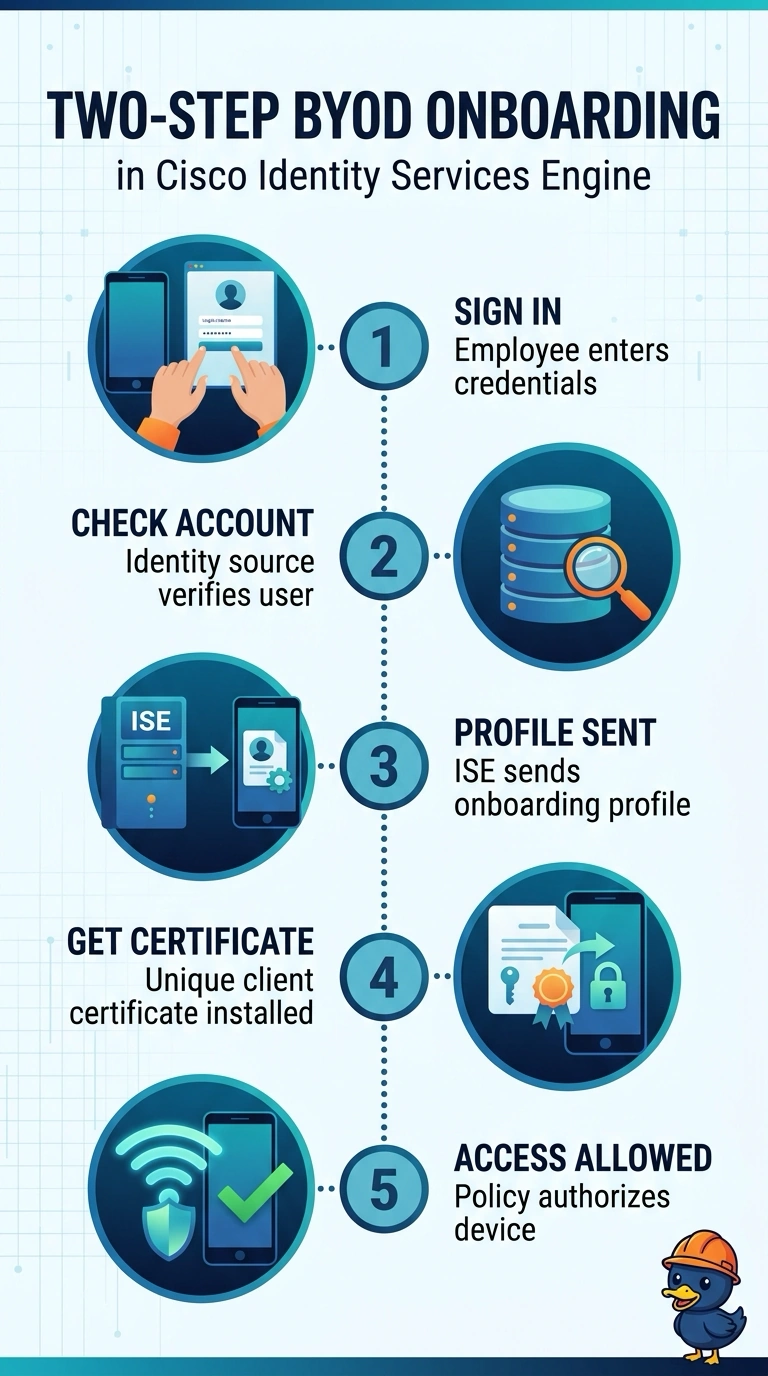
Short Explanation
You want employees to sign in at the BYOD portal before ISE provisions each phone with its own client certificate, so every device can be identified and blocked independently while staying outside MDM. A user-scoped certificate, email-verified registration, or MDM enrollment each misses one of your requirements.
Full Explanation
The capability that meets all three requirements has employees authenticate at the BYOD portal before ISE provisions a distinct client certificate to each enrolled device, without requiring personal devices to enter MDM. A user-scoped certificate installed on registered devices retains employee sign-in and avoids MDM, but the credential is associated with the user rather than being unique to each device, so it fails the per-device certificate requirement. Email-verified self-registration can result in individual certificates and leave devices unmanaged, but email verification is not employee authentication before registration; it does not enforce the requirement that employees sign in first. Having MDM enroll each device before ISE provisions its unique certificate provides employee sign-in and device-specific certificates, but MDM enrollment contradicts the requirement that personal devices remain outside device management. Exam caveat: BYOD portals, certificate authorities, and enrollment protocols can be combined in different ways, so identify which system authenticates the employee and whether the credential is device-specific rather than assuming a protocol name guarantees the requirements. Practical check: verify that policy requires employee authentication before registration, inspect certificate subject or SAN fields and issuance records to confirm a distinct client certificate for each device, and confirm successful enrollment does not trigger MDM enrollment.