
During a ransomware incident, engineers must drop connections to command-and-control servers that Cisco Talos rates as malicious before analysts have catalogued them. Traffic reaches those hosts directly by IP address, the approved access control policy is change-frozen so any fix must sit outside its rule set, and the block must hold even where the matching rule has IPS inspection switched off. Which Threat Defense control should enforce this block?
Select an answer to reveal the explanation.
Short Explanation
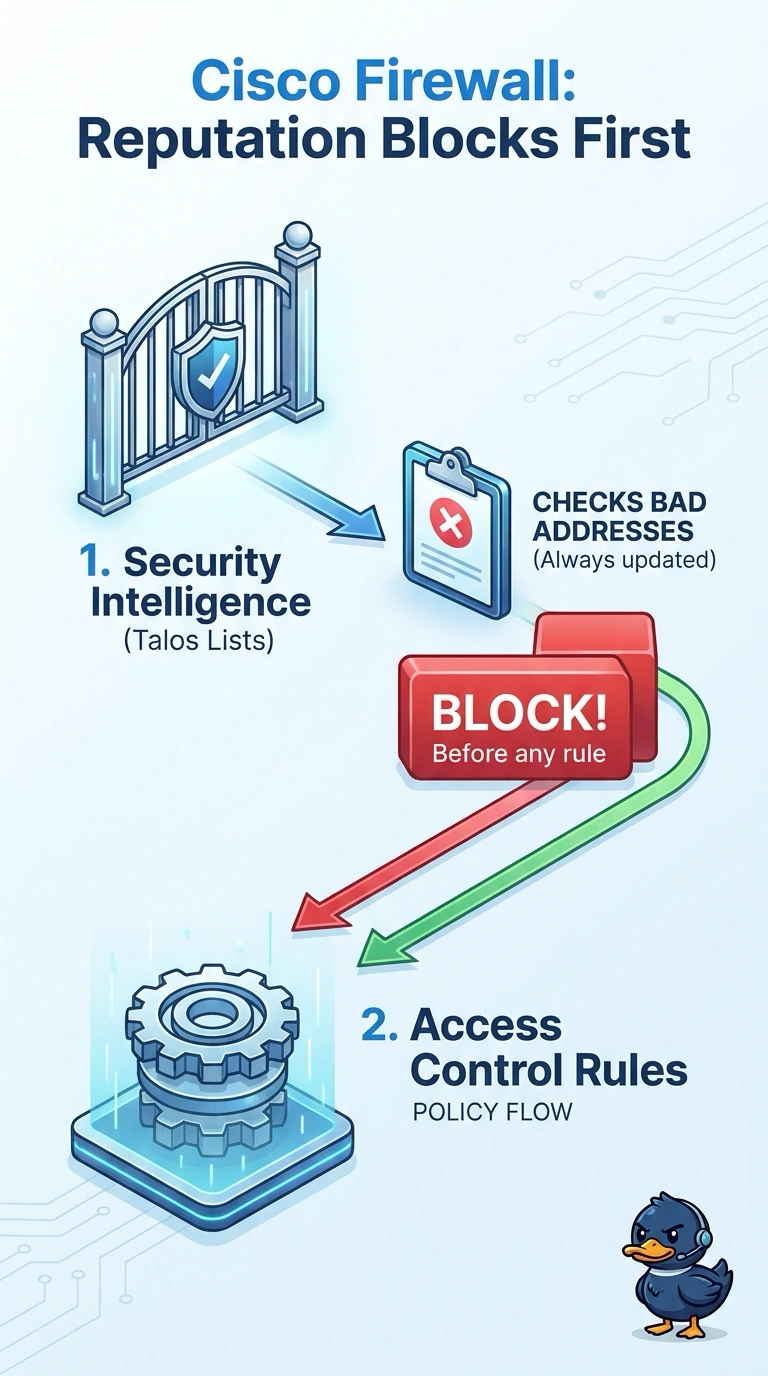
Security Intelligence works like a bouncer holding Cisco's live guest list, checking every connection before the access control rules get a say. That reputation lookup catches raw IP traffic and refreshes itself as Talos updates, so you don't have to catalogue anything first. Your DNS and rule-based options each handle only part of that job.
Full Explanation
Security Intelligence is the fit because its Talos reputation lists can block malicious destinations before analysts add them to local rules, and the control is evaluated before access control rules. It can therefore stop direct-IP connections without changing the frozen rule set, and the block does not depend on IPS inspection being enabled on the matching rule. DNS reputation blocking is a sound defense for malicious hostnames, but it cannot stop a client that connects directly to an IP address without making a DNS query; that misses the stated traffic path. A Talos-fed network group in an access control deny rule can address direct IP traffic and log matches, but it requires an access control rule to reference the group, so it conflicts with the change freeze. Inline IPS signatures can block recognized C2 traffic, but this approach relies on IPS inspection, which the scenario explicitly says may be disabled on the matching rule. Exam caveat: Security Intelligence is configured as part of the access control policy, even though it acts before individual access control rules; “outside the rule set” does not mean outside the policy entirely. Practical check: verify that the relevant Talos Security Intelligence feed and action are enabled, then test a representative destination and confirm the connection event identifies a Security Intelligence block.