
A security operations team adds a STIX TAXII feed of command-and-control infrastructure to the Management Center. They want IP observables blocked on the managed devices, domain observables from the same feed monitored only, and one internal server address that appears in the feed treated as a false positive. Which Threat Intelligence Director configuration delivers those three behaviors?
Select an answer to reveal the explanation.
Short Explanation
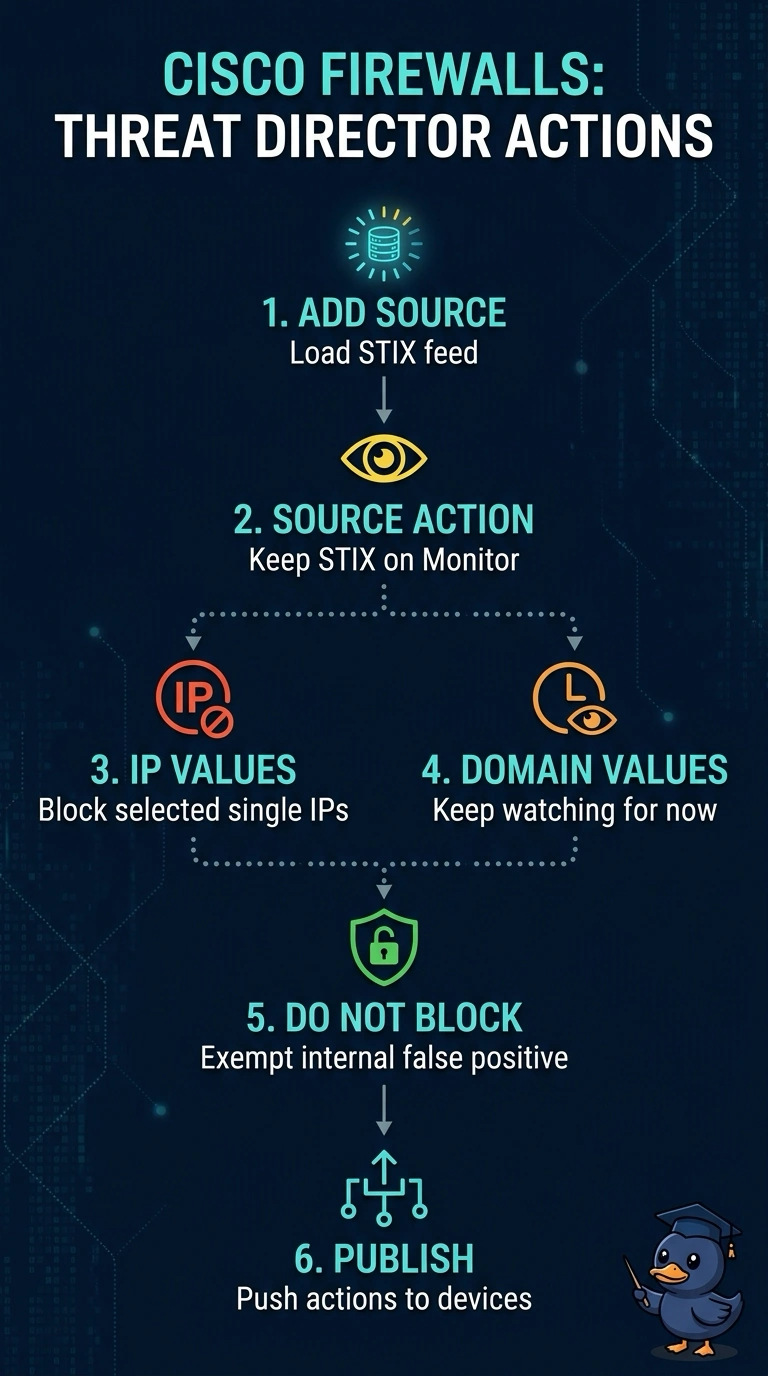
You can steer the action at three levels, and a STIX feed makes you start conservatively at the top. Because complex indicators live in a STIX source, you keep the source at Monitor, then you're free to flip single IP observables to Block and park the false positive on the Do Not Block list. Blocking every observable would deny the domains you only want watched, and skipping the exemption leaves that internal server denied.
Full Explanation
The correct configuration uses the feed in Monitor mode so its observables are not indiscriminately blocked, then applies blocking specifically to the selected IP observables. Domain observables from that same feed therefore remain monitored, and Do Not Block prevents the internal address from being blocked even though it appears in the intelligence. Setting the entire feed to Block is a valid source-level policy when all its indicators should be enforced, but it fails here because domains would also be blocked rather than monitored. Monitoring the feed and blocking the selected C2 IPs otherwise matches the requested policy, but omitting Do Not Block leaves the internal address eligible for blocking; identifying an indicator as internal does not itself create an exception. Monitoring the feed and adding the internal address to Do Not Block handles the false positive and preserves domain monitoring, but fails to block the selected IP observables. Exam caveat: source-level actions and indicator-level overrides are distinct, and a source-wide Block setting can affect more than the indicator type you intend to enforce. Practical check: after deployment, inspect the effective disposition of a representative C2 IP, a domain, and the internal address in the Management Center, then verify the resulting policy on the managed devices.