
A 400-seat manufacturer wants access rules that allow only Finance Active Directory group members onto the ERP servers. Staff already authenticate to the wired network with 802.1X through Cisco ISE, laptops must stay free of agents, and the policy rules out any user sign-in prompt. Which identity source design supplies both the Finance group list and the user-to-IP mappings?
Select an answer to reveal the explanation.
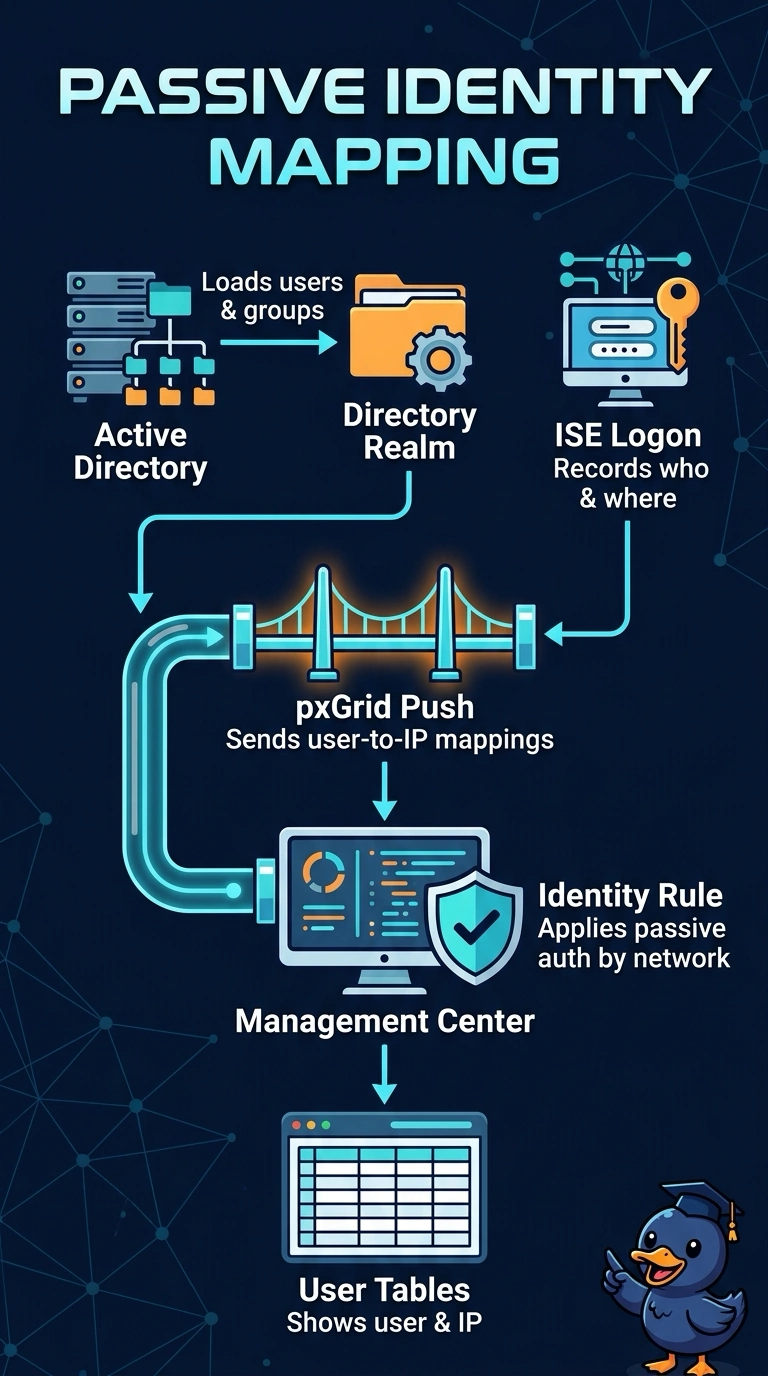
Short Explanation
You can reuse the identity infrastructure already in place: an Active Directory realm supplies Finance group membership, and ISE sends current user-to-IP mappings over pxGrid. Secure Client identity reporting would require an agent, a local Finance list can drift from AD, and DHCP-snooping bindings identify devices and addresses—not the users behind them.
Full Explanation
The design that meets the requirements uses an Active Directory realm to retrieve Finance group membership and ISE over pxGrid to provide current user-to-IP mappings. Because staff already authenticate through 802.1X to ISE, you can reuse an existing identity source without installing endpoint software or prompting users to sign in again. Secure Client identity reporting could provide user-to-IP data, but it conflicts with the requirement that laptops remain agent-free. Using pxGrid for mappings while keeping Finance membership in a local Management Center list disconnects access decisions from the authoritative AD group; the list can become outdated as staff join or leave Finance, leading to incorrect grants or denials. DHCP-snooping bindings provide device-to-address information, but do not establish which user is using an address, so combining them with AD group membership still fails to provide the needed user-to-IP mapping. Exam caveat: group membership and user-IP mappings may come from different integrations, so confirm both are configured and that group resolution uses the intended directory. Practical check: in Management Center, verify that a test Finance user appears in the resolved AD group and that ISE’s pxGrid mapping shows the user’s current IP before testing the ERP access rule.