
A SOC analyst is following a workstation that triggered a Command and Control alert in the Secure Firewall Management Center. The same workstation also produced a malware detection on Secure Endpoint and repeated suspicious lookups through Umbrella within the same hour, but each console shows only its own piece. Which Cisco capability should bring these three detections into one investigation?
Select an answer to reveal the explanation.
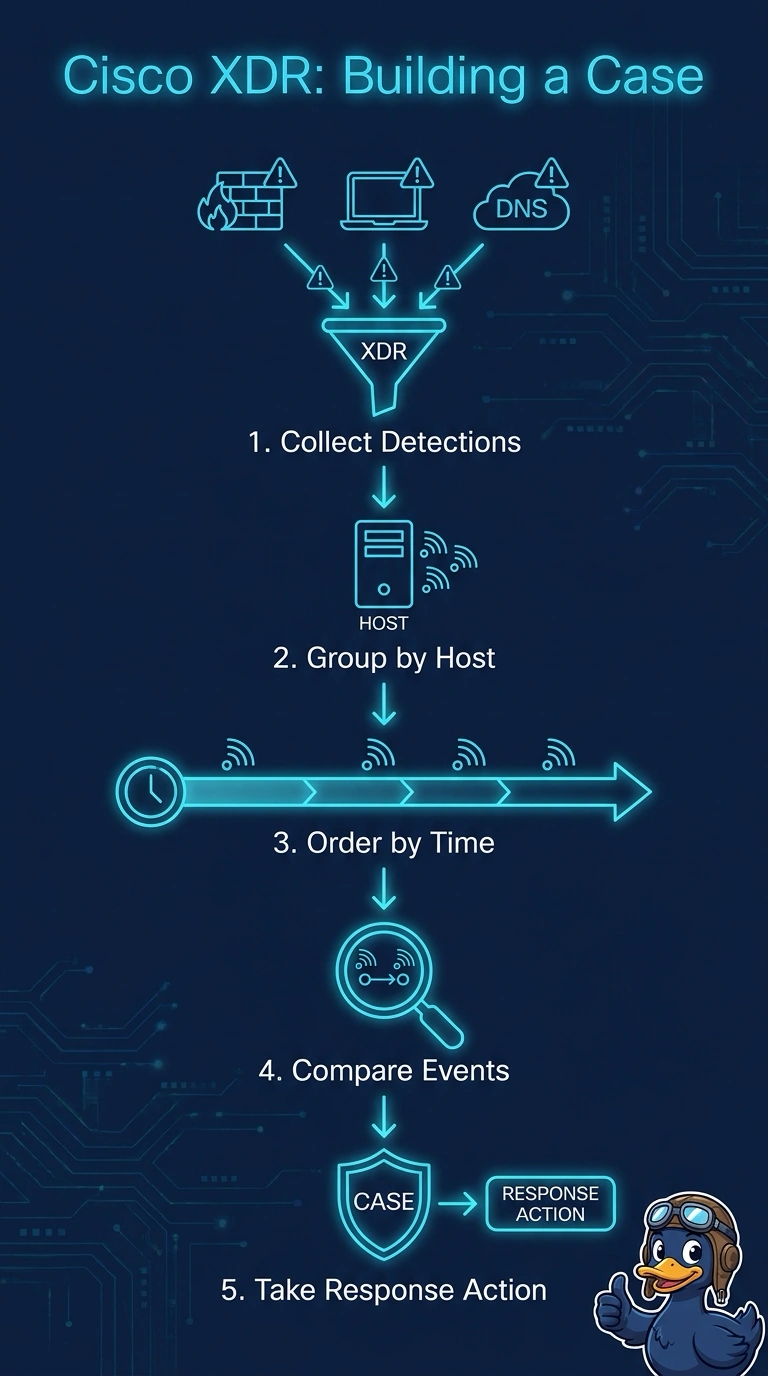
Short Explanation
With Cisco XDR, you can correlate the firewall, endpoint, and DNS detections into one incident timeline. It’s like gathering scattered puzzle pieces in one place, so you can investigate the whole story without switching between consoles.
Full Explanation
Cisco XDR is the appropriate capability because the requirement is to investigate detections from Secure Firewall Management Center, Secure Endpoint, and Umbrella together, rather than merely enrich one alert or correlate events within a single console. Its cross-source correlation can assemble those connected detections into a unified incident timeline, giving the analyst a common investigation view of the workstation’s activity. FMC correlation policies are a valid way to group related events that the Management Center itself receives, but that event-level correlation does not pull in Umbrella DNS lookups, so it falls short of the stated three-source scope. Secure Malware Analytics can enrich an endpoint alert with sandbox detonation results and behavioral indicators, but enrichment is not the same as adding the firewall C2 detection to the same incident investigation. Umbrella Investigate can provide valuable context for suspicious DNS activity and related firewall indicators, yet it does not bring the Secure Endpoint malware detection into the case. Exam caveat: threat-intelligence enrichment, event correlation, and unified incident management are related but distinct capabilities; a useful pivot does not by itself establish that alerts are joined in one timeline. Practical check: verify that the relevant Secure Firewall, Secure Endpoint, and Umbrella integrations are enabled and that the workstation’s identifiers and event timestamps align in the resulting XDR incident.