
A financial services SOC subscribes to a TAXII feed from its intelligence vendor and wants malicious infrastructure blocked on Secure Firewall Threat Defense within minutes of each feed update, with no access or intrusion policy edits after refreshes. Last quarter several IPS rules drifted out of date. Which Threat Defense configuration enforces blocked observables from the feed automatically?
Select an answer to reveal the explanation.
Short Explanation
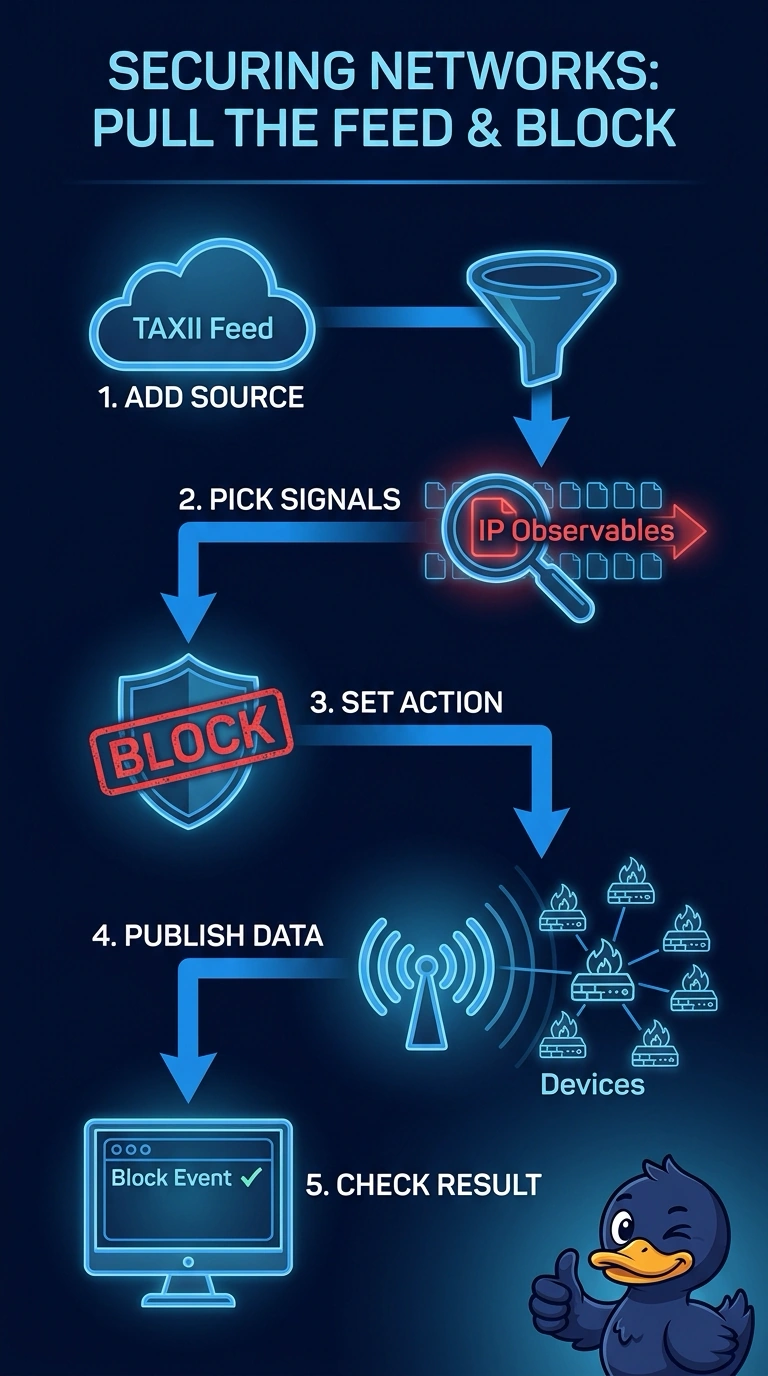
Configure Threat Intelligence Director to fetch your TAXII feed and set supported IP observables to block, so managed devices enforce updates without policy edits. It works like a doorman checking each arrival against the latest list, though you’ll want to confirm feed and device update intervals meet your timing needs.
Full Explanation
Threat Intelligence Director can retrieve third-party threat intelligence from a TAXII source and distribute supported indicators to managed devices. Configure the action for the IP observables to block; feed retrieval and distribution intervals determine how quickly new indicators become available for enforcement. This avoids editing access or intrusion policies after each refresh. Turning the feed into intrusion rules requires translating the indicators into rules and redeploying the intrusion policy, recreating the drift problem. System-provided security intelligence lists use Cisco-provided intelligence rather than the vendor's feed, so they do not enforce indicators from that feed. A dynamic indicator list refreshed nightly and matched in an access control rule is a plausible alternative, but its nightly refresh does not meet the stated within-minutes goal. Confirm that the source retrieves successfully and that a connection event shows the expected indicator and block action.