
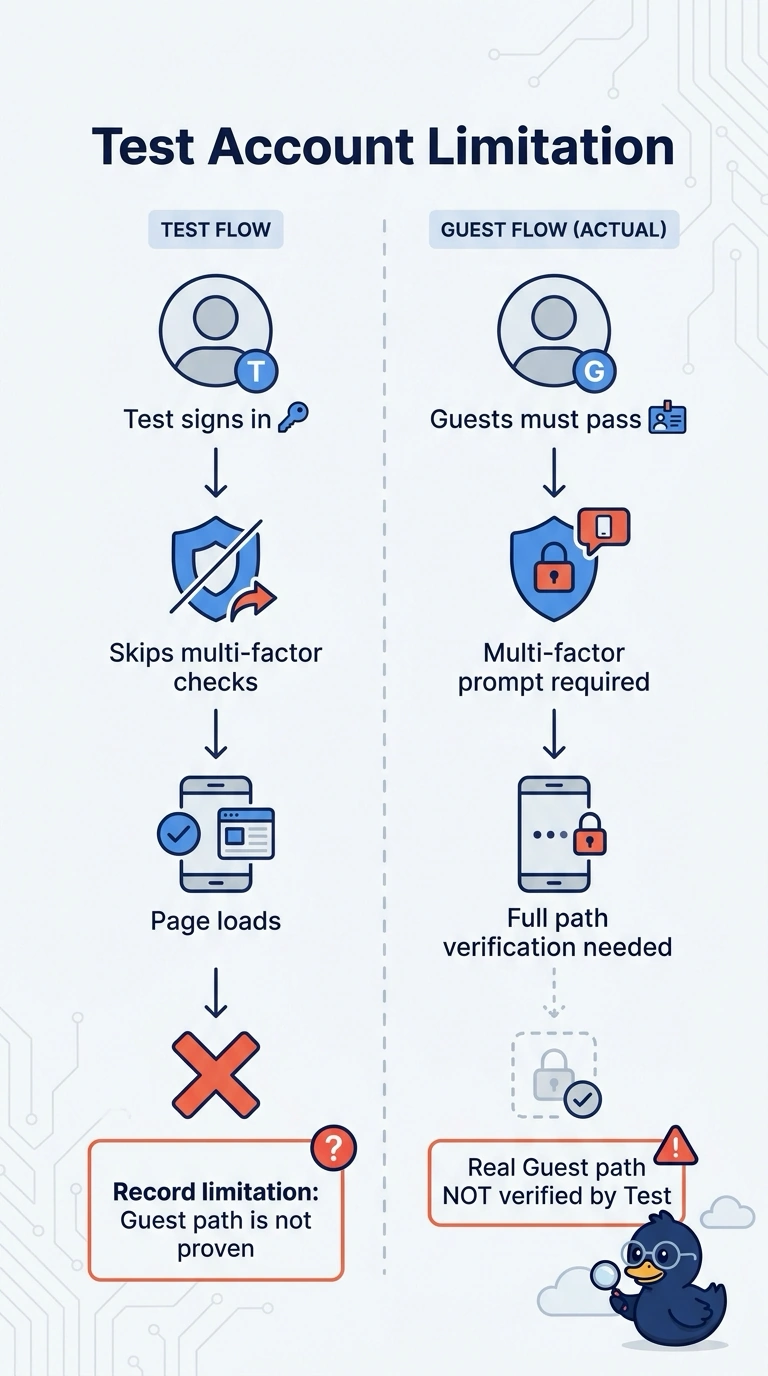
On event days a stadium web test signs in with an account that skips the multi-factor prompt real guests must pass, then the rest of the page loads. What limitation should the team record?
Select an answer to reveal the explanation.
Short Explanation
A backstage pass that waves you past the security line does not prove the line works for everyone else. The stadium test account skips the multi-factor prompt real guests must pass, so the test is not proving that path. The trap is calling it the wrong auth method, a test with no credentials, or a network-loss check.
Full Explanation
The web test reaches the page because its account is allowed to skip the multi-factor prompt that real guests must pass. The result can speak for the steps that account actually walks, and it cannot prove the multi-factor path. That limitation is what the team should record. Saying the ticket application is being tested with a different authentication method than real guests use overstates the gap: the application method is unchanged, and a privileged account is exempted from one step. Saying the page test stores no credentials, so login is not attempted at all, contradicts the fact that the test signs in. Saying the check is only a network-loss test, so it does not log a guest in, contradicts the fact that a page load follows a sign-in. Exam caveat: a green transaction that uses an exempt account is not evidence that every guest can pass multi-factor checks. Operational check: compare the prompts the test account sees with the prompts a normal guest account sees, and note in the test record that multi-factor enforcement is outside what this account proves.