
A zone-based policy permits staff web to the internet and intrusion prevention is not applied to that policy. Malware in those sessions is allowed. Routes exist. What is missing?
Select an answer to reveal the explanation.
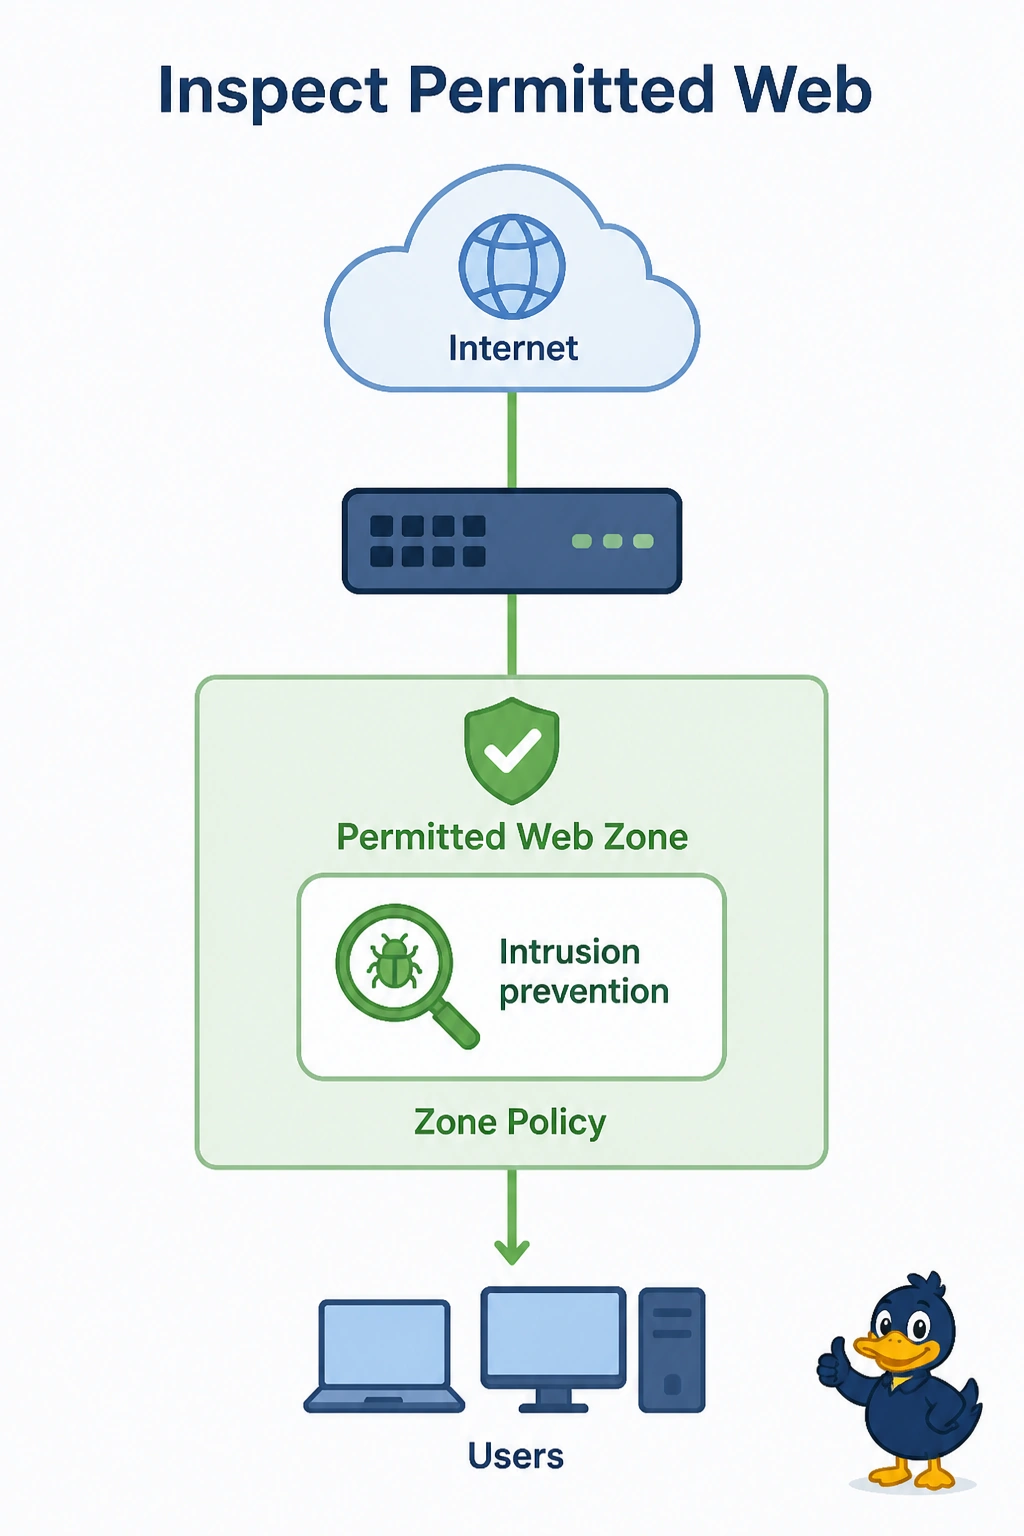
Short Explanation
The door is open and nobody is watching what walks through. You add intrusion prevention to the zone policy that already permits staff web. A routing preference does not inspect the payload, and a loss class is not a malware check.
Full Explanation
A zone-based permit decides that the session may pass. Intrusion prevention, attached to that security policy, is what inspects the permitted traffic for malware. It is not applied here, so malware in staff web is allowed even though the routes are fine. Add intrusion prevention to the policy. An OMP preference only changes which path a prefix uses. It does not look inside a flow that is already permitted. A strict SLA drops or forwards based on loss, latency, or jitter. It is not a malware detector, and healthy loss would not be a reason to drop the session. VPN 512 is the management VPN. Putting staff hosts there does not attach inspection. Exam caveat: inspection has to be on the policy the traffic actually hits. A second unused policy with intrusion prevention does not see these sessions. Operational check: a test payload the intrusion policy is built to catch should increment the inspection counter and be dropped after the feature is applied.