
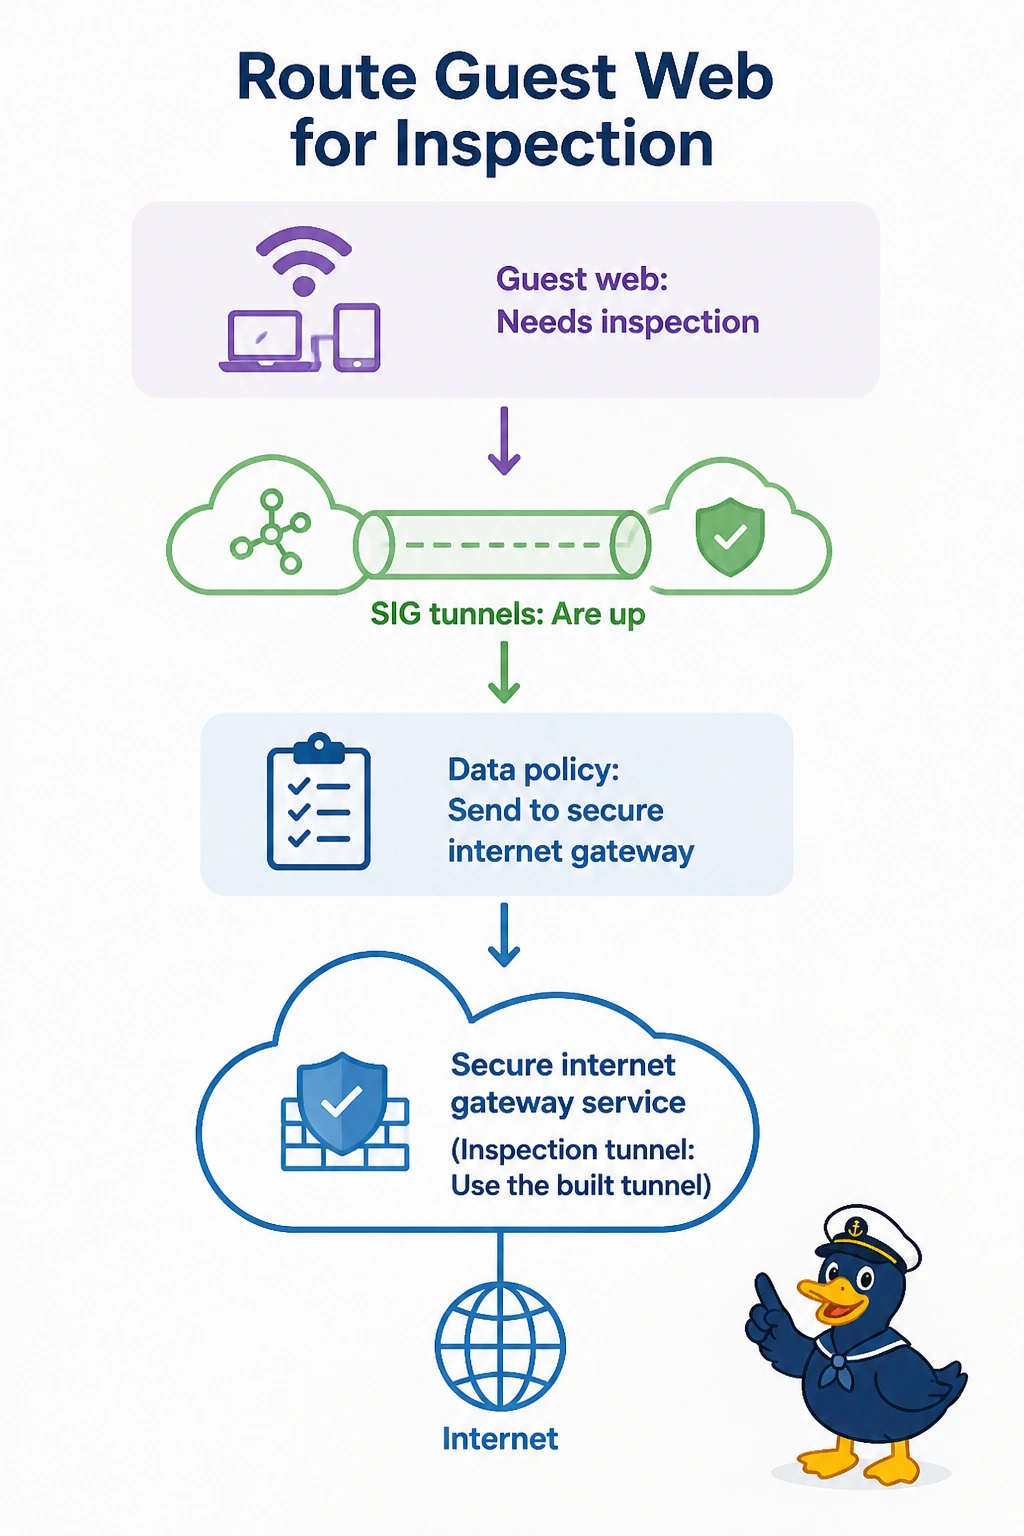
Guest web at a stadium should be inspected by the secure internet gateway. The SIG tunnels are up. A data policy sends guest web to the IaaS cloud gateway that holds a private VPC. What should the policy send it to?
Select an answer to reveal the explanation.
Short Explanation
The inspection tunnel is up, and you sent the guests to a different building. You point guest web at the secure internet gateway service. The IaaS gateway reaches a private VPC and does not run the inspection stack, and VPN 512 will not sort this traffic.
Full Explanation
The Secure Internet Gateway feature builds the tunnels to the cloud security provider. A data policy has to steer guest web into that service or the packets never enter those tunnels. This policy sends them to the IaaS cloud gateway instead, so they head for the private VPC and skip inspection. Change the action to the SIG service. The IaaS gateway is the path into the VPC, not the inspection point. VPN 512 is management and does not apply a security stack to guest sessions. The manager connection carries control traffic. It does not redirect web before OMP. Exam caveat: the SIG tunnels being up is not enough. After you retarget the policy, confirm no earlier sequence still matches guest web and sends it to the cloud gateway. Operational check: a guest session should appear in the SIG log and should not be forwarded toward the VPC prefix.