
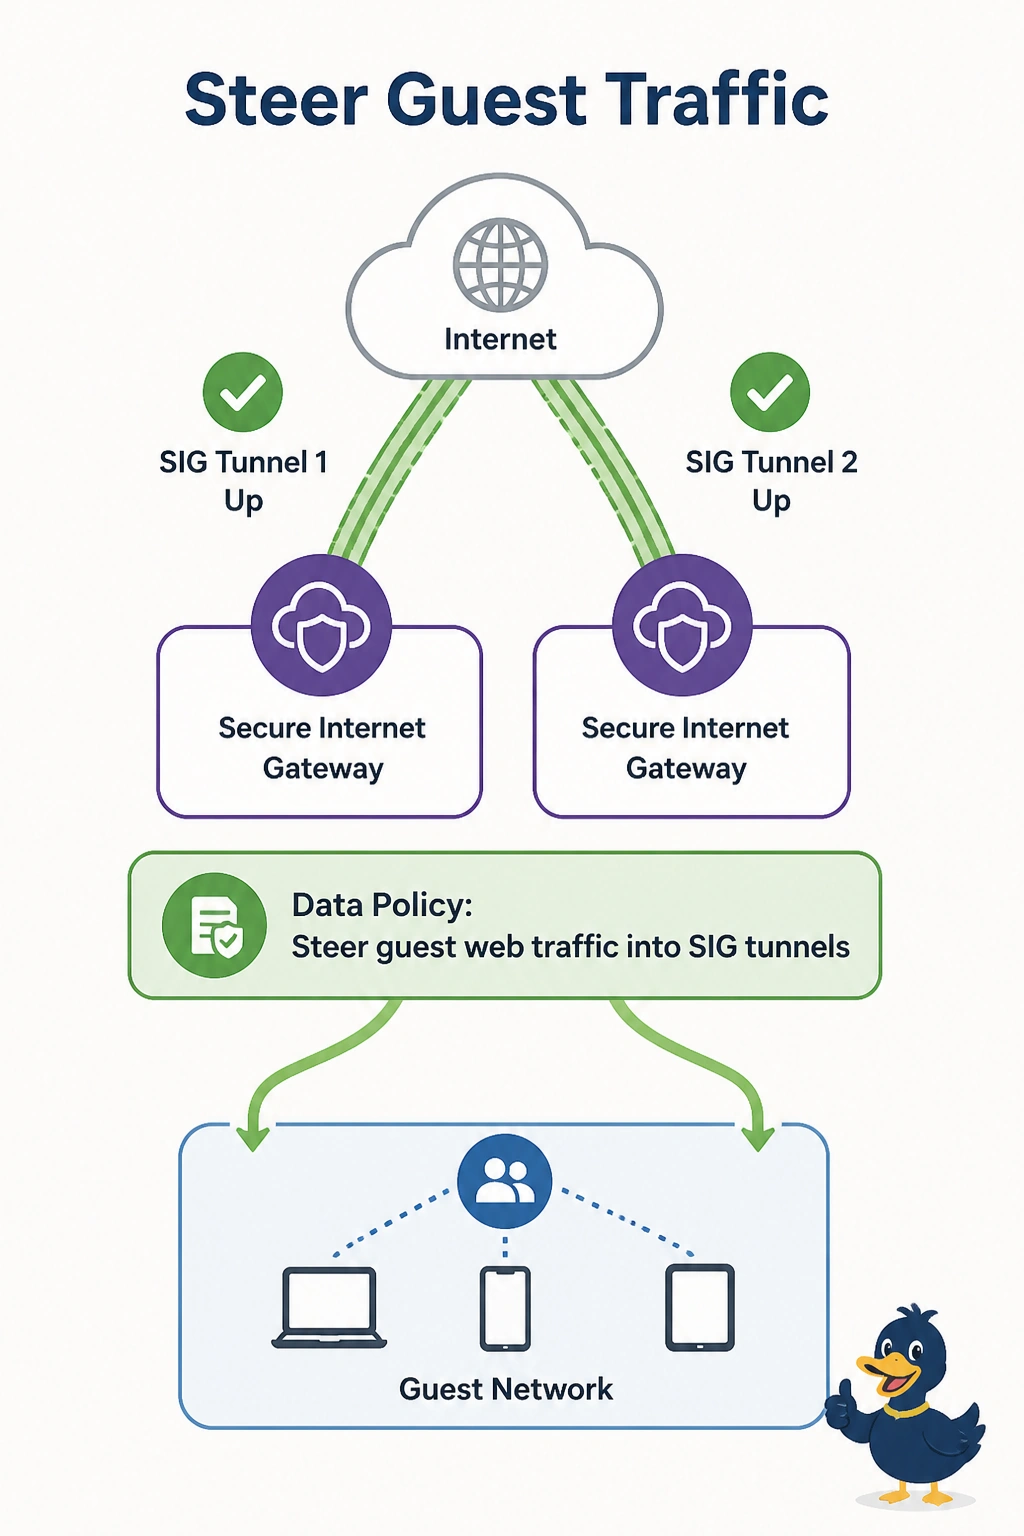
A resort's Catalyst SD-WAN edge shows both secure internet gateway tunnels up. Guest web traffic still leaves by uninspected local internet. No data policy references the SIG. What is missing?
Select an answer to reveal the explanation.
Short Explanation
The inspection lanes are open, and nobody put the guest traffic in them. You add a data policy that steers guest web into the SIG tunnels. The tunnels being up is not the same thing as using them, and you do not need a private VPC gateway to start.
Full Explanation
The Secure Internet Gateway feature can bring tunnels up and still forward nothing until a data policy matches the intended traffic and sets the SIG as its path. Guest web is leaving by local internet because no policy references the SIG. Add that steer. A private-VPC cloud gateway is Cloud OnRamp for Multicloud. It is not a prerequisite for using SIG tunnels that are already up. An OMP filter that withdraws the local internet TLOC can break the underlay the SIG tunnels ride on, and it does not by itself move guest flows into those tunnels. Guest routes in a service VPN are not installed by a BGP session to the SIG provider. The SIG path is a tunnel plus a steer, not a BGP neighbor in VPN 10. Exam caveat: steer only the guest VPN. Staff traffic that is supposed to stay on a different exit should not match the same policy. Operational check: after the data policy is activated, a guest web session should show the SIG path and should appear in the provider log instead of the uninspected local exit.