
A pharmacy chain wants Microsoft 365 to use the local internet exit at each store, and wants every other web flow to stay on the secure internet gateway. Which policy makes that split?
Select an answer to reveal the explanation.
Short Explanation
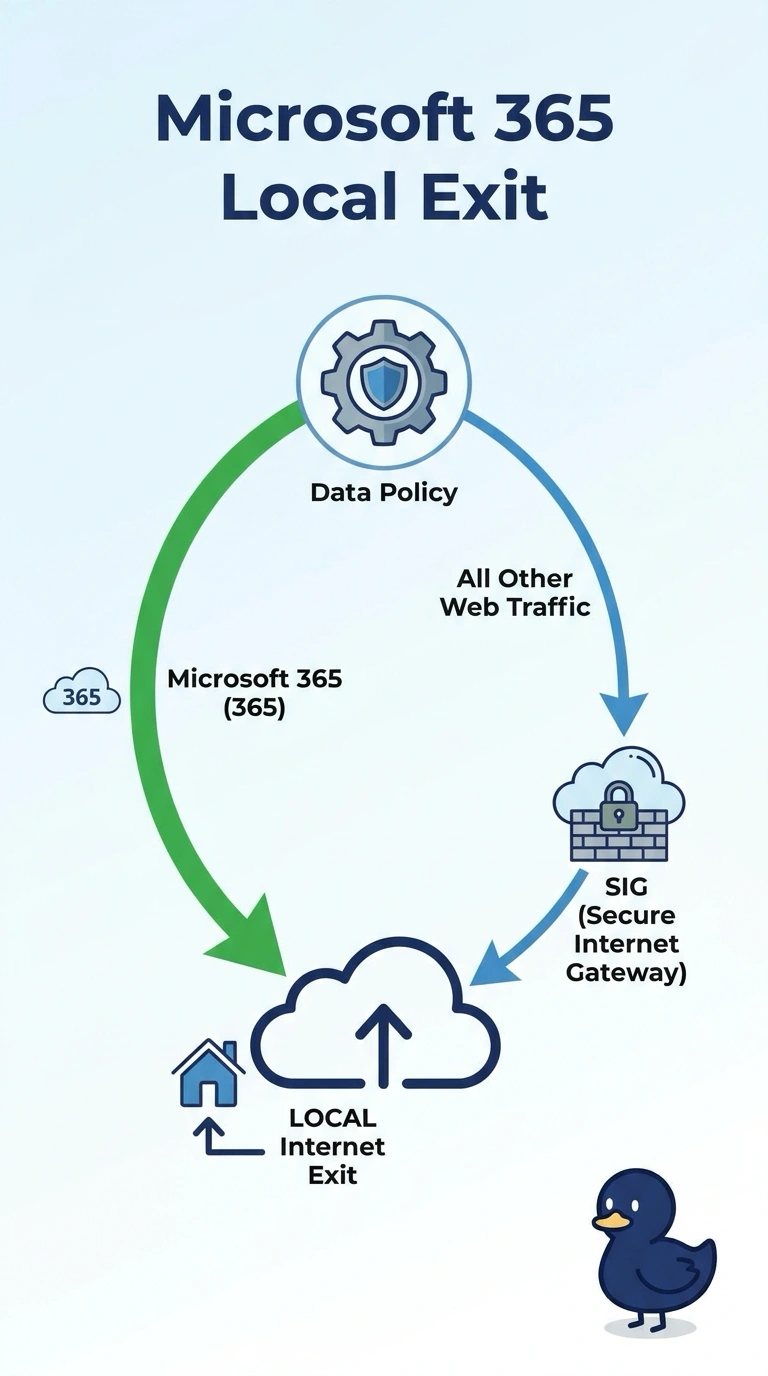
You let one delivery use the side door and you keep everything else on the inspected dock. You match Microsoft 365 in a data policy and send only that application to the local internet exit. Removing the SIG tunnels, or denying the rest of the web, is a bigger cut than the pharmacy asked for.
Full Explanation
A Catalyst SD-WAN data policy can match one application and set a local internet exit for it, while traffic that does not match continues to the secure internet gateway. Microsoft 365 takes the side door. Other web flows stay inspected. A control policy that removes the SIG tunnels takes the inspected path away from everyone, which violates the request to keep other web flows on the gateway. A zone-based firewall that permits Microsoft 365 and denies every other web application blocks the rest of the web instead of steering it to the SIG. Cloud OnRamp for Multicloud attaches private cloud networks. Microsoft 365 in this design is a SaaS application on the internet, not a private virtual network the pharmacy is hosting. Exam caveat: if Cloud OnRamp for SaaS is also enabled for Microsoft 365, its path choice and this data policy have to agree or they will fight. Operational check: a Microsoft 365 flow should egress the store internet interface, and a general web flow from the same PC should still appear in the SIG inspection log.