
A retailer uses Catalyst SD-WAN Secure Internet Gateway tunnels for guest web traffic and wants that inspection path to survive one provider point of presence failing. What should they configure?
Select an answer to reveal the explanation.
Short Explanation
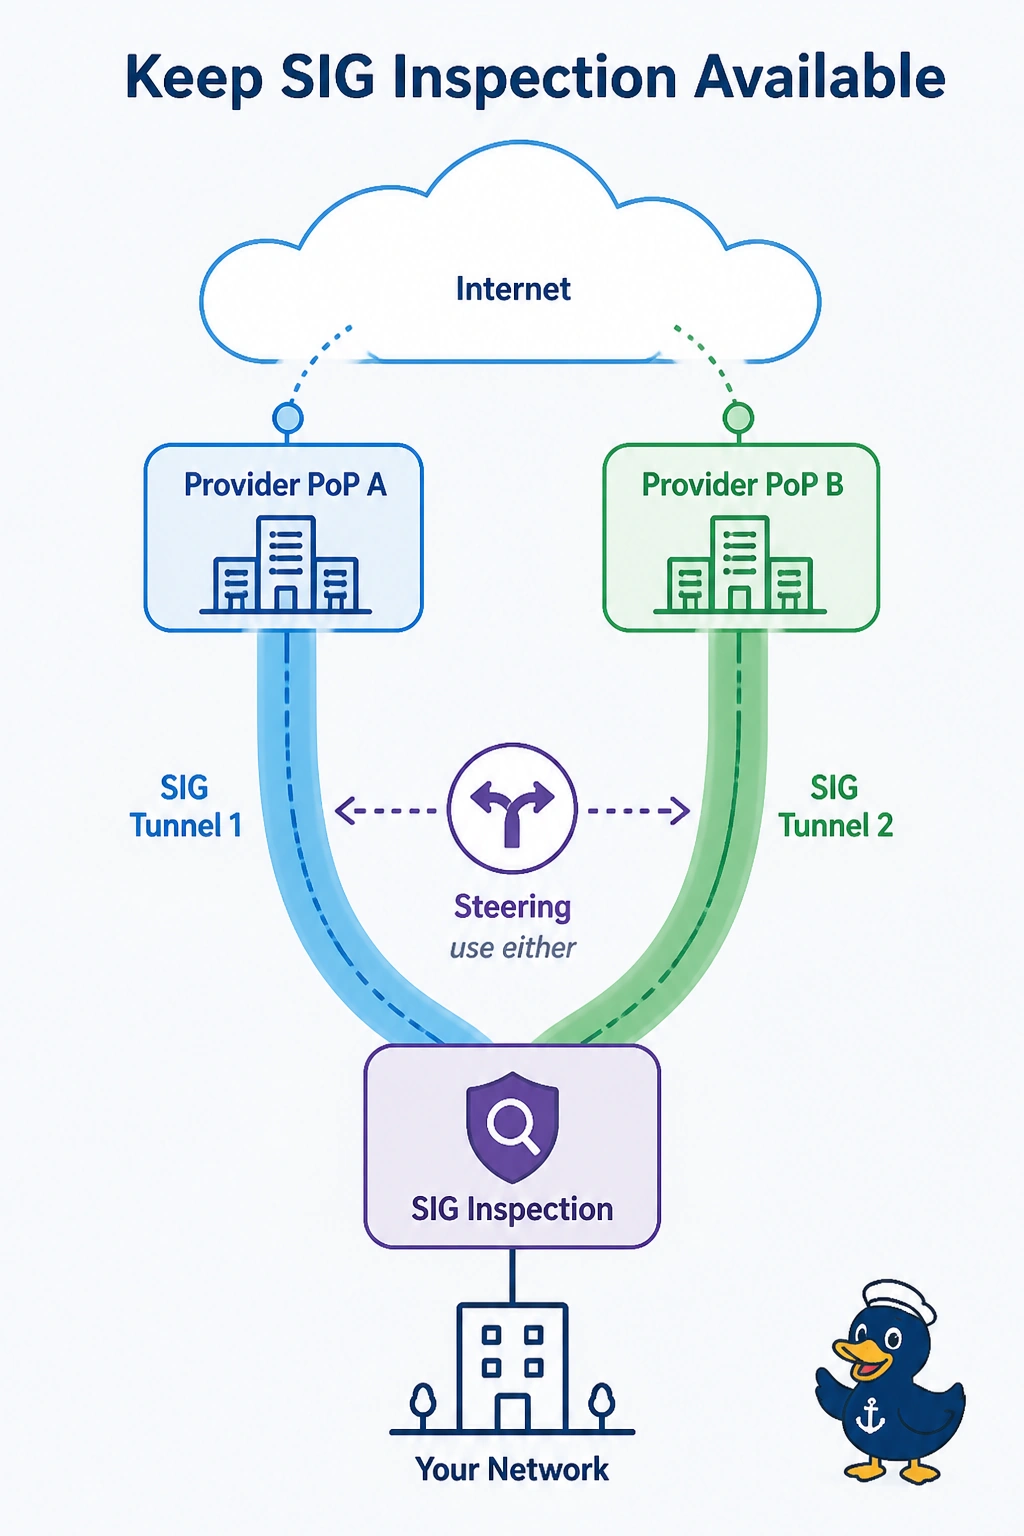
One inspection dock is a single lock on the gate. You build two SIG tunnels toward different points of presence and let steering use the one that is up. A static route out the raw internet skips the inspection the retailer still wants, and pulling every internet TLOC removes the road the tunnels ride on.
Full Explanation
The Secure Internet Gateway feature can build more than one tunnel so guest web traffic has a second provider point of presence when the first fails. Steering then uses the remaining tunnel and inspection continues. A single tunnel plus a static route to uninspected internet keeps connectivity and drops the security requirement the moment the tunnel fails. Cloud OnRamp for Multicloud attaches private cloud networks. It does not provide a second SIG point of presence, and it is not a substitute for guest web inspection. A control policy that withdraws every internet TLOC removes the underlay the SIG tunnels need. Guest web would have no path to either point of presence. Exam caveat: both tunnels should be tested, not merely configured. A second tunnel with a bad credential looks like redundancy until the first point of presence fails. Operational check: shut the primary SIG destination in a maintenance window and confirm guest web moves to the second tunnel and still appears in the provider's inspection log.